• Insight Partners, a global venture capital and private equity firm, has officially confirmed a significant data breach that exposed personal information of individuals connected to the company. The breach notification reveals sophisticated attack methods and a months-long timeline that has raised serious concerns about data security practices at one of the world’s largest investment firms. […]

    The post Insight Partners Confirms Data Breach Exposing Users’ Personal Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • SonicWall has alerted its customers to reset all login credentials after a recent leak exposed firewall configuration backups. The vendor emphasizes three critical stages—containment, remediation, and monitoring—to minimize risk and restore secure access. Users should follow each stage in order, beginning with containment to block further exposure, proceeding to remediation to reset passwords and shared […]

    The post SonicWall Advises Users to Reset Logins After Config Backup Leak appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Cybersecurity researchers have discovered two new malicious packages in the Python Package Index (PyPI) repository that are designed to deliver a remote access trojan called SilentSync on Windows systems. “SilentSync is capable of remote command execution, file exfiltration, and screen capturing,” Zscaler ThreatLabz’s Manisha Ramcharan Prajapati and Satyam Singh said. “SilentSync also extracts

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A newly discovered phishing campaign is exploiting Facebook’s external URL warning feature to dupe users into handing over their login credentials. By abusing Facebook’s “You’re about to leave Facebook” redirect mechanism, attackers can conceal malicious URLs behind the social media giant’s official domain and graphic style—making the lure appear bona fide even to cautious users. […]

    The post Hackers Target Facebook Accounts in Latest Phishing Attack appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • AI’s growing role in enterprise environments has heightened the urgency for Chief Information Security Officers (CISOs) to drive effective AI governance. When it comes to any emerging technology, governance is hard – but effective governance is even harder. The first instinct for most organizations is to respond with rigid policies. Write a policy document, circulate a set of restrictions, and

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • SonicWall has issued an urgent advisory urging all customers to perform an Essential Credential Reset after security researchers discovered that MySonicWall configuration backup files were inadvertently exposed on public storage. 

    The sensitive files contained encrypted passwords, pre-shared keys, and TLS certificates used by SonicOS appliances, potentially allowing threat actors to decrypt and leverage credentials to gain unauthorized network access. 

    SonicWall’s Knowledge Base outlines three critical phases: Containment, Remediation, and Monitoring, to mitigate risk and restore secure operations.

    Lock Down WAN-Facing Management

    To immediately reduce exposure, SonicWall recommends disabling or restricting all WAN-based management services before proceeding with password resets. 

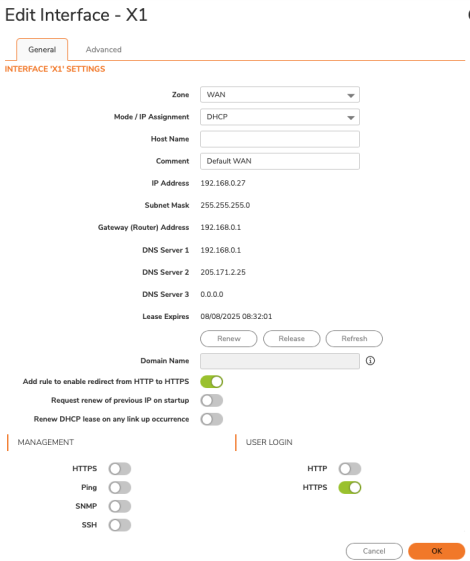
    Administrators must navigate to Network → System → Interfaces, edit each WAN interface, and disable HTTP/HTTPS & SSH Management. 

    Disable the HTTPS/SSH Management options

    Disable the HTTPS/SSH Management options

    Similarly, SSL VPN and IPsec VPN services should be turned off by accessing Network → SSL VPN → Server Settings and Network → IPsec VPN → Rules and Settings, respectively. 

    SNMP v3 access must be disabled under Device → Settings → SNMP to prevent unauthorized SNMP GET/SET commands from exposing Engine IDs or community strings. 

    Restricting inbound NAT/Access Rules to known/trusted IP addresses further prevents attackers from reconnecting after credential changes. 

    SonicOS 6.5.5.1 and 7.3.0 feature a dynamic enforcement option that blocks user accounts until a new password is set, ensuring containment remains effective even if WAN restrictions cannot be fully applied.

    Credential Reset

    Key actions include resetting passwords for all Local Users and re-enrolling TOTP bindings. 

    Administrators must update bind account passwords on LDAP, RADIUS, and TACACS+ servers, rotating shared secrets with SHA-256-hashed values. 

    Rotate shared secrets

    Rotate shared secrets

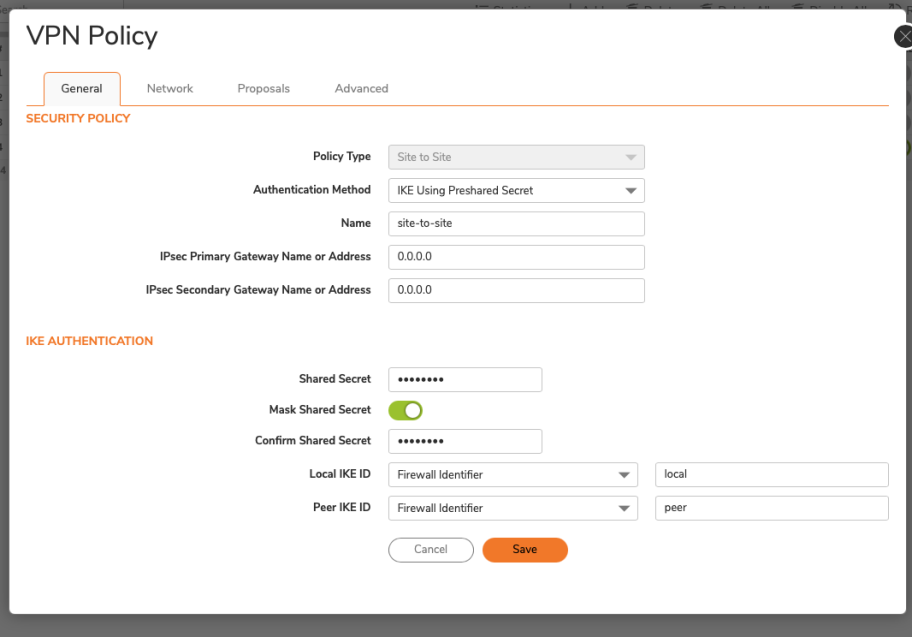
    All IPsec VPN pre-shared keys—used for both site-to-site tunnels and GroupVPN require replacement with new AES-256 encrypted secrets, with corresponding updates on remote gateways. 

    WAN interface credentials for L2TP/PPPoE/PPTP and cellular WWAN must be refreshed in coordination with ISPs. Dynamic DNS, Clearpass NAC, and email log automation accounts should have their passwords reset to avoid delivery failures. 

    Finally, update encryption keys in the Global Management System (GMS) IPSec Management Tunnel mode under Device → Settings → Administration, reads the Knowledge base.

    After remediation, re-enable services gradually, verifying each with a successful login test and SSH key rotation. Customers relying on automated workflows are reminded to update scripts referencing the old credentials.

    Continuous monitoring of the system and audit logs is essential. Administrators should review Monitor → Logs → System Logs and Audit Logs, filtering for repeated authentication failures or anomalies in configuration changes. 

    Export logs to CSV for detailed analysis, and leverage SIEM integrations using Syslog over TLS 1.2 to ensure secure forwarding. 

    Following these steps will safeguard SonicWall environments against exploitation of exposed configuration backups and reinforce the integrity of network perimeter defenses.

    Find this Story Interesting! Follow us on Google News, LinkedIn, and X to Get More Instant Updates.

    The post SonicWall Urges Customers to Reset Login Credentials After Configuration Backup Files Exposed appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The notorious Everest ransomware group has reportedly added Bayerische Motoren Werke AG (BMW) to its list of high-profile targets, alleging the theft of a trove of critical internal documents from the German automotive manufacturer.

    According to information surfaced this week, Everest claims to have exfiltrated a staggering 600,000 lines of sensitive internal data from BMW, now using the threat of public exposure as leverage for ransom negotiations.

    Everest, known for targeting organizations across multiple sectors, displayed BMW on its leak site alongside a countdown timer indicating the limited window available for negotiations before confidential files are released to the public.

    The site features sections titled “Critical BMW Audit Documents” and urgent instructions for BMW representatives, stressing the urgency by listing time-sensitive deadlines for accessing the stolen materials.

    BMW Allegedly Breached
    Countdown

    The prominent inclusion of BMW on the Everest portal has already drawn widespread attention within both cybersecurity and automotive communities.

    The gang is leveraging intimidation tactics, stating that the “recording will be available through” a countdown clock, a common method used by ransomware operators to pressure victim organizations into meeting their demands swiftly.

    The evidence provided by the Everest group reportedly includes references to internal audit files and communications, but the authenticity and full scope of the stolen documents have not yet been independently verified.

    The alleged data haul of 600,000 lines signals a significant compromise, potentially exposing financial records, audit reports, engineering documentation, and other confidential corporate information.

    Threat analysts monitoring the situation caution that the leak could not only affect BMW’s internal operations but also pose broader risks to partners, suppliers, and customers if sensitive data is published or sold on underground forums.

    Ransomware attacks targeting the automotive sector have escalated in 2025, reflecting adversaries’ growing interest in complex supply chains and high-value intellectual property.

    BMW has yet to release an official statement regarding the incident, and it remains unclear whether the company has entered negotiations with Everest or informed regulatory authorities about the alleged breach.

    Security experts urge companies to avoid direct ransom payments, work closely with law enforcement, and prioritize proactive vulnerability management.

    The Everest ransomware group’s claim against BMW, if substantiated, marks another troubling milestone in the ongoing battle against cyber extortion.

    As investigations continue, industry observers await further confirmation of the breach’s impact and potential mitigation steps taken by the automotive giant.

    Find this Story Interesting! Follow us on Google News, LinkedIn, and X to Get More Instant Updates.

    The post BMW Allegedly Breached by Everest Ransomware Group and Stolen Internal Documents appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Splunk today unveiled a comprehensive guide designed to empower security teams to detect Remote Employment Fraud (REF) during the critical onboarding phase—when imposters have already passed through HR vetting and background checks and gained network access. Building on the inaugural blog, “Imposters at the Gate: Spotting Remote Employment Fraud Before It Crosses the Wire,” this […]

    The post Splunk Publishes Guide to Spot Remote Work Fraud in Organizations appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • In recent months, cybersecurity researchers have exposed a tangled web of hidden alliances among leading ransomware operations, reshaping how defenders perceive these threats.

    Historically treated as distinct entities—Conti, LockBit, Evil Corp, and others—ransomware groups have evolved into a dynamic marketplace where code, infrastructure, and human capital flow freely between operators.

    The transformation accelerated after major disruptions such as the Conti takedown in mid-2024, forcing affiliates to scatter and rebrand under new banners.

    The result is a fractured ecosystem where attribution based solely on ransomware family names is increasingly unreliable.

    Domaintools analysts identified overlapping infrastructure footprints and shared binary artifacts that point to resource pooling rather than isolated criminal factions.

    Passive DNS records, shared SSL certificates, and duplicate command-and-control domains revealed that multiple groups have leveraged the same bulletproof hosting providers, suggesting either direct collaboration or common affiliations at the affiliate level.

    Analytical map (Source – Domaintools)

    These infrastructure overlaps underscore the necessity for defenders to track underlying assets and behaviors instead of surface-level brand labels.

    Beyond infrastructure, detailed code analysis has uncovered striking similarities in encryption routines and persistence modules.

    A comparative disassembly of the loader stages for both Black Basta and QakBot highlights identical opcode sequences in the memory-resident decryptor, indicating code reuse or direct lineage.

    In one instance, the decryption stub found in Black Basta’s initial loader closely mirrors the QakBot routine, differing only by offset values:-

    for (int i = 0; i < encryptedSize; i++) {
        decrypted[i] = encrypted[i] ^ key[(i + keyOffset) % keyLen];
    }

    This snippet illustrates how affine key indexing enables polymorphic encryption across multiple malware families, complicating signature-based detection.

    Infection Mechanism: Fileless Deployment and Persistence

    Delving deeper into the infection mechanism reveals a sophisticated fileless approach designed to evade endpoint defenses.

    Attackers first exploit exposed RDP services or phishing vectors to deploy a lightweight PowerShell loader in memory.

    Once executed, this loader uses the Windows API’s VirtualAlloc and WriteProcessMemory functions to inject a second-stage payload directly into the explorer.exe process.

    A sample persistence tactic involves writing a registry key under HKCU:\Software\Microsoft\Windows\CurrentVersion\Run that executes the loader with base64-encoded parameters at user logon.

    Domaintools researchers noted that this in-memory injection not only bypasses traditional AV scans but also leverages legitimate system binaries to blend in with normal operations.

    By understanding these hidden alliances and infection tactics, cybersecurity teams can prioritize detection of shared infrastructure and code patterns, enabling more resilient defenses against a threat landscape defined by human-driven modularity and rapid rebranding.

    Find this Story Interesting! Follow us on Google News, LinkedIn, and X to Get More Instant Updates.

    The post Researchers Uncover Hidden Connections Between Ransomware Groups and Relationships Between Them appeared first on Cyber Security News.
    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Counter Threat Unit™ (CTU) researchers are tracking a sophisticated threat actor known as Warlock Group, which CTU designates as GOLD SALEM. Since March 2025, the group has compromised enterprise networks and bypassed security solutions to deploy its custom Warlock ransomware. While Microsoft refers to this collective as Storm-2603 and associates it “with moderate confidence to […]

    The post Warlock Ransomware Deployed via Compromised GOLD SALEM Networks and Bypassed Security Solutions appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶