• AzureHound, an open-source data collection tool designed for legitimate penetration testing and security research, has become a favored weapon in the hands of sophisticated threat actors.

    The tool, which is part of the BloodHound suite, was originally created to help security professionals and red teams identify and fix cloud vulnerabilities.

    However, malicious actors have increasingly misused this capability to map out Azure environments and discover pathways for privilege escalation attacks.​

    The tool operates by collecting data through Microsoft Graph and Azure REST Application Programming Interfaces (APIs), allowing it to enumerate Entra ID and Azure environments to gather information about identities and resources.

    Written in the Go programming language and available as precompiled versions for Windows, Linux, and macOS, AzureHound proves particularly dangerous because it does not need to be run from within a victim’s network.

    Since both APIs are accessible externally, threat actors can launch discovery operations remotely after gaining initial access to compromised systems.​

    How Threat Actors Weaponize the Tool

    When threat actors gain access to a victim’s Azure environment, they deploy AzureHound to automate discovery procedures that would otherwise require extensive manual effort.

    The tool helps attackers discover user hierarchies, identify high-value targets, and uncover misconfigurations or indirect privilege escalation opportunities that might otherwise remain hidden.
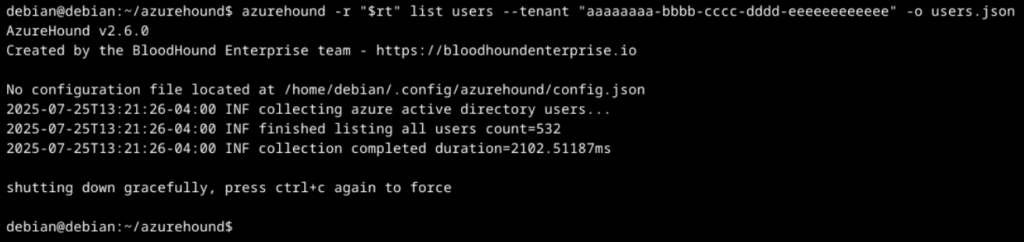
    Execution of AzureHound to enumerate users.
    Execution of AzureHound to enumerate users

    By gathering comprehensive internal Azure information, attackers can develop targeted attack strategies with surgical precision.​ The tool outputs data in JSON format, which can be ingested by BloodHound’s visualization capabilities.

    This creates a graphical representation of hidden relationships and attack paths within the target’s infrastructure, giving attackers a complete roadmap of the environment they have infiltrated.

    This combination of automated discovery and visual analysis transforms cloud reconnaissance from a time-consuming process into an efficient operation. Recent threat intelligence reveals the widespread adoption of AzureHound across multiple adversary groups.
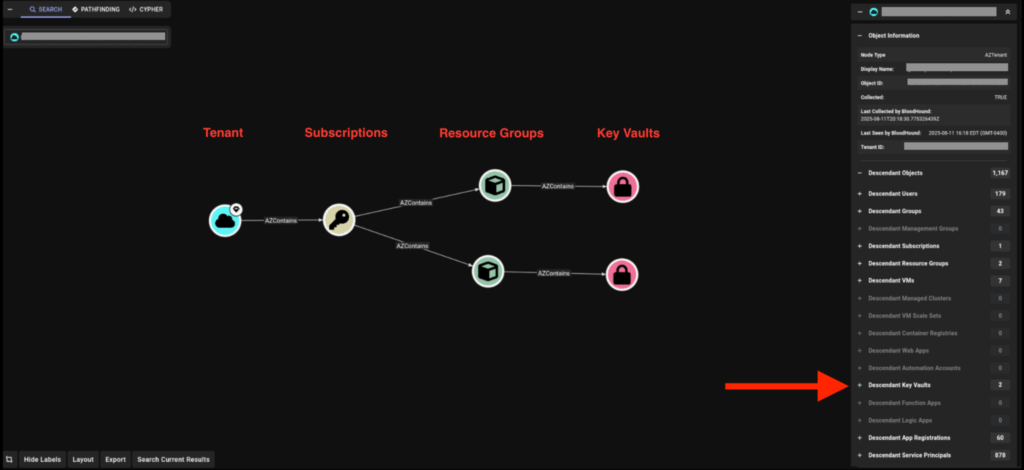
    BloodHound illustration of available key vaults.
    BloodHound illustration of available key vaults

    Unit 42 researchers have tracked the Iranian-backed group Curious Serpens, also known as Peach Sandstorm and active since at least 2013, leveraging AzureHound to conduct internal discovery operations against target Microsoft Entra ID environments.​

    In May 2025, Microsoft disclosed that suspected nation-state threat actor Void Blizzard employed AzureHound during the discovery phase of their campaigns to enumerate Entra ID configurations.

    More recently, in August 2025, Microsoft reported Storm-0501, a ransomware operator, using AzureHound to enumerate target Entra ID tenants while operating in hybrid, multi-tenant Azure environments.​

    Organizations using Azure and Microsoft Entra ID must recognize that tools like AzureHound leave detectable evidence when used maliciously.

    Security teams should focus on detecting abnormal API activity, monitoring for suspicious enumeration patterns, and implementing strong identity and access controls.
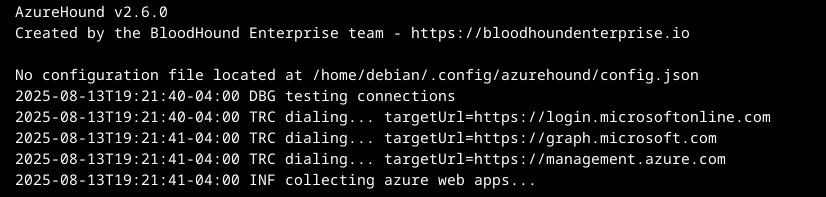
    AzureHound API test requests
    AzureHound API test requests

    Understanding how threat actors misuse legitimate tools is essential for building effective detection capabilities and responding quickly to compromise indicators in cloud environments.

    Follow us on Google News, LinkedIn, and X for daily cybersecurity updates. Contact us to feature your stories.

    The post AzureHound Penetration Testing Tool Weaponized by Threat Actors to Enumerate Azure and Entra ID appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The Cybersecurity and Infrastructure Security Agency (CISA) has raised alarm over active exploitation of a critical privilege escalation vulnerability affecting Broadcom’s VMware Tools and VMware Aria Operations. Tracked as CVE-2025-41244, this 0-day flaw poses significant risk to organizations managing virtualized infrastructure, potentially allowing attackers to gain root-level access to compromised systems. CVE ID Vendor Affected […]

    The post CISA Alerts on Active Exploitation of VMware Tools and Aria Operations 0-Day appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • North Korean state-sponsored threat actors have escalated their cyber operations with the deployment of sophisticated new malware variants designed to establish persistent backdoor access to compromised systems. Recent investigations by threat intelligence researchers have uncovered two distinct toolsets from prominent DPRK-aligned hacking groups: Kimsuky’s newly identified HttpTroy backdoor and an upgraded version of Lazarus’s BLINDINGCAN […]

    The post Kimsuky and Lazarus Hackers Deploy New Backdoor Tools for Remote Access Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent warning about a severe injection vulnerability in the XWiki Platform, designated as CVE-2025-24893.

    This flaw allows unauthenticated attackers to execute arbitrary remote code, posing significant risks to organizations using the open-source wiki software.

    Discovered and actively exploited, the vulnerability underscores the dangers of eval injection in web applications, particularly those handling search functionalities.

    XWiki, a popular platform for collaborative content management, suffers from this eval injection issue in its SolrSearch feature. Attackers can exploit it without logging in, potentially compromising entire installations.

    CISA added the CVE to its Known Exploited Vulnerabilities catalog on October 30, 2025, emphasizing the need for immediate action amid reports of real-world exploitation.

    While it’s unclear if ransomware groups are leveraging it specifically, the flaw’s severity aligns with tactics seen in broader campaigns targeting content management systems.

    Vulnerability Mechanics and Impact

    At its core, CVE-2025-24893 stems from improper handling of user input in the SolrSearch endpoint, classified under CWE-95 for improper neutralization of directives in dynamically evaluated code. Any guest user can send a crafted request to trigger code execution.

    For instance, a simple test involves accessing the SolrSearch RSS feed with a payload like %7D%7D%7D%7B%7Basync async=false%7D%7D%7B%7Bgroovy%7D%7Dprintln(“Hello from” + ” search text:” + (23 + 19))%7B%7B/groovy%7D%7D%7B%7B/async%7D%7D. If the response includes “Hello from search text:42” in the RSS title, the instance is vulnerable.

    The impact is devastating: complete remote code execution undermines confidentiality, integrity, and availability. Attackers could steal data, deploy malware, or pivot to other systems.

    Affected versions include those prior to the patches, primarily impacting enterprise users in education, government, and corporate sectors who rely on XWiki for internal knowledge bases.

    CVE IDDescriptionAffected Products/VersionsCVSS 3.1 ScoreCWEExploitation Status
    CVE-2025-24893Eval injection in SolrSearch allowing arbitrary RCEXWiki Platform < 15.10.11, < 16.4.1, < 16.5.0RC19.8 (Critical)CWE-95Actively exploited in the wild

    Mitigations

    CISA urges users to promptly apply vendor mitigations, adhere to Binding Operational Directive 22-01 for cloud services, or discontinue use of the product if patches are unavailable.

    XWiki has released fixes in versions 15.10.11, 16.4.1, and 16.5.0RC1, which sanitize inputs and prevent eval execution.

    As a temporary workaround, administrators can modify the Main.SolrSearchMacros file, specifically line 955, to enforce an application/xml content type for the rawResponse macro, mirroring the template’s secure output handling.

    This blocks malicious payloads without a full upgrade. Organizations should also monitor logs for suspicious SolrSearch requests and restrict guest access where possible.

    This incident highlights the ongoing threats to legacy web platforms. With exploitation confirmed, swift patching remains critical to safeguard sensitive environments.

    Follow us on Google News, LinkedIn, and X for daily cybersecurity updates. Contact us to feature your stories.

    The post CISA Warns of XWiki Platform Injection vulnerability Exploited to Execute Remote Code appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added a high-severity security flaw impacting Broadcom VMware Tools and VMware Aria Operations to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation in the wild. The vulnerability in question is CVE-2025-41244 (CVSS score: 7.8), which could be exploited by an attacker to attain

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • In an unprecedented cybersecurity incident that occurred in September 2025, over 500 gigabytes of internal data from China’s Great Firewall infrastructure were exposed in what security experts are calling one of the most consequential breaches in digital surveillance history.

    The massive leak encompasses more than 100,000 documents, including internal source code, work logs, configuration files, emails, technical manuals, and operational runbooks from Chinese infrastructure firms associated with the censorship apparatus.

    The exposed material reveals the technical scaffolding behind China’s digital surveillance regime, containing raw IP access logs from state-run telecom providers such as China Telecom, China Unicom, and China Mobile.

    The dataset provides unprecedented visibility into real-time traffic monitoring and endpoint interaction protocols, offering researchers a multidimensional forensic cross-section of the Great Firewall’s operational anatomy.

    Far from being an accidental disclosure, this archive represents a curated corpus likely compiled over an extended period, suggesting either a trusted insider with comprehensive access or a methodical external data exfiltration campaign.

    The breach reveals critical vulnerabilities within China’s distributed enforcement model, exposing moments where the censorship apparatus faltered.

    DomainTools analysts noted that multiple instances of cross-border leakage routes allowed foreign IP addresses to establish unfiltered sessions for extended periods, indicating delays in rule propagation, temporary policy gaps, or failures in heuristic detection systems.

    These lapses demonstrate that while the system maintains high surveillance capabilities, it remains reactive and inconsistently enforced across different regions.

    Among the most sensitive exposed artifacts are packet captures (PCAPs) and routing tables paired with blackhole sinkhole exports, detailing how traffic is intercepted, redirected, or silently dropped.

    Excel spreadsheets enumerate known VPN IP addresses, DNS query patterns, SSL certificate fingerprints, and behavioral signatures of proxy services, providing insight into identification and blocking heuristics.

    The dataset also contains Visio diagrams mapping internal firewall architecture from hardware deployments to logical enforcement chains spanning various ministries and provinces.

    Metadata Exposure and Attribution Tracking

    The leak’s most strategically valuable component lies in the accidentally embedded metadata across thousands of files, offering unprecedented visibility into the human and organizational machinery behind China’s censorship apparatus.

    Network Topology (Source – Domaintools)

    The dump exposes dozens of unique usernames following consistent naming conventions indicative of internal departmental hierarchies, including system-level account names and author tags in Office documents that enable correlation to individual operators.

    Authorship data and revision histories link technical documents to specific personnel across government agencies, telecom subsidiaries, and third-party contractors.

    System Status Network Topology (Source – Domaintools)

    Cross-referencing these metadata fields with known Chinese corporate entities and state-linked research institutes has enabled the construction of preliminary attribution clusters showing clear ties to China’s major telecommunications providers and academic partners, including digital forensics laboratories and infrastructure vendors with suspected MSS connections.

    Multiple files retain internal IP address references and machine hostnames mapped to sandbox and testbed environments used for evaluating censorship evasion tools, including systems specifically tagged for analyzing Psiphon, V2Ray, and Shadowsocks protocols.

    Some remote server addresses and reverse-proxy logs point to Great Firewall staging zones used to pilot domain interdiction and traffic shaping prior to national deployment.

    The organizational fingerprints reveal a complex lattice of state-linked entities operating in tightly controlled silos, with core traffic monitoring and enforcement responsibilities handled by major telecommunications providers whose infrastructure appears repeatedly in PCAP logs, IP registries, and system-level telemetry.

    This breach fundamentally shifts the asymmetry between censor and censored, providing detailed blueprints of China’s digital surveillance infrastructure for the first time in history.

    Follow us on Google News, LinkedIn, and X to Get More Instant Updates, Set CSN as a Preferred Source in Google.

    The post Historic Great Firewall Breach – 500GB+ Censorship Data Exposed appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • In a historic breach of China’s censorship infrastructure, over 500 gigabytes of internal data were leaked from Chinese infrastructure firms associated with the Great Firewall (GFW) in September 2025. Researchers now estimate the full dump is closer to approximately 600 GB, with a single archive comprising around 500 GB alone. The material includes more than […]

    The post Massive Great Firewall Leak Exposes 500GB of Censorship Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • WhatsApp has unveiled passkey-encrypted backups, simplifying the protection of cherished chat histories without the burden of memorizing complex passwords.

    This feature allows users to secure their end-to-end encrypted backups using biometric methods like fingerprints, facial recognition, or device screen locks, ensuring seamless access even after losing a phone or switching devices.

    Announced on October 29, 2025, the update addresses a long-standing pain point for the app’s over three billion users, who often store years of photos, voice notes, and conversations in backups on Google Drive or iCloud.​

    Passkeys represent a passwordless authentication evolution, leveraging device-specific biometrics to generate unique cryptographic keys that remain secure on the user’s hardware.

    Unlike the previous system introduced in 2021, which required a custom password or a cumbersome 64-digit encryption key, this new method integrates directly with the phone’s built-in security features for effortless encryption.

    WhatsApp Passkey Encryption for Chat

    Users can now encrypt backups with a simple tap or glance, applying the same robust end-to-end encryption that safeguards live chats and calls against access by WhatsApp, Meta, or third-party cloud providers.

    This innovation not only enhances convenience but also reduces risks associated with forgotten credentials, which previously could lock users out of their data entirely.

    Security experts note that passkeys are more resistant to phishing and credential stuffing attacks than traditional passwords, making them a forward-thinking choice for mobile messaging.​

    With cyber threats escalating, including recent spyware exploits targeting messaging apps, protecting stored data has never been more critical.

    WhatsApp’s encrypted backups ensure that personal memories and sensitive exchanges remain private, even if a device is compromised or stolen. The feature builds on the platform’s pioneering 2021 rollout of end-to-end encryption for backups, which now secures over 100 billion daily messages for two billion users.

    By eliminating reliance on easily lost keys, passkeys democratize advanced security, empowering non-technical users to maintain privacy without compromising on protection.

    This move aligns with broader industry trends toward biometric and zero-knowledge authentication, potentially setting a standard for other apps handling personal data.​

    The passkey encryption will deploy gradually worldwide on iOS and Android over the coming weeks and months, starting with the latest app versions. To enable it, users should navigate to Settings > Chats > Chat backup > End-to-end encrypted backup and select the passkey option.

    WhatsApp encourages immediate updates to stay ahead of the rollout, emphasizing that this enhancement keeps backups as secure and accessible as everyday chats.

    Follow us on Google News, LinkedIn, and X for daily cybersecurity updates. Contact us to feature your stories.

    The post WhatsApp Introduces Passkey Encryption for Enhanced Chat Message Backup Security appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Security researchers have uncovered a sophisticated attack vector that exploits how AI search tools and autonomous agents retrieve web content. The vulnerability, termed “agent-aware cloaking,” allows attackers to serve different webpage versions to AI crawlers like OpenAI’s Atlas, ChatGPT, and Perplexity while displaying legitimate content to regular users. This technique represents a significant evolution of […]

    The post New Agent-Aware Cloaking Technique Uses ChatGPT Atlas Browser to Feed Fake Content appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The Cybersecurity and Infrastructure Security Agency (CISA), working alongside the National Security Agency and international cybersecurity partners, has released a comprehensive security guidance document focused on hardening Microsoft Exchange servers against evolving threats. The Microsoft Exchange Server Security Best Practices guide aims to help network defenders and IT administrators strengthen their on-premises Exchange infrastructure and […]

    The post CISA Publishes New Guidance to Strengthen Microsoft Exchange Server Security appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶