• Exposure Management is a proactive cybersecurity discipline that systematically identifies, assesses, prioritizes, and remediates security vulnerabilities and misconfigurations across an organization’s entire attack surface both internal and external.

    Unlike traditional, periodic vulnerability scanning, EM leverages continuous monitoring, threat intelligence, and a holistic, graph-based view of risk to anticipate and neutralize potential attack paths before adversaries can exploit them.

    It is the practical application of the Continuous Threat Exposure Management (CTEM) framework, which defines a cyclical five-step process: Scoping, Discovery, Prioritization, Validation, and Mobilization.

    The core value of an EM platform lies in its ability to consolidate findings from diverse security tools (such as vulnerability scanners, cloud posture management, and EDR) and enrich them with business context (e.g., asset criticality, owner) and attacker context (e.g., exploitability in the wild).

    This consolidation drastically reduces alert fatigue by focusing security teams on the few exposures that pose the greatest, most exploitable risk to the business, rather than a massive, unprioritized list of Common Vulnerabilities and Exposures (CVEs).

    Ultimately, EM drives measurable reduction in the organizational risk posture and improves the efficiency of security operations.

    How We Choose An Exposure Management Tools

    Selecting the right Exposure Management Tool requires a strategic approach focused on holistic coverage, actionable intelligence, and seamless integration with existing Security Operations Center (SOC) workflows.

    Our methodology for evaluating the top tools is based on several key criteria:

    1. Scope and Discovery Coverage: The tool must offer comprehensive, continuous discovery of all assets including known, unknown (Shadow IT), and third-party/vendor-related assets—across the full spectrum of modern infrastructure (on-premise, multi-cloud, SaaS, and code). Look for agentless and API-based scanning capabilities for minimal friction.
    2. Risk Prioritization & Context: The platform’s ability to prioritize vulnerabilities must go beyond simple severity scores (CVSS). The best tools use a risk-based approach incorporating:
      • Attacker Context: Real-time threat intelligence on active exploitation.
      • Business Context: Asset criticality, data sensitivity, and owner.
      • Attack Path Visualization: Mapping how an exposure can be chained with others to create an end-to-end attack path.
    3. Validation and Remediation Integration: A top-tier tool validates whether an exposure is actually exploitable (often via integrated Breach and Attack Simulation – BAS) and provides clear, actionable remediation guidance, including one-click fixes or direct integration with ticketing/workflow systems (like Jira, ServiceNow) to accelerate Mean Time to Remediate (MTTR).
    4. Scalability and Architecture: The solution must be highly scalable to accommodate a dynamic, rapidly expanding digital footprint, especially in cloud-native environments.
      • A cloud-native, agentless architecture often simplifies deployment and reduces operational overhead.

    Comparison Table: Top 10 Best Exposure Management Tools In 2026

    Tool NameExternal Attack Surface Management (EASM)Cloud Attack Surface Management (CASM)Breach & Attack Simulation (BAS)Risk-Based PrioritizationAgentless Deployment
    Mandiant✅ Yes✅ Yes (Multi-Cloud)❌ No (Focus on Intel)✅ Yes✅ Yes
    Wiz❌ No (Focus on Cloud)✅ Yes (Cloud-Native)❌ No✅ Yes✅ Yes
    RiskProfiler✅ Yes✅ Yes (Multi-Cloud)❌ No✅ Yes✅ Yes
    CrowdStrike Falcon✅ Yes✅ Yes (via Falcon)❌ No✅ Yes❌ No (Sensor-based)
    Tenable One✅ Yes✅ Yes (Multi-Cloud)❌ No✅ Yes✅ Yes / ❌ No (Hybrid)
    Qualys✅ Yes✅ Yes (via VMDR)❌ No✅ Yes✅ Yes
    CyCognito✅ Yes (Attacker’s View)✅ Yes❌ No✅ Yes✅ Yes
    Microsoft Defender✅ Yes (External focus)✅ Yes (via Defender)❌ No✅ Yes✅ Yes
    Cymulate✅ Yes (via Discovery)✅ Yes (via Validation)✅ Yes (Core Feature)✅ Yes✅ Yes / ❌ No (Hybrid)
    Bitsight✅ Yes✅ Yes (Cloud Configs)❌ No✅ Yes✅ Yes

    1. Mandiant

    Best Exposure Management Tools
    Mandiant

    Why We Picked It

    Mandiant is chosen for its world-class, frontline threat intelligence, which directly informs its risk prioritization engine.

    This allows organizations to prioritize exposures that Mandiant’s consultants know adversaries are actively exploiting in real-world attacks.

    Specifications & Features

    • Intel-Informed Checks: Uses Mandiant’s own threat intelligence for active and passive checks of external assets.
    • Continual Asset Discovery: Automated, continuous discovery and inventory of internet-facing assets, including Shadow IT.
    • Multicloud Assessment: Ability to assess cloud-hosted external assets and unify visibility across hybrid/multicloud.
    • Centralized Risk Mitigation: Consolidates visibility and provides clear paths for remediation, driven by threat context.

    Reason to Buy

    You need an exposure management tool that is directly fed by the industry’s most current, credible, and real-world attacker intelligence to ensure your security team focuses exclusively on the most exploitable risks.

    Pros & Cons

    • Pros: Direct integration with Mandiant’s proprietary threat intel; Strong external focus and shadow IT detection; Effective for large, complex enterprises.
    • Cons: Less focus on integrated validation (BAS) than some competitors; Pricing can be complex; May require Mandiant-specific expertise for full value.

    ✅ Best For: Enterprises prioritizing real-world threat intelligence and wanting an outside-in, attacker’s view of their external attack surface.

    Official Home Page: Mandiant Attack Surface Management

    2. Wiz

    Best Exposure Management Tools
    Wiz

    Why We Picked It

    Wiz is the undisputed leader in Cloud Security Posture Management (CSPM) and has expanded to offer deep exposure management features rooted in its unique, agentless Security Graph.

    It’s ideal for organizations that are cloud-first or heavily invested in multi-cloud environments.

    Specifications & Features

    • Agentless-First Scanning: Provides 100% coverage of the cloud environment without agents, using API and snapshot reading.
    • Graph-Based Risk Prioritization: Correlates security findings across workloads, network, identity, and data to identify critical attack paths.
    • Unified Vulnerability Management: Centralizes and prioritizes vulnerabilities across cloud, code, and on-premises using the same context model.
    • Shift-Left Capabilities: Integrates with code (SAST/DAST) tools to find and fix vulnerabilities early in the development lifecycle.

    Reason to Buy

    Your primary risk is in the cloud, and you need a consolidated, context-aware platform that can identify exploitable security gaps that span across multiple cloud resources, identities, and data stores.

    Pros & Cons

    • Pros: Deepest cloud security context and coverage; Exceptional ease of deployment (agentless); Industry-leading Security Graph technology; Excellent for modern DevOps pipelines.
    • Cons: Originally cloud-centric, with less native EASM/on-prem heritage; Can be expensive for smaller operations; Remediation often relies on integrations.

    ✅ Best For: Cloud-Native and Multi-Cloud organizations that need to prioritize risk based on exploitability within the cloud environment.

    Official Home Page: Agentless Cloud Vulnerability Management - Wiz

    3. RiskProfiler

     cloud attack surface management
    RiskProfiler

    Why We Picked It

    RiskProfiler is selected for its focus on providing a unified view of risk that extends beyond the organization’s perimeter to include third-party vendor risk and brand risk (phishing, impersonation), making it a comprehensive CTEM solution.

    Specifications & Features

    • Unified CTEM Ecosystem: Consolidates External, Cloud, Vendor, and Brand risk into a single platform.
    • Brand Risk Protection: Monitors for brand impersonation, typosquats, phishing, and fake apps.
    • AI-Enabled Third-Party Risk Management: Automates the exchange and scoring of vendor security questionnaires.
    • Context-Based Graph Models: Pinpoints and ranks exposed assets by evaluating risks through a hacker’s lens.

    Reason to Buy

    You need to manage your total external risk, including the exposure introduced by supply chain vendors and threats to your brand reputation outside of your technical infrastructure.

    Pros & Cons

    • Pros: Strong integration of third-party risk management; Dedicated brand protection features; Contextual threat insights for prioritization; Unified view across four major risk domains.
    • Cons: Focus is heavily external, may require other tools for deep internal security; Smaller market presence compared to industry giants; Initial setup for all modules can be complex.

    ✅ Best For: Organizations with significant third-party vendor reliance and high exposure to brand-related threats (phishing, impersonation).

    Official Home Page: RiskProfiler - External Threat Exposure Management

    4. CrowdStrike Falcon

     cloud attack surface management
    CrowdStrike Falcon

    Why We Picked It

    CrowdStrike is included for its ability to integrate Exposure Management natively within the Falcon platform, leveraging its ubiquitous single, lightweight sensor for real-time asset discovery and vulnerability assessment across the internal and external attack surface.

    Specifications & Features

    • Unified Falcon Sensor: Uses a single, lightweight agent for real-time, maintenance-free vulnerability assessment and continuous visibility.
    • AI-Powered Asset Criticality: Automatically classifies assets (Critical, High, Non-Critical) based on business context and peer insights.
    • Full Lifecycle Vulnerability Management: Covers asset discovery, assessment, prioritization, and effective remediation within a single product.
    • Active, Passive, & API Discovery: Discovers all assets, including sensorless devices (routers, IoT), without traditional network scanning appliances.

    Reason to Buy

    You are already a CrowdStrike customer and want to consolidate your endpoint security, threat intelligence, and exposure management into a single, high-performance platform with minimal footprint.

    Pros & Cons

    • Pros: Real-time visibility without scan windows; Excellent threat intelligence integration; Reduces the need for multiple security agents; Seamlessly integrates with EDR/XDR workflows.
    • Cons: Heavily reliant on the Falcon sensor (not fully agentless); Primarily focuses on the asset visibility the sensor can provide; Higher cost for the full unified platform.

    ✅ Best For: Organizations committed to the CrowdStrike Falcon platform who prioritize real-time, continuous visibility over periodic scanning.

    Official Home Page: Falcon Exposure Management - CrowdStrike

    5. Tenable

    Mandiant attack surface
    Tenable

    Why We Picked It

    Tenable is a long-standing leader in Vulnerability Management (VM) that has successfully pivoted to the holistic Exposure Management model with its Tenable One platform, offering deep, comprehensive coverage across IT, cloud, and operational technology (OT).

    Specifications & Features

    • Converged Exposure Platform: Unifies data from Tenable’s VM, EASM, Cloud Security, and AD Security products.
    • Predictive Prioritization Scoring (PPS): Uses machine learning to anticipate which vulnerabilities are most likely to be exploited in the near future.
    • Unified Attack Surface Visualization: Provides a consolidated view of the entire attack surface and the paths an attacker could take.
    • Broadest Asset Coverage: Includes IT, Web Apps, OT, Cloud, and Active Directory security posture.

    Reason to Buy

    You require a solution from a trusted VM vendor that offers the broadest coverage of assets and the ability to leverage predictive analytics to prioritize remediation based on future exploit likelihood.

    Pros & Cons

    • Pros: Deepest history and coverage in core vulnerability management; Strong support for diverse environments (OT/AD); Predictive risk scoring for proactive prioritization; High potential for upselling existing Tenable customers.
    • Cons: Can be perceived as scan-heavy (though API-based for cloud); Platform integration is newer than individual products; Transitioning from a VM mindset to an EM mindset can be a learning curve.

    ✅ Best For: Large enterprises seeking to consolidate and modernize their legacy vulnerability and asset management programs under a single, unified exposure platform.

    Official Home Page: Tenable One Exposure Management

    6. Qualys

    Mandiant attack surface
    Qualys

    Why We Picked It

    Qualys is a veteran in the security space that has tightly integrated its External Attack Surface Management (EASM) into its comprehensive Cloud Platform, providing a seamless “outside-in” and “inside-out” view for existing customers.

    Specifications & Features

    • EASM as a Feature: Provides an outside-in view of internet-facing assets within the Qualys Cloud Platform (CSAM).
    • Continuous Monitoring: Continuously monitors the external attack surface to discover new domains, unsolicited ports, certificates, and applications.
    • Asset Discovery: Discovers all domains, subdomains, and associated assets, including unknown/unmanaged assets.
    • Integration with VMDR: Directly feeds EASM findings into the Vulnerability Management, Detection, and Response (VMDR) workflow for prioritization and remediation.

    Reason to Buy

    You are a current Qualys customer looking to extend the reach of your existing security platform to continuously discover and manage your external digital footprint and integrate findings with a familiar VMDR workflow.

    Pros & Cons

    • Pros: Deep integration with the Qualys ecosystem; Comprehensive visibility of external assets; Robust for large organizations with complex IT infrastructure; Consolidates EASM under a single vendor.
    • Cons: EASM features can feel like an add-on to the VMDR core; Full feature set requires adoption of the full Qualys Cloud Platform; Initial EASM feature may have started as a beta.

    ✅ Best For: Existing Qualys Cloud Platform users who want to centralize EASM and vulnerability data under a single vendor.

    Official Home Page: External Attack Surface Management - Qualys

    7. CyCognito

     attack path visualization
    CyCognito

    Why We Picked It

    CyCognito stands out for its attacker-centric approach, which automatically discovers and tests all internet-exposed assets (both known and unknown) from the perspective of a malicious actor, prioritizing risks based on the probability and impact of exploitation.

    Specifications & Features

    • Attacker-Centric Discovery: Discovers all internet-exposed assets to build a complete picture of the attack surface from the outside.
    • Automated Security Testing: Automatically detects and validates potential attack vectors across the external IT ecosystem.
    • Business Context Mapping: Graphs asset relationships and determines business context (owner, purpose, data sensitivity) for better prioritization.
    • Comprehensive Prioritization: Ranks attack vectors based on attacker priorities, business context, ease of exploitation, and remediation complexity.

    Reason to Buy

    You need an EM solution that goes beyond inventorying assets to actively and continuously testing them for exploitable flaws, helping you see and fix your exposure exactly as an attacker would.

    Pros & Cons

    • Pros: Powerful, continuous security testing at scale; Strong focus on unknown/unmonitored assets; Prioritization based on attacker logic; Provides clear remediation guidance.
    • Cons: Not a traditional internal vulnerability scanner; Focus is heavily on the external/perimeter attack surface; Higher price point reflective of its advanced testing capabilities.

    ✅ Best For: Organizations that prioritize continuous, active security testing and require an outside-in, attacker-focused view of their risk.

    Official Home Page: Exposure Management - CyCognito

    8. Microsoft Defender

     attack path visualization
    Microsoft Defender

    Why We Picked It

    Microsoft is a strategic choice for its deep integration into the Microsoft Defender suite and its ability to provide a comprehensive view of external risks by leveraging Microsoft’s vast threat intelligence and cloud infrastructure presence.

    Specifications & Features

    • Attack Surface Discovery: Maps the organization’s external attack surface by identifying all internet-facing assets, services, and applications.
    • Threat Intelligence Integration: Leverages up-to-date Microsoft threat intelligence feeds for proactive threat identification and response.
    • Automated Vulnerability Assessment: Automates the assessment of external defenses to find and address weaknesses.
    • Integration with Defender Ecosystem: Seamlessly works with other Microsoft Defender components (e.g., EDR, Cloud Security Posture Management) for unified security.

    Reason to Buy

    You are heavily invested in the Microsoft ecosystem (Azure, M365) and need a native, integrated EM solution that leverages your existing tools and Microsoft’s global threat intelligence network.

    Pros & Cons

    • Pros: Unbeatable integration for Microsoft shops; Leverages Microsoft’s massive threat intelligence; Cost-friendly for existing Defender customers; Strong security monitoring and protection.
    • Cons: Initial setup and integration can be complicated for varied IT environments; Limited for non-Microsoft-centric cloud/infrastructure; Features may be more limited than best-of-breed EASM pure-plays.

    ✅ Best For: Organizations that have standardized on the Microsoft Defender suite and utilize Microsoft Azure/Cloud services.

    Official Home Page: Microsoft Defender External Attack Surface Management

    9. Cymulate

    Tenable One exposure platform
    Cymulate

    Why We Picked It

    Cymulate is unique on this list because its core strength is Breach and Attack Simulation (BAS) and Exposure Validation, enabling organizations to continuously test their defenses against the latest adversarial techniques and validate that an exposure is truly a risk.

    Specifications & Features

    • BAS/Exposure Validation Core: Continuously tests security controls across the full kill chain using automated, live, offensive testing.
    • AI-Assisted Custom Testing: Allows users to create realistic, multi-stage attack chains from plain language prompts or threat advisories (Purple Teaming).
    • Optimized Remediation: Provides actionable guidance, including control-ready threat updates and custom detection rules for SIEM/EDR platforms.
    • Cyber Resilience Metrics: Delivers a unified, measurable view of security posture, benchmarked against industry peers.

    Reason to Buy

    You need to move beyond simple vulnerability discovery to empirically validate if your security controls (firewalls, EDR, SIEM rules) are actually working against current threats and prioritize only those exposures that validation proves are exploitable.

    Pros & Cons

    • Pros: Core focus on validation (BAS/CTEM step 4); Automated Purple Teaming capabilities; Provides quantitative, board-ready cyber resilience metrics; Excellent for optimizing and tuning existing security tools.
    • Cons: External Attack Surface Discovery is a supporting feature rather than the core focus; Requires strong integration with other discovery/scanner tools for full EM value; Requires expertise to leverage the full BAS potential.

    ✅ Best For: Security teams that need to validate, optimize, and prove the effectiveness of their existing security controls against real-world threats (CTEM Validation).

    Official Home Page: Cymulate Exposure Validation

    10. Bitsight

    Tenable One exposure platform
    Bitsight

    Why We Picked It

    Bitsight is known for its market-leading Security Ratings and brings that proprietary risk scoring and analytics model to its EASM platform, offering unmatched signal quality and contextual intelligence for external risks and third-party risk management.

    Specifications & Features

    • Unmatched Signal Quality: Leverages behavioral analytics and telemetry from billions of daily events to identify true exposures with high precision.
    • Integrated Third-Party Risk: Extends EASM visibility and risk scoring to third-party vendors and supply chain partners.
    • Daily Discovery Cadence: Automated, daily discovery and classification of new or changed internet-facing assets.
    • Integration with GRC/SOC Workflows: Provides data for rapid response and allows for integration with workflow tools like Jira and ServiceNow.

    Reason to Buy

    Your primary driver is a quantifiable, data-driven security rating for both your own organization and your entire supply chain, driven by high-quality external risk data and analytics.

    Pros & Cons

    • Pros: Industry-leading security ratings and risk quantification; Excellent for third-party risk management; Daily and automated asset discovery; Strong reporting and governance (GRC) focus.
    • Cons: Licensing model can be complex; Historically focused on ratings, the EASM platform is a newer extension; Less of an internal, post-exploitation focus than some other platforms.

    ✅ Best For: Risk and Governance (GRC) teams that need quantitative security ratings and highly accurate, data-driven external exposure management for themselves and their vendors.

    Official Home Page: External Attack Surface Management - BitSight Technologies

    Conclusion

    The evolution from reactive Vulnerability Management to proactive Exposure Management is the defining shift in cybersecurity for 2026.

    The Top 10 Best Exposure Management Tools in 2026 reflect this trend, with leading vendors moving toward unified platforms that integrate discovery, threat intelligence, business context, and attack validation to deliver a prioritized, actionable view of risk.

    When selecting a tool, organizations must align their choice with their primary risk domain whether it’s cloud-native risk (Wiz), the need for real-world threat intelligence (Mandiant), or the necessity of proving control effectiveness (Cymulate).

    All platforms excel in risk prioritization, but the method (threat intelligence vs. attack path analysis vs. security ratings) is what sets them apart.

    To begin building a comprehensive EM program, security teams should focus on the initial step of Continuous Threat Exposure Management (CTEM) by establishing a complete inventory of all internet-facing assets.

    The post Top 10 Best Exposure Management Tools In 2026 appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A new wave of ClickFix attacks is abusing highly realistic fake Windows Update screens and PNG image steganography to secretly deploy infostealing malware such as LummaC2 and Rhadamanthys on victim systems.

    The campaigns rely on tricking users into manually running a pre-staged command, turning simple social engineering into a multi-stage, file-light infection chain that is hard for traditional defenses to spot.​

    ClickFix is a social engineering technique in which a web page convinces users to press Win+R, then paste and run a command that has been silently copied to the clipboard.

    Earlier lures posed as “Human Verification” or robot-check pages, but newer activity observed by Huntress swaps this for a full-screen, blue Windows Update-style splash screen with convincing progress messages.

    Fake Windows Update

    Once the fake update “completes,” the page instructs users to follow the familiar pattern and execute the malicious Run-box command.​

    That command typically launches mshta.exe with a URL whose second IP octet is hex-encoded, kicking off a staged chain that downloads obfuscated PowerShell and reflective .NET loaders. This approach leans heavily on trusted “living off the land” binaries, making the activity blend in with legitimate Windows behavior.​

    Malware hidden in PNG pixels

    The most distinctive feature of this campaign is its use of a .NET steganographic loader that hides shellcode inside the pixel data of a PNG image.

    Instead of appending data, the loader AES-decrypts an embedded PNG resource, reads the raw bitmap bytes, and reconstructs shellcode from a specific color channel, using a custom XOR-based routine to recover the payload in memory.​

    The recovered shellcode is Donut-packed and then injected into a target process such as explorer.exe via dynamically compiled C# code that calls standard Windows APIs like VirtualAllocEx, WriteProcessMemory, and CreateRemoteThread.

    In analyzed cases, this final stage has delivered LummaC2 and, in a separate Windows Update cluster, the Rhadamanthys information stealer.​

    Huntress has tracked ClickFix Windows Update clusters since early October, noting repeated use of the IP address 141.98.80[.]175 and rotating paths such as /tick.odd, /gpsc.dat, and /one.dat for the first mshta.exe stage.

    Subsequent PowerShell stages have been hosted on domains like securitysettings[.]live and xoiiasdpsdoasdpojas[.]com, pointing back to the same backend infrastructure.​

    These campaigns continued to appear around the time of Operation Endgame 3.0, which targeted Rhadamanthys’ infrastructure in mid-November, disrupting servers and seizing domains linked to the stealer.

    Even after the takedown announcement, researchers observed multiple active domains still serving the Windows Update ClickFix lure, though the Rhadamanthys payload itself appeared to be unavailable.​

    Because the attack hinges on user interaction with the Run dialog, one strong control is to disable the Windows Run box via Group Policy or registry settings (for example, configuring the NoRun policy under the Explorer key).

    Security teams should also use EDR telemetry to watch for explorer.exe spawning mshta.exe, powershell.exe, or other scripting binaries with suspicious command lines.​

    User awareness remains critical: employees should be trained that neither CAPTCHA checks nor Windows Update processes will ever require pasting commands into the Run prompt from a web page.

    During investigations, analysts can further validate potential ClickFix abuse by reviewing the RunMRU registry key, which records recent commands executed via the Run dialog.​

    Follow us on Google News, LinkedIn, and X for daily cybersecurity updates. Contact us to feature your stories.

    The post ClickFix Attack Uses Steganography to Hide Malicious Code in Fake Windows Security Update Screen appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • TRUPPENÜBUNGSPLATZ PUTLOS TRAINING GROUND, Germany—In a grassy field near the Baltic Sea, U.S. soldiers used net-shooting hunter drones, specially outfitted 557 rifles, and .50-caliber machine guns to drop dozens of drones, large and small, into the cold mud.

    For the U.S. Army, the daylong event marked the beginning of the end of firing $4-million missiles at $20,000 drones; for its European counterparts, it showed off options to counter Russia’s accelerating threat.

    The event was part of Project Flytrap, a U.S. Army effort to advance the state of counter-drone art. More than 200 vendors applied to participate in the November iteration; 20 were chosen by the Global Tactical Edge Acquisition Directorate, a new procurement office the service set up to get such gear to the field quickly.

    On Nov. 21, media and foreign militaries watched a series of demonstrations that showed off not just individual products, but how they could be made to work together in just days.

    Brig. Gen. Curtis King of the 10th Army Air and Missile Defense Command told Defense One that Ukrainian descriptions of battlefield conditions have helped the U.S. Army develop new tactics, gear, and weapons.

    Because supply lines are vulnerable, it’s useful to be able to make drones at, or near, the front lines. In a tent on the field, a soldier with the 10th AAMDC showed off the results of some experimentation: a 3D printer that can print a drone frame in a few hours. With pre-ordered electronic components, it could serve as an interceptor or as part of a sensor mesh to locate enemy drones and their launching points.

    More sensing is key to effective, affordable counter-drone efforts. King said one of the most important aspects of the event was integrating data from active radar systems with that of passive radar, a novel form that deduces a drone’s location from perturbations in FM radio signals. And he said the event showed off a real breakthrough: integrating all that sensor data so it could be used at all levels, from anti-drone snipers to the operators of first-person-view drones to unit commanders.

    “We were able to send that to the units that were working on classified systems, and we were able to send that information to units who were working on sensitive but unclassified information. We've been demonstrating that for a while, but what was so significant this time is the number of sensors that we did and we did that with no latency, meaning we got real-time data,” he said.

    Soldier feedback led to a top prize for Armaments Research Company, whose portable drone-tracing gear could turn “every soldier into a sensor,” said CEO Mike Canty, an Iraq War veteran.

    An “aim assistant” from Zeromark helps soldiers shoot down drones with bullets—rather than with lasers that are still under development or jammers that don’t work against autonomous drones.

    Then there’s Fortem's net-shooting drone, useful in cities or around civilian populations.

    Besides helping the U.S. Army, the show aimed to help European officials learn to defend themselves against Russian drones, even if the U.S. backs out of its security guarantees. 

    “What you saw today … are effectors that cost much less, sometimes a tenth of the cost of that drone. So not only are we still achieving the lethality we need, but we're doing it on the right side of the cost curve,” King told reporters. 

    Journalists from Europe wanted to know: will the tech on display really stop Russian drone incursions? 

    King and other Army officials didn’t have a simple answer. They noted that the United States remains part of NATO, that the event aimed to inform European decision-making, and that future FlyTrap events will incorporate ground robotics and air-launched effects.

    Col. Chris Hill, project manager for integrated fires mission command, noted, “The real goal is to have soldiers from other countries that are part of the assessment, because you want skin in the game early. You want your soldiers to take a look at their own commands, to say, ‘Yes, this capability works.’ You see a lot of non-U.S. flags out there because if you look at the eastern flank, those are NATO countries. So every country along that plane who's in closest proximity to the threat from Russia needs to know that the kit actually works.”

    ]]>

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • NVIDIA has disclosed two critical code injection vulnerabilities affecting its Isaac-GR00T robotics platform.

    The vulnerabilities, tracked as CVE-2025-33183 and CVE-2025-33184, exist within Python components and could allow authenticated attackers to execute arbitrary code, escalate privileges, and alter system data.

    The flaws pose a significant threat to organizations deploying NVIDIA’s robotics solutions across industrial automation, research facilities, and autonomous systems.

    Both vulnerabilities carry a high CVSS score of 7.8, indicating serious security risks that require immediate remediation.

    Vulnerability Details

    The code injection issues affect all versions of NVIDIA Isaac-GR00T N1.5 across all platforms.

    An attacker with local access and low-level privileges could exploit these vulnerabilities without user interaction, potentially gaining complete system control.

    CVE IDDescriptionCVSS ScoreCWEAttack Vector
    CVE-2025-33183Code injection in Python component allowing arbitrary code execution7.8CWE-94Local/Low Privilege
    CVE-2025-33184Code injection in Python component allowing arbitrary code execution7.8CWE-94Local/Low Privilege

    Successful exploitation could result in unauthorized code execution, privilege escalation, information disclosure, and data modification, compromising the integrity of critical robotic operations.

    Both vulnerabilities stem from improper handling of user-supplied input in Python components, classified under CWE-94 (Improper Control of Generation of Code).

    This weakness has been historically exploited in numerous attacks targeting interpreted code environments.

    NVIDIA has released a software update addressing both vulnerabilities. The patch is available through GitHub commit 7f53666 of the Isaac-GR00T repository.

    Organizations running Isaac-GR00T should immediately update to any code branch incorporating this specific commit to eliminate the attack surface.

    System administrators should prioritize deploying the security update across all Isaac-GR00T deployments.

    Given the high severity rating and the potential for critical system compromise, NVIDIA recommends treating this as an urgent priority.

    Organizations unable to patch immediately should restrict local access to affected systems and monitor for suspicious activity.

    NVIDIA’s Product Security Incident Response Team (PSIRT) continues monitoring for exploitation attempts.

    The vulnerabilities were responsibly disclosed by Peter Girnus of Trend Micro Zero Day Initiative, highlighting the importance of coordinated vulnerability research.

    For comprehensive information, visit NVIDIA’s Product Security page to access complete Security alerts and subscribe to future vulnerability notifications.

    Follow us on Google News, LinkedIn, and X for daily cybersecurity updates. Contact us to feature your stories.

    The post NVIDIA’s Isaac-GROOT Robotics Platform Vulnerability Let Attackers Inject Malicious Codes appeared first on Cyber Security News.
    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The Department of Government Efficiency, a cornerstone of the second Trump administration's efforts to remake the federal government, no longer exists as a "centralized entity," according to the head of the government’s personnel agency. 

    But the longstanding White House technology team that President Donald Trump used to house DOGE continues to work on technology modernization projects throughout federal agencies.

    The administration’s head of the Office of Personnel Management, Scott Kupor, told Reuters that DOGE “doesn’t exist” anymore, and posted on X that DOGE doesn’t have “centralized leadership” within the U.S. DOGE Service, though he did clarify that its principles “remain alive and well.” Fox News also reported that the centralized office for DOGE is closed.

    Trump used an existing, Obama-era technology unit in the White House to establish the controversial cost-cutting unit on day one of his administration in January, installing DOGE within what was then the U.S. Digital Service and renaming it the U.S. DOGE Service. 

    The Trump executive order establishing DOGE also set up a "temporary organization” within USDS with a pre-set dissolution date on July 4, 2026. 

    DOGE made headlines throughout the spring for shutting down entire agencies, culling government contracts, getting rid of federal employees and accessing sensitive government systems. 

    But as Nextgov/FCW has reported before, the temporary organization and the USDS team that predated DOGE haven’t necessarily been working together, with the former taking on the controversial efficiency work and the other focusing on low-profile government modernization projects.

    Even so, dozens of USDS employees from the team predating DOGE have been dismissed since Trump took office. Others have resigned.

    USDS still has about 50 employees, according to a source familiar with its operations who was not authorized to speak on the record. In July, the service was looking for new hires. 

    A shutdown plan for the White House, updated in October, also referenced 45 DOGE employees, which likely also refers to those working at USDS. The temporary DOGE organization had only one or two people left as of recent months, according to the source familiar.

    The team that predated DOGE continues to work on user experience and modernization projects at agencies like the departments of Veterans Affairs and State, the General Services Administration and the Centers for Medicare and Medicaid Services. These efforts are in line with the work of the U.S. Digital Service pre-DOGE, said the source familiar. 

    The USDS accounts also posted that “the executive order establishing U.S. DOGE Service (USDS) is still in effect,” calling the Reuters story “misinformation” on X and LinkedIn Monday.

    “USDS is still partnering with agencies to modernize federal technology and software to maximize governmental efficiency and productivity,” the post continued, the words written out over a photo of the popular internet doge meme associated with Dogecoin cryptocurrency and the administration’s efficiency team. The White House also told Nextgov/FCW that DOGE continues to be integrated into agencies.

    “President Trump was given a clear mandate to reduce waste, fraud, and abuse across the federal government, and he continues to actively deliver on that commitment,” White House Assistant Press Secretary Liz Huston said in a statement.

    Despite Kupor’s comments about a lack of centralized leadership for DOGE, the team’s acting administrator, Amy Gleason, does appear to still be at USDS.

    It is true that much has changed about DOGE since the spring. 

    Billionaire Elon Musk initially led DOGE, but he stepped away from the effort in May only to have a public feud with Trump. Many DOGE staffers followed the Tesla CEO out the door, while others have taken on appointments and leadership roles in agencies. 

    One DOGE associate, Joe Gebbia, is now heading an entirely new White House “America by Design” initiative.

    The news about DOGE becoming more dispersed isn’t necessarily a surprise. 

    In early June, the director of the Office of Management and Budget, Russell Vought, told lawmakers that the vision for DOGE was for it to become more "institutionalized" within agencies as “in-house consultants,” and that the leadership of DOGE was “decentralized” and with agency heads.

    Either way, the DOGE ethos appears to still be a priority for the administration, which began layoff proceedings for 4,000 federal employees during the recent shutdown, a move a court eventually paused and Congress later reversed as part of the funding provision to reopen the government.

    OPM and the Office of Management and Budget are institutionalizing the cost-cutting unit’s “principles,” the head of OPM wrote on X, linking to a blog about a recent executive order that set out new requirements for agencies on headcount and hiring.

    OPM has “not taken on new responsibilities,” an OPM spokesperson told Nextgov/FCW, but continues “to prioritize efficiency in the federal workforce in line with the president’s priorities.”

    ]]>

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A mask of darkness had fallen over the Gobi Desert training grounds at Zhurihe when the Blue Force unleashed a withering strike intended to wipe Red Force artillery off the map. Plumes rose from “destroyed” batteries as the seemingly successful fire plan took out its targets in waves. But it had all been a trap. 

    When Blue began to shift positions to avoid counter-battery fire, exercise control called a halt—and revealed that, far from defeating the enemy, more than half of Blue’s fire units had already been destroyed. After the exercise, the Red commander explained the ruse: he had salted the range with decoy guns and what he called “professional stand-ins,” the signatures of units and troops, which not only tricked Blue’s sensors and AI-assisted targeting into shooting at phantoms, but also revealed their own firing points.

    It was just one example of how China’s military is building for a battlefield where humans and AI seek not just to fight, but fool each other. 

    Under the banner of “counter-AI warfare”, the People’s Liberation Army is teaching troops to fight the model as much as the soldier. Forces are learning to alter how vehicles appear to cameras, radar, and heat sensors so the AI misidentifies them, to feed junk or poisoned data into an opponent’s pipeline, and to swamp battlefield computers with noise. Leaders are drilling their own teams to spot when their own machines are wrong. The goal is simple: make an enemy’s military AI chase phantoms and miss the real threat. 

    The PLA conceives its counter-AI playbook as a triad that targets data, algorithms, and computing power. In May, PLA Daily described the concept in its Intelligentized Warfare Panorama series. It argued that the most reliable way to “break intelligence” is to hit all three at once. 

    First, counter-data operations inject junk data, skew what the sensors see, slip in corrupted examples, and reshape a vehicle’s radar, heat, and visual signals with coatings and emitters that mimic another platform’s profile and even engine vibration to mislead AI-assisted ISR. Second, counter-algorithm operations take advantage of model weak spots with logic tricks and crafted inputs, confusing AIs by breaking their “reward” signals and leading them to waste time in fruitless searches. Finally, attacks on computing power include “hard-kill” kinetic and cyber strikes on data centers and links, and “soft-kill” saturation attacks that flood the battlespace with electromagnetic noise, tying down scarce computing resources and clogging decision loops. A 2024 study by PLA researchers lists soft-kill techniques such as data pollution, reversal, backdoor insertion, and adversarial attacks that manipulate machine learning models.

    Commentary from PLA analysts casts the contest as algorithm-versus-algorithm in joint operations. It urges planners to defeat enemy algorithms by testing how the algorithms make decisions, scrambling the signals that guide drone swarms, and maneuvering in unexpected ways to throw off the patterns those systems are trained to favor, with the aim of tricking enemy sensors and models into misidentifying targets. 

    In sum, instead of fearing an enemy’s use of AI, the PLA defines the adversary’s AI as a target set, and assigns work to hit each part.

    The PLA is already putting these ideas into action. In August 2023, an Air Force UAV regiment added “real and fake targets” to target-unmasking drills, forcing pilots to sort decoys from real targets. Similarly, PLA air-defense training now treats ultra-low-altitude penetration as a priority, with studies framing the fight as the meeting point of decoys, deceptive signatures, and AI-aided or intelligent recognition. In the maritime arena, a 2024 study builds a framework for unmanned underwater vehicles to detect and ignore acoustic decoys when attacking a surface vessel.

    PLA writers also give sustained attention to the human half of the team. In April, PLA Daily warned that commanders can slide into technology dependency and amplify bias baked into training data. The remedy is training commanders to judge when to trust the AI and when to overrule it by adding deception scenarios to simulations and running human and machine war games so operators practice spotting bad advice and overriding it. Follow-on commentary argued for “cognitive consistency” between operator and tool. In this model, wargames embed adversary behavior and develop rapid courses of action so instructors can see when officers override a wrong algorithm and explain why.

    Human-in-the-loop command remains the baseline, with humans continuing to play the role of operator, fail-safe, and moral arbiter. Lt. Gen. He Lei echoed this view in 2024, urging tight limits on wartime AI and insisting that life-and-death authority stay with humans. Recent guidance adds rules for how units collect, label, and track data from start to finish, and those rules feed training scenarios, post-exercise reviews, and performance scores.

    Industry’s role

    Reflecting this growth in PLA thinking, Chinese companies have also begun to market counter-AI products in the categories of physical deception, electronic warfare, and software. Huaqin Technology markets multispectral camouflage that hides radar, infrared, and visual signatures. Yangzhou Spark offers camouflage nets and suits, stealth coatings, radar-absorbing materials, smoke generators, signature simulators, and radar reflectors. JX Gauss advertises inflatable, full-scale radar-vehicle decoys with remote-controlled moving parts. Together, these products support the counter-data playbook by changing how vehicles appear to radar, infrared, and visual sensors, planting convincing decoys, and tricking AI-enabled surveillance into locking onto the wrong signals.

    Electronic-warfare vendors jam communications links and network connections, following the PLA’s soft-kill computing resources concept. Saturating the spectrum with clutter and false signals forces the enemy’s AI and limited computing power to waste time and resources, while friendly forces maintain a clear picture. Chengdu M&S Electronics lists gear that generates false target signals, fields radar decoy rounds, and provides simulators that play back hostile radar and communications signals to confuse receivers. Balu Electronics sells communications-jamming simulators that build complex electromagnetic environments and drive multi-target interference. 

    Meanwhile, Chinese tech firms are developing counter-AI software. Tencent Cloud runs a large-model red-team program and offers tools that monitor and lock down model inputs and outputs to block prompt injection, tainted data, and leaks. Qi’anxin’s model protection fence and GPT-Guard add tools that simulate attacks and watch inputs and outputs for tampering, and RealAI’s RealSafe automatically builds test cases that try to fool models and checks how well they hold up. Marketed as defense, these tools also sharpen tradecraft for pressuring an opponent’s algorithms.

    U.S. response

    U.S. planners need not look to China to understand that they must assume their AI will be contested in future battles. The PLA’s work in this space reflects the lessons from Ukraine, where deception operations have taken on a new level of importance in a battlefield saturated with sensors. It also heightens the concern of a growing “deception gap,” where if the U.S. military and its partners cannot master today’s emerging tools, they may fall behind in a critical field.

    Answering that playbook begins with structured red-teaming and rigorous test and evaluation, not just one-off demos. The U.S. already has building blocks, including DARPA’s GARD on adversarial robustness, IARPA’s TrojAI on backdoor detection, NIST’s AI Risk Management Framework for evaluation and risk controls, and DOT&E guidance for continuous test and evaluation across the enterprise. Planners must harden pipelines and models by protecting data provenance, detecting anomalies, preserving safe fallbacks, and monitoring model health in the field.

    Keeping humans decisively on top of the loop remains essential and is codified in DoD Directive 3000.09 on autonomy in weapons. Units should also upgrade the opposing forces they train against, giving them AI-enabled reconnaissance and deception kits and ensuring that “real and fake” targets are part of every major exercise.

    Failure to do so will mean that the American military’s enthusiastic embrace of AI leads not to new advantages, but new vulnerabilities and even loss in this crucial new aspect of warfare.

    ]]>

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Foreign spies are posing as consulting firms, think tanks, corporate recruiters, and more to exploit U.S. soldiers, Army civilians, and family members, the Army deputy chief of staff for intelligence said in a recent memo.

    “Especially in the context of the recent lapse in appropriations and government shutdown, our adversaries are looking online to identify individuals seeking new employment opportunities, expressing dissatisfaction or describing financial insecurity,” Lt. Gen. Anthony R. Hale wrote in a Nov. 13 message sent to more than a million soldiers and Army-related civilians.

    Current and former federal workers, especially those with security clearances, should be aware of these attempts, the message said. “If the offer seems flattering, urgent, exclusive or too good to be true, it probably is.”

    The Army publicized Hale's message in a Monday statement.

    His warning was issued after months of Defense Department changes that fired some civilian employees, induced thousands more to leave, and left many others shaken. The message went out just after the government reopened from a record-long shutdown on Nov. 12.

    In June 2024, a transmission provided by the Army indicated that it had observed such foreign intelligence activity for some time. It said adversaries use less-traditional social-messaging platforms like Reddit and Discord to pose seemingly innocuous questions to servicemembers that increase in sensitivity over time. 

    Requesters “may rely on opinion-based questions such as asking [Department of the Army] personnel for their opinion on topics such as Taiwan, Ukraine or Israel to gather information,” it said. The espionage efforts do not target only classified information and aim to access various forms of sensitive data like battle plans, contracts and research.

    Army members and their families may also be extended “disproportionate payment” offers, such as $1,000 for a two-page whitepaper or an all-expense paid trip to destinations like China, Hong Kong or Macao, the 2024 message said.

    A suspected Chinese intelligence operation has tried to recruit former U.S. federal employees and public policy experts through fake websites and job postings, Nextgov/FCW first reported in September. 

    Those recruitment efforts — which involved low-quality websites representing non-existent companies — appear to have picked up steam amid Department of Government Efficiency-fueled employee departures and terminations over the last several months.

    The FBI previously told Nextgov/FCW that it’s aware of foreign adversaries using employment sites and social media platforms to identify knowledgeable individuals to target for recruitment.

    “Often those targeted have security clearances and access to classified information. But our adversaries also are looking for experts in business and academia with technical expertise,” the bureau said.

    Chinese intelligence entities have deployed online efforts to recruit unwitting current and former federal employees, the National Counterintelligence and Security Center said in April. In March, CNN reported that foreign adversaries, including China and Russia, accelerated efforts to recruit disgruntled federal workers in national security roles.

    ]]>

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

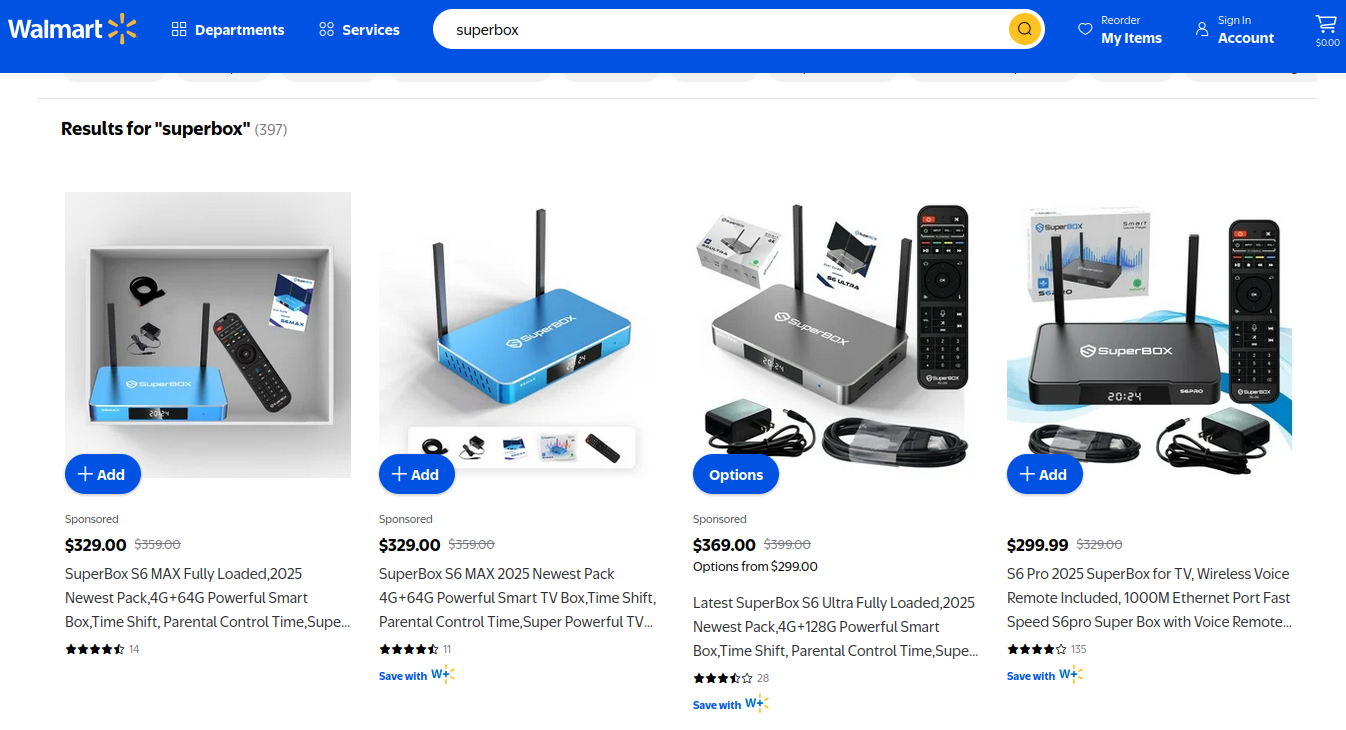
  • On the surface, the Superbox media streaming devices for sale at retailers like BestBuy and Walmart may seem like a steal: They offer unlimited access to more than 2,200 pay-per-view and streaming services like Netflix, ESPN and Hulu, all for a one-time fee of around $400. But security experts warn these TV boxes require intrusive software that forces the user’s network to relay Internet traffic for others, traffic that is often tied to cybercrime activity such as advertising fraud and account takeovers.

    Superbox media streaming boxes for sale on Walmart.com.

    Superbox bills itself as an affordable way for households to stream all of the television and movie content they could possibly want, without the hassle of monthly subscription fees — for a one-time payment of nearly $400.

    “Tired of confusing cable bills and hidden fees?,” Superbox’s website asks in a recent blog post titled, “Cheap Cable TV for Low Income: Watch TV, No Monthly Bills.”

    “Real cheap cable TV for low income solutions does exist,” the blog continues. “This guide breaks down the best alternatives to stop overpaying, from free over-the-air options to one-time purchase devices that eliminate monthly bills.”

    Superbox claims that watching a stream of movies, TV shows, and sporting events won’t violate U.S. copyright law.

    “SuperBox is just like any other Android TV box on the market, we can not control what software customers will use,” the company’s website maintains. “And you won’t encounter a law issue unless uploading, downloading, or broadcasting content to a large group.”

    A blog post from the Superbox website.

    There is nothing illegal about the sale or use of the Superbox itself, which can be used strictly as a way to stream content at providers where users already have a paid subscription. But that is not why people are shelling out $400 for these machines. The only way to watch those 2,200+ channels for free with a Superbox is to install several apps made for the device that enable them to stream this content.

    Superbox’s homepage includes a prominent message stating the company does “not sell access to or preinstall any apps that bypass paywalls or provide access to unauthorized content.” The company explains that they merely provide the hardware, while customers choose which apps to install.

    “We only sell the hardware device,” the notice states. “Customers must use official apps and licensed services; unauthorized use may violate copyright law.”

    Superbox is technically correct here, except for maybe the part about how customers must use official apps and licensed services: Before the Superbox can stream those thousands of channels, users must configure the device to update itself, and the first step involves ripping out Google’s official Play store and replacing it with something called the “App Store” or “Blue TV Store.”

    Superbox does this because the device does not use the official Google-certified Android TV system, and its apps will not load otherwise. Only after the Google Play store has been supplanted by this unofficial App Store do the various movie and video streaming apps that are built specifically for the Superbox appear available for download (again, outside of Google’s app ecosystem).

    Experts say while these Android streaming boxes generally do what they advertise — enabling buyers to stream video content that would normally require a paid subscription — the apps that enable the streaming also ensnare the user’s Internet connection in a distributed residential proxy network that uses the devices to relay traffic from others.

    Ashley is a senior solutions engineer at Censys, a cyber intelligence company that indexes Internet-connected devices, services and hosts. Ashley requested that only her first name be used in this story.

    In a recent video interview, Ashley showed off several Superbox models that Censys was studying in the malware lab — including one purchased off the shelf at BestBuy.

    “I’m sure a lot of people are thinking, ‘Hey, how bad could it be if it’s for sale at the big box stores?’” she said. “But the more I looked, things got weirder and weirder.”

    Ashley said she found the Superbox devices immediately contacted a server at the Chinese instant messaging service Tencent QQ, as well as a residential proxy service called Grass IO.

    GET GRASSED

    Also known as getgrass[.]io, Grass says it is “a decentralized network that allows users to earn rewards by sharing their unused Internet bandwidth with AI labs and other companies.”

    “Buyers seek unused internet bandwidth to access a more diverse range of IP addresses, which enables them to see certain websites from a retail perspective,” the Grass website explains. “By utilizing your unused internet bandwidth, they can conduct market research, or perform tasks like web scraping to train AI.” 

    Reached via Twitter/X, Grass founder Andrej Radonjic told KrebsOnSecurity he’d never heard of a Superbox, and that Grass has no affiliation with the device maker.

    “It looks like these boxes are distributing an unethical proxy network which people are using to try to take advantage of Grass,” Radonjic said. “The point of grass is to be an opt-in network. You download the grass app to monetize your unused bandwidth. There are tons of sketchy SDKs out there that hijack people’s bandwidth to help webscraping companies.”

    Radonjic said Grass has implemented “a robust system to identify network abusers,” and that if it discovers anyone trying to misuse or circumvent its terms of service, the company takes steps to stop it and prevent those users from earning points or rewards.

    Superbox’s parent company, Super Media Technology Company Ltd., lists its street address as a UPS store in Fountain Valley, Calif. The company did not respond to multiple inquiries.

    According to this teardown by behindmlm.com, a blog that covers multi-level marketing (MLM) schemes, Grass’s compensation plan is built around “grass points,” which are earned through the use of the Grass app and through app usage by recruited affiliates. Affiliates can earn 5,000 grass points for clocking 100 hours usage of Grass’s app, but they must progress through ten affiliate tiers or ranks before they can redeem their grass points (presumably for some type of cryptocurrency). The 10th or “Titan” tier requires affiliates to accumulate a whopping 50 million grass points, or recruit at least 221 more affiliates.

    Radonjic said Grass’s system has changed in recent months, and confirmed the company has a referral program where users can earn Grass Uptime Points by contributing their own bandwidth and/or by inviting other users to participate.

    “Users are not required to participate in the referral program to earn Grass Uptime Points or to receive Grass Tokens,” Radonjic said. “Grass is in the process of phasing out the referral program and has introduced an updated Grass Points model.”

    A review of the Terms and Conditions page for getgrass[.]io at the Wayback Machine shows Grass’s parent company has changed names at least five times in the course of its two-year existence. Searching the Wayback Machine on getgrass[.]io shows that in June 2023 Grass was owned by a company called Wynd Network. By March 2024, the owner was listed as Lower Tribeca Corp. in the Bahamas. By August 2024, Grass was controlled by a Half Space Labs Limited, and in November 2024 the company was owned by Grass OpCo (BVI) Ltd. Currently, the Grass website says its parent is just Grass OpCo Ltd (no BVI in the name).

    Radonjic acknowledged that Grass has undergone “a handful of corporate clean-ups over the last couple of years,” but described them as administrative changes that had no operational impact. “These reflect normal early-stage restructuring as the project moved from initial development…into the current structure under the Grass Foundation,” he said.

    UNBOXING

    Censys’s Ashley said the phone home to China’s Tencent QQ instant messaging service was the first red flag with the Superbox devices she examined. She also discovered the streaming boxes included powerful network analysis and remote access tools, such as Tcpdump and Netcat.

    “This thing DNS hijacked my router, did ARP poisoning to the point where things fall off the network so they can assume that IP, and attempted to bypass controls,” she said. “I have root on all of them now, and they actually have a folder called ‘secondstage.’ These devices also have Netcat and Tcpdump on them, and yet they are supposed to be streaming devices.”

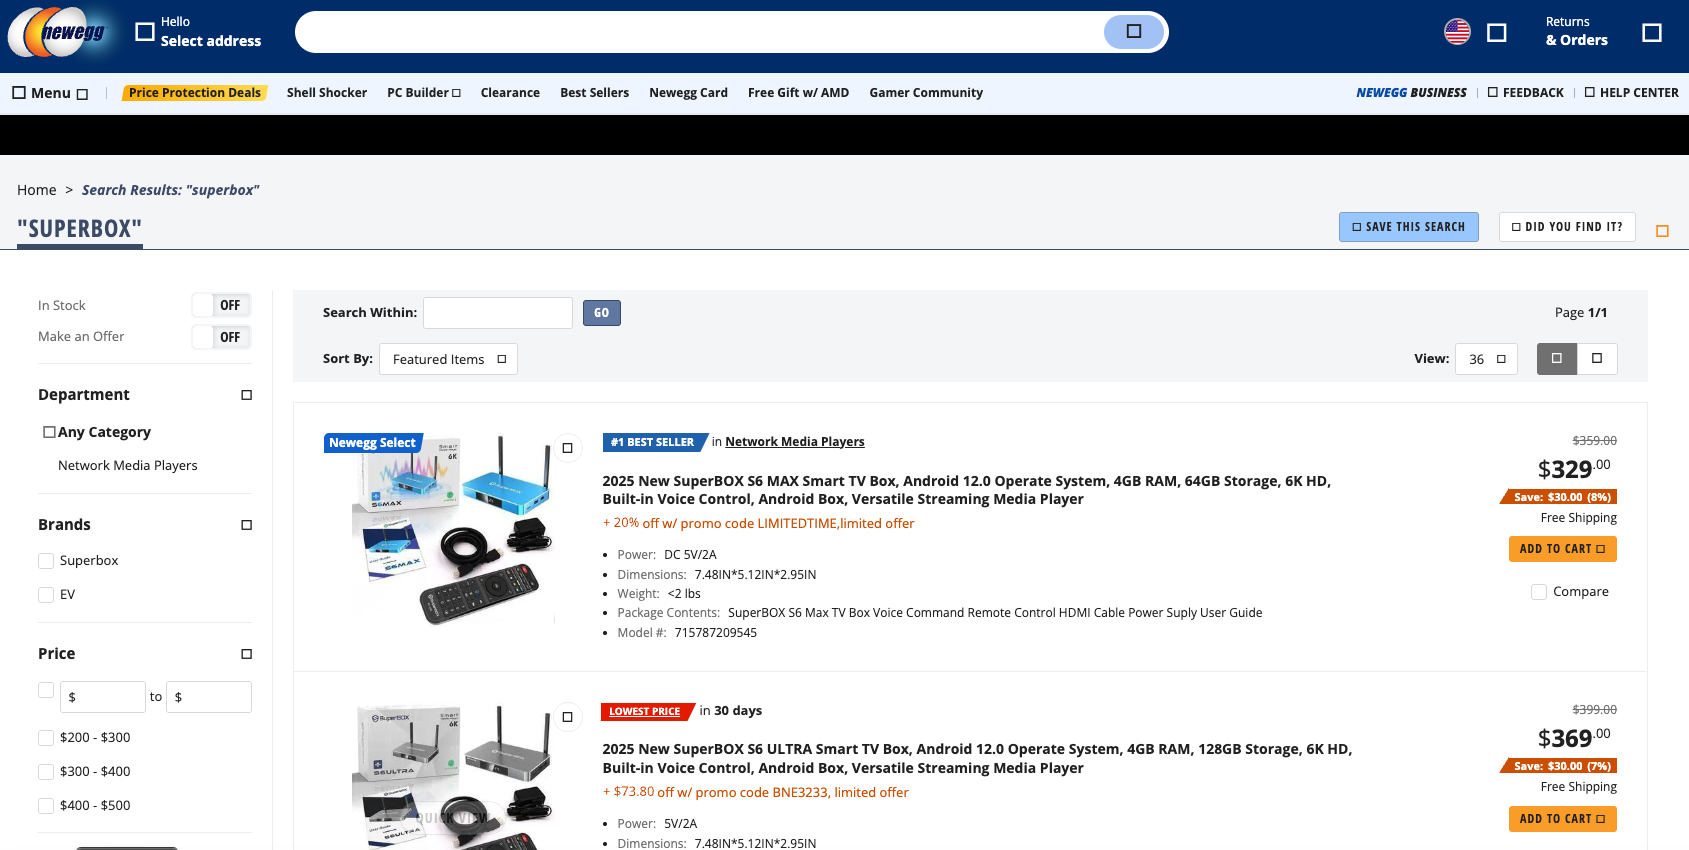
    A quick online search shows various Superbox models and many similar Android streaming devices for sale at a wide range of top retail destinations, including Amazon, BestBuy, Newegg, and Walmart. Newegg.com, for example, currently lists more than three dozen Superbox models. In all cases, the products are sold by third-party merchants on these platforms, but in many instances the fulfillment comes from the e-commerce platform itself.

    “Newegg is pretty bad now with these devices,” Ashley said. “Ebay is the funniest, because they have Superbox in Spanish — the SuperCaja — which is very popular.”

    Superbox devices for sale via Newegg.com.

    Ashley said Amazon recently cracked down on Android streaming devices branded as Superbox, but that those listings can still be found under the more generic title “modem and router combo” (which may be slightly closer to the truth about the device’s behavior).

    Superbox doesn’t advertise its products in the conventional sense. Rather, it seems to rely on lesser-known influencers on places like Youtube and TikTok to promote the devices. Meanwhile, Ashley said, Superbox pays those influencers 50 percent of the value of each device they sell.

    “It’s weird to me because influencer marketing usually caps compensation at 15 percent, and it means they don’t care about the money,” she said. “This is about building their network.”

    A TikTok influencer casually mentions and promotes Superbox while chatting with her followers over a glass of wine.

    BADBOX

    As plentiful as the Superbox is on e-commerce sites, it is just one brand in an ocean of no-name Android-based TV boxes available to consumers. While these devices generally do provide buyers with “free” streaming content, they also tend to include factory-installed malware or require the installation of third-party apps that engage the user’s Internet address in advertising fraud.

    In July 2025, Google filed a “John Doe” lawsuit (PDF) against 25 unidentified defendants dubbed the “BadBox 2.0 Enterprise,” which Google described as a botnet of over ten million Android streaming devices that engaged in advertising fraud. Google said the BADBOX 2.0 botnet, in addition to compromising multiple types of devices prior to purchase, can also infect devices by requiring the download of malicious apps from unofficial marketplaces.

    Some of the unofficial Android devices flagged by Google as part of the Badbox 2.0 botnet are still widely for sale at major e-commerce vendors. Image: Google.

    Several of the Android streaming devices flagged in Google’s lawsuit are still for sale on top U.S. retail sites. For example, searching for the “X88Pro 10” and the “T95” Android streaming boxes finds both continue to be peddled by Amazon sellers.

    Google’s lawsuit came on the heels of a June 2025 advisory from the Federal Bureau of Investigation (FBI), which warned that cyber criminals were gaining unauthorized access to home networks by either configuring the products with malicious software prior to the user’s purchase, or infecting the device as it downloads required applications that contain backdoors, usually during the set-up process.

    “Once these compromised IoT devices are connected to home networks, the infected devices are susceptible to becoming part of the BADBOX 2.0 botnet and residential proxy services known to be used for malicious activity,” the FBI said.

    The FBI said BADBOX 2.0 was discovered after the original BADBOX campaign was disrupted in 2024. The original BADBOX was identified in 2023, and primarily consisted of Android operating system devices that were compromised with backdoor malware prior to purchase.

    Riley Kilmer is founder of Spur, a company that tracks residential proxy networks. Kilmer said Badbox 2.0 was used as a distribution platform for IPidea, a China-based entity that is now the world’s largest residential proxy network.

    Kilmer and others say IPidea is merely a rebrand of 911S5 Proxy, a China-based proxy provider sanctioned last year by the U.S. Department of the Treasury for operating a botnet that helped criminals steal billions of dollars from financial institutions, credit card issuers, and federal lending programs (the U.S. Department of Justice also arrested the alleged owner of 911S5).

    How are most IPidea customers using the proxy service? According to the proxy detection service Synthient, six of the top ten destinations for IPidea proxies involved traffic that has been linked to either ad fraud or credential stuffing (account takeover attempts).

    Kilmer said companies like Grass are probably being truthful when they say that some of their customers are companies performing web scraping to train artificial intelligence efforts, because a great deal of content scraping which ultimately benefits AI companies is now leveraging these proxy networks to further obfuscate their aggressive data-slurping activity. By routing this unwelcome traffic through residential IP addresses, Kilmer said, content scraping firms can make it far trickier to filter out.

    “Web crawling and scraping has always been a thing, but AI made it like a commodity, data that had to be collected,” Kilmer told KrebsOnSecurity. “Everybody wanted to monetize their own data pots, and how they monetize that is different across the board.”

    SOME FRIENDLY ADVICE

    Products like Superbox are drawing increased interest from consumers as more popular network television shows and sportscasts migrate to subscription streaming services, and as people begin to realize they’re spending as much or more on streaming services than they previously paid for cable or satellite TV.

    These streaming devices from no-name technology vendors are another example of the maxim, “If something is free, you are the product,” meaning the company is making money by selling access to and/or information about its users and their data.

    Superbox owners might counter, “Free? I paid $400 for that device!” But remember: Just because you paid a lot for something doesn’t mean you are done paying for it, or that somehow you are the only one who might be worse off from the transaction.

    It may be that many Superbox customers don’t care if someone uses their Internet connection to tunnel traffic for ad fraud and account takeovers; for them, it beats paying for multiple streaming services each month. My guess, however, is that quite a few people who buy (or are gifted) these products have little understanding of the bargain they’re making when they plug them into an Internet router.

    Superbox performs some serious linguistic gymnastics to claim its products don’t violate copyright laws, and that its customers alone are responsible for understanding and observing any local laws on the matter. However, buyer beware: If you’re a resident of the United States, you should know that using these devices for unauthorized streaming violates the Digital Millennium Copyright Act (DMCA), and can incur legal action, fines, and potential warnings and/or suspension of service by your Internet service provider.

    According to the FBI, there are several signs to look for that may indicate a streaming device you own is malicious, including:

    -The presence of suspicious marketplaces where apps are downloaded.
    -Requiring Google Play Protect settings to be disabled.
    -Generic TV streaming devices advertised as unlocked or capable of accessing free content.
    -IoT devices advertised from unrecognizable brands.
    -Android devices that are not Play Protect certified.
    -Unexplained or suspicious Internet traffic.

    This explainer from the Electronic Frontier Foundation delves a bit deeper into each of the potential symptoms listed above.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A new malware campaign targeting Brazilian users has emerged, using WhatsApp as its primary distribution channel to spread banking trojans and harvest sensitive information.

    This sophisticated attack leverages social engineering by exploiting the trust victims place in their existing contacts, making the malicious files appear legitimate.

    The campaign begins with phishing emails containing archived VBS scripts that employ advanced obfuscation techniques to evade detection by security software.

    Once the initial payload runs, it downloads and installs Python and the Selenium WebDriver components, enabling automated interaction with WhatsApp Web.

    The malware then injects malicious JavaScript code into the victim’s browser session, accessing WhatsApp’s internal APIs to enumerate contacts and distribute payloads.

    This approach allows attackers to spread the infection without requiring QR code authentication by hijacking existing logged-in sessions by copying browser cookies and local storage data.

    K7 Security Labs researchers identified this variant as part of the broader Water-Saci campaign, which has been actively targeting financial institutions across Brazil.

    The attack chain deploys both a Python-based distribution script and a banking trojan that monitors for active Windows related to Brazilian banks and cryptocurrency wallets.

    By combining automated messaging with memory-only payload execution, the malware remains undetected, mainly while compromising victim machines and their entire contact networks.

    The campaign also delivers an MSI installer that drops an AutoIt script alongside encrypted payload files. This secondary component establishes persistence through registry modifications and continuously monitors the victim’s active windows for banking-related keywords.

    Kill chain (Source - K7 Security Labs)
    Kill chain (Source – K7 Security Labs)

    When specific financial institutions or crypto wallet applications are detected, the malware decrypts and loads its banking trojan directly into memory, bypassing disk writes and making traditional file-based detection methods ineffective.

    Technical Breakdown of the Infection Mechanism

    The infection begins when victims receive phishing emails containing ZIP-archived VBS script files that use character encoding and XOR encryption to evade signature-based detection.

    The script employs a multi-layered obfuscation strategy, building strings character by character using Chr() functions and then applying XOR operations with specific values to decode the actual malicious commands.

    objyAQeaOCCI = objyAQeaOCCI & Chr(49)
    objyAQea0cCI = objyAQeaOCCI & Chr(55)
    objyAQea0cCI = objyAQeaOCCI & Chr(57)
    For Each varcBAIRFO In Split(strSwQRHTeBd, aOwTbJaE)
    objhiCebPk = (objhiCebPk (26 Xor 93)) Mod 256
    objhiCebPk = (objhiCebPk (150 Xor 104)) Mod 256

    Char and Xor (Source - K7 Security Labs)
    Char and Xor (Source – K7 Security Labs)

    After deobfuscation, the script downloads two components: an MSI file and another VBS file. The downloaded VBS file contains identical obfuscation patterns and drops a batch script that installs the Python, ChromeDriver, and Selenium packages.

    This automated setup creates the infrastructure needed for WhatsApp automation without requiring manual user intervention.

    The Python script, named whats.py, takes control of the victim’s WhatsApp Web session by copying browser profile data, including cookies, local storage, and IndexedDB files, to a temporary directory.

    Using Selenium’s user-data-dir argument, the script launches Chrome with these copied credentials, effectively bypassing the QR code authentication step that would usually protect WhatsApp Web access.

    arquivos_copiar = [
    “Cookies”, “Cookies-journal”,
    “Local Storage”, “Session Storage”,
    “IndexedDB”, “Service Worker”
    ]
    options.add_argument(f”–user-data-dir={perfil_temp}”)

    Sets up the user-data-dir (Source - K7 Security Labs)
    Sets up the user-data-dir (Source – K7 Security Labs)

    Once authenticated, the malware injects helper JavaScript from GitHub into the WhatsApp Web page context, enabling access to internal API functions like WPP.contact.list, WPP.chat.sendTextMessage, and WPP.chat.sendFileMessage.

    The script then harvests the victim’s contact list, filtering out groups, business accounts, and contacts with specific number patterns configured by the attackers.

    These harvested contacts are batched and systematically sent malicious ZIP files containing the next stage of the infection, perpetuating the campaign across victim networks while sending detailed logs back to the attacker’s PHP server.

    Follow us on Google News, LinkedIn, and X to Get More Instant Updates, Set CSN as a Preferred Source in Google.

    The post Hackers Leveraging WhatsApp That Silently Harvest Logs and Contact Details appeared first on Cyber Security News.
    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Tel Aviv, Israel, November 24th, 2025, CyberNewsWire Blast is introducing a new operating model for cloud security with a first-of-its-kind Preemptive Cloud Defense Platform, replacing reactive response with continuous prevention. Blast Security, a cybersecurity startup founded by industry veterans from Solebit (acquired by Mimecast) and elite IDF units, today announced its launch from stealth and […]

    The post Elite Cyber Veterans Launch Blast Security with $10M to Turn Cloud Detection into Prevention appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶