• Advanced steganography techniques are becoming increasingly central to state-sponsored cyber operations.

    Recent analysis has exposed two Chinese technology companies, BIETA and CIII, that allegedly provide sophisticated steganography solutions to support advanced persistent threat campaigns.

    These organizations operate as front companies linked to China’s Ministry of State Security, playing a critical role in modernizing the country’s intelligence gathering capabilities.

    BIETA, formally known as the Beijing Institute of Electronics Technology and Application, operates from a location adjacent to the MSS headquarters in Beijing.

    The company maintains close institutional ties with government agencies and universities, including the University of International Relations, which functions as an MSS subsidiary.

    CIII, operating as Beijing Sanxin Times Technology Co., Ltd., presents itself as a state-owned enterprise while reportedly providing forensic and counterintelligence support services.

    Both organizations maintain detailed focus on developing advanced hiding techniques for malicious payloads.

    Security analysts at Telsy identified that these companies have dedicated substantial resources to steganographic research and development.

    Analysis of academic publications reveals that approximately 46 percent of BIETA’s 87 research papers published between 1991 and 2023 specifically address steganography.

    The companies have obtained multiple software copyrights for techniques including audiovisual-to-voice conversion systems and JPEG image forensic differentiation methods, both registered in 2017.

    Steganography implementation strategies

    The steganography implementation strategies employed represent a significant technical shift in APT operations.

    Rather than relying solely on traditional encryption, threat actors use Least Significant Bit steganography to conceal .NET payloads within image files.

    BIETA’s research extends beyond standard JPEG formats to include MP3 audio and MP4 video files for covert information transmission.

    Historical APT groups including APT1, Mirage, Leviathan, and Pirate Panda have all utilized similar techniques to distribute backdoors like TClinet and Stegmap without triggering conventional detection systems.

    The technical innovation extends to emerging technologies, with BIETA researchers exploring Generative Adversarial Networks for steganographic applications.

    This advancement suggests future APT operations may employ AI-driven methods to generate undetectable carrier files.

    Understanding these techniques remains essential for defensive security teams as state-sponsored actors continue refining their ability to hide malicious communications within seemingly innocuous media files, making detection increasingly challenging for traditional security monitoring tools and approaches.

    Follow us on Google News, LinkedIn, and X to Get More Instant Updates, Set CSN as a Preferred Source in Google.

    The post Chinese Front Companies Providing Advanced Steganography Solutions for APT Operations appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A new remote access trojan dubbed KimJongRAT has surfaced, posing a severe threat to Windows users.

    This sophisticated malware is believed to be orchestrated by the Kimsuky group, a threat actor with alleged state backing.

    The campaign typically begins with a phishing email containing a deceptive archive named National Tax Notice, which lures unsuspecting victims into initiating the infection chain.

    Upon opening the malicious archive, users are presented with a shortcut file disguised as a legitimate PDF document.

    Tax notice.pdf (Source - Alyac)
    Tax notice.pdf (Source – Alyac)

    When executed, this shortcut file triggers a hidden command that decodes a Base64 URL and abuses the legitimate Microsoft HTML Application utility to contact a remote server.

    This process stealthily downloads an additional payload known as tax.hta, effectively bypassing standard security checks.

    Alyac security analysts identified that this loader script is implemented in VBScript and employs clever evasion techniques.

    The malware attempts to evade detection by utilizing legitimate services like Google Drive to host its malicious components.

    Once active, the loader retrieves both decoy documents to trick the user and the actual malicious binaries required for the next stage of the attack.

    Exfiltration of sensitive data

    The primary objective of this campaign is the exfiltration of sensitive personal and financial data.

    The malware targets a wide array of information, including system details, browser storage data, and encryption keys.

    It specifically hunts for cryptocurrency wallet information and credentials for communication platforms like Telegram and Discord, making it a highly dangerous tool for identity theft and financial fraud.

    The most notable aspect of KimJongRAT is its ability to adapt its behavior based on the target environment’s security posture.

    The malware executes a specific VBScript command to check the status of Windows Defender before proceeding.

    It uses the code snippet Set exec = oShell.Exec(ss) followed by If InStr(output, “STOPPED”) > 0 Then to determine if the security service is active.

    If Windows Defender is disabled, the malware downloads a file named v3.log, which executes the primary payload.

    Conversely, if security is active, it retrieves an alternative file called pipe.log to circumvent detection.

    Regardless of the path taken, the malware establishes persistence by registering itself in the system registry, ensuring it runs automatically to transmit stolen data periodically.

    List of cryptocurrency wallets hijacked by malware (Source - Alyac)
    List of cryptocurrency wallets hijacked by malware (Source – Alyac)

    While the List of cryptocurrency wallets hijacked by malware highlights the breadth of targeted applications, it also highlights the specific financial intent behind this tailored threat.

    Follow us on Google News, LinkedIn, and X to Get More Instant Updates, Set CSN as a Preferred Source in Google.

    The post KimJongRAT Attacking Windows Users via Weaponized .hta Files to Steal Logins appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A sophisticated cyberespionage campaign dubbed “Operation Hanoi Thief” has surfaced, specifically targeting IT professionals and recruitment teams in Vietnam.

    Discovered on November 3, 2025, this threat activity employs a complex multi-stage infection chain designed to harvest sensitive browser credentials and history.

    The attackers leverage a malicious spear-phishing strategy, distributing a ZIP archive named Le-Xuan-Son_CV.zip, which masquerades as a legitimate job application from a software developer based in Hanoi.

    The infection initiates when a victim interacts with a shortcut file, CV.pdf.lnk, contained within the archive. This file triggers a sequence of events utilizing “Living off the Land” (LOLBin) tactics.

    Specifically, it abuses the Windows ftp.exe utility with the -s flag to execute a batch script hidden within a pseudo-polyglot file named offsec-certified-professional.png.

    This file dual-functions as a harmless image lure and a malicious container, effectively evading traditional detection mechanisms by burying its payload within legitimate image headers.

    Data Exfiltration (Source - Seqrite)
    Data Exfiltration (Source – Seqrite)

    This command line argument is a critical indicator of the attack’s stealthy nature.

    Seqrite security analysts identified that this campaign is likely of Chinese origin, citing overlaps in tactics with previous state-sponsored activities.

    The primary objective appears to be intelligence gathering, focusing on the theft of login data and browsing habits from victims in the technology and HR sectors.

    By exploiting the trust inherent in recruitment processes, the threat actors successfully bypass initial perimeter security layers.

    Technical Analysis of the LOTUSHARVEST Payload

    The core of this attack is the execution of the LOTUSHARVEST implant. Once the initial script runs, it abuses DeviceCredentialDeployment.exe to conceal its command-line activities and renames system utilities like certutil.exe to lala.exe to bypass monitoring.

    In the infection chain, the script then extracts a base64-encoded blob from the polyglot file, decoding it into a malicious DLL named MsCtfMonitor.dll.

    Infection Chain (Source - Seqrite)
    Infection Chain (Source – Seqrite)

    This DLL is side-loaded using a legitimate ctfmon.exe binary copied to the C:\ProgramData directory.

    LOTUSHARVEST functions as a robust information stealer, employing anti-analysis checks like IsDebuggerPresent and IsProcessorFeaturePresent to crash if analyzed.

    It targets Google Chrome and Microsoft Edge, querying SQLite databases to extract the top 20 visited URLs and decrypting up to five saved credentials using CryptUnprotectData.

    Finally, the stolen data is formatted into JSON and exfiltrated via an HTTPS POST request to the attacker-controlled server eol4hkm8mfoeevs.m.pipedream.net/service.

    Follow us on Google News, LinkedIn, and X to Get More Instant Updates, Set CSN as a Preferred Source in Google.

    The post Operation Hanoi Thief Attacking IT Professionals with Pseudo-Polyglot Payload to Hide Malware appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • With the holiday shopping season kicking into high gear, a massive cybersecurity threat has emerged, putting online shoppers at significant risk.

    A coordinated campaign has been discovered, involving the registration of over 2,000 fake holiday-themed online stores.

    These malicious sites are designed to lure unsuspecting consumers with the promise of steep discounts, only to steal their payment information and personal data.

    The scale of this operation is vast, with two distinct clusters of fraudulent storefronts identified, both employing sophisticated tactics to appear legitimate and deceive shoppers.

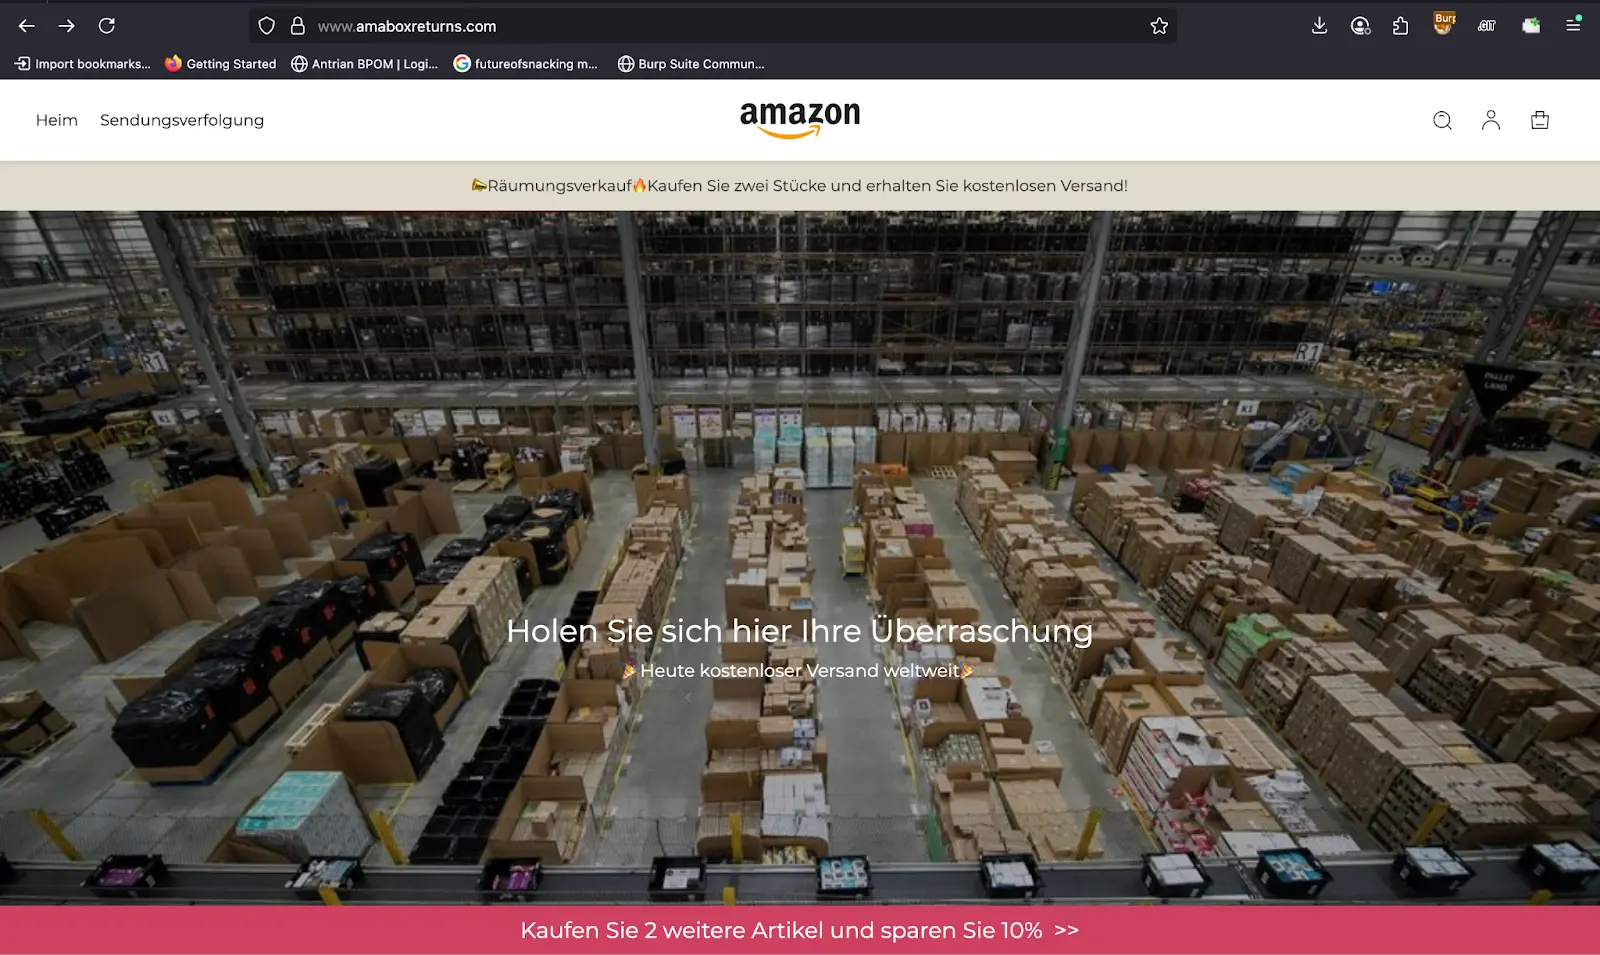
    The first cluster primarily consists of typosquatted domains mimicking Amazon, while the second spans a wide array of “.shop” domains impersonating well-known brands such as Apple, Samsung, and Ray-Ban.

    These fake stores are not isolated incidents but part of a large-scale, automated campaign. The threat actors behind this operation have timed their attack to coincide with peak shopping periods like Black Friday and Cyber Monday, when consumers are actively hunting for bargains and may be less cautious about unfamiliar websites.

    Fake storefront (Source - CloudSEK)
    Fake storefront (Source – CloudSEK)

    CloudSEK security researchers noted the coordinated nature of these scams, identifying the use of identical phishing kits, recurring website templates, and shared infrastructure across the network of fake stores.

    This level of coordination suggests a well-organized and resourced operation. The impact on consumers is severe, ranging from direct financial losses to the long-term risks of identity theft.

    Furthermore, these scams erode trust in legitimate online retailers and the e-commerce ecosystem as a whole.

    Infection and Deception Tactics

    The modus operandi of these fake stores is both simple and effective. They leverage a combination of social engineering and technical evasion to trick users and avoid detection.

    The sites are designed to look like professional e-commerce platforms, complete with holiday-themed banners, countdown timers creating a false sense of urgency, and fake “trust badges” to build credibility.

    Fabricated “recent purchase” pop-ups are also used to create social proof and pressure visitors into making a purchase.

    Fake Landing Page (Source - CloudSEK)
    Fake Landing Page (Source – CloudSEK)

    When a user attempts to buy a product, they are redirected to a shell checkout page designed to harvest their billing and payment details.

    These shell websites often use unflagged domains to process transactions, allowing the attackers to bypass fraud detection systems.

    Fake & Impersonating Domains:-

    Domain ClusterImpersonated BrandFake Domain Examples
    Cluster A (Amazon-themed)Amazonamaboxhub.com, amawarehousesale.com, amaznshop.com
    Cluster B (.shop domains)Xiaomixiaomidea.shop
    Jo MaloneJomalonesafe.shop
    FujifilmFujifilmsafe.shop
    SamsungSamsungsafe.shop
    A popular brand[brand]safe.shop or [brand]fast.shop

    The investigation also revealed that a shared Content Delivery Network (CDN), cdn.cloud360.top, was used to serve assets to over 750 of the fake stores, further highlighting the centralized nature of the campaign.

    A recurring JavaScript file, identified by its unique SHA-256 hash, was also found across numerous malicious .shop domains, controlling the fraudulent checkout process.

    Follow us on Google News, LinkedIn, and X to Get More Instant Updates, Set CSN as a Preferred Source in Google.

    The post Hackers Registered 2,000+ Fake Holiday-Themed Online Stores to Steal User Payments appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • New York, New York, December 1st, 2025, CyberNewswire BreachLock, the global leader in Penetration Testing as a Service (PTaaS), has been named a Leader and Fast Mover in the 2025 GigaOm Radar Report for PTaaS for the third year in a row. The GigaOm Radar Report for PTaaS is published annually to help security leaders and practitioners […]

    The post BreachLock Named a Leader in 2025 GigaOm Radar Report for Penetration Testing as a Service (PTaaS) for Third Consecutive Year appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • New York, New York, December 1st, 2025, CyberNewswire

    BreachLock, the global leader in Penetration Testing as a Service (PTaaS), has been named a Leader and Fast Mover in the 2025 GigaOm Radar Report for PTaaS for the third year in a row.

    The GigaOm Radar Report for PTaaS is published annually to help security leaders and practitioners evaluate PTaaS solutions for more informed decision-making. This year’s report evaluated 16 of the top PTaaS providers in the market based on key feature capabilities, their ability to meet enterprise business requirements, deployment models, and other important decision-making criteria.  

    2025 marks the third year in a row BreachLock has been positioned as a leader and fast mover in the Maturity and Platform Play Quadrant of the GigaOm PTaaS Radar Report, demonstrating both its consistency and platform innovations geared towards enterprise customers.  

    BreachLock and the 15 other PTaaS providers evaluated in the report were scored based on the following key feature capabilities: 

    1. Built-in vulnerability scanners 
    2. Integration with SDLC technologies 
    3. API access 
    4. Customizable testing methodologies 
    5. Retesting of findings 
    6. Streamlined procurement 
    7. Crowdsourcing pentesters 
    8. Compliance Reporting 

    BreachLock scored highly in all but one category, with the exception of crowdsourcing pentesters, helping earn its position as a leader and fast mover in this year’s report. While crowdsourcing pentesters has its benefits, BreachLock’s 100% in-house team of highly skilled, certified expert pentesters offers enterprises a higher level of consistency, scalability, and reliability to guarantee quality results when penetration testing critical systems and applications. 

    BreachLock also scored highly in GigaOm’s business criteria comparison focused on non-functional requirements buyers commonly consider for purchase decision-making to determine a solution’s impact on an organization. The five factors evaluated as part of the business criteria comparison included: 

    1. Flexibility 
    2. Scalability 
    3. Speed 
    4. Risk Reduction 
    5. Cost 

    While the key capabilities and business criteria scores were the most heavily weighted criteria for radar positioning, GigaOm also scored each provider on emerging features, which scored providers’ integration capabilities with attack surface management (ASM) and private PTaaS platforms. 

    Lastly, GigaOm’s solution overview of BreachLock highlights its unified, cloud-native platform that combines PTaaS, Continuous Threat Exposure Management (CTEM), and Adversarial Exposure Validation (AEV), addressing how it enables organizations to transition from traditional point-in-time security testing to continuous, threat intelligence-driven offensive security. 

    Commenting on BreachLock’s position in the report, Seemant Sehgal, Founder & CEO of BreachLock, expressed, “It’s an honor to be recognized by GigaOm as a PTaaS leader for the third year in a row, which is a clear reflection of BreachLock’s constant innovation and focus on enterprise needs.” He added, “The world is evolving fast with Agentic AI—and so are attackers. BreachLock is one of the very few offensive security companies leading this shift. Our unified, agentic, and automation-first approach is reshaping enterprise-scale offensive security, and we’re proud to be ranked alongside the best—driving innovation, speed, and measurable outcomes for our clients.” 

    Chris Ray, author of the GigaOm Radar Report for PTaaS, highlighted BreachLock’s strengths in the report, writing, “BreachLock excels for enterprises with CI/CD pipelines requiring continuous security validation through its deep SDLC integration, risk-contextualized findings, and pipeline security gates. Its unified PTaaS and ASM solution provides seamless visibility for organizations transitioning from periodic to continuous security testing, eliminating blind spots between scheduled assessments.” 

    About BreachLock 

    BreachLock is a global leader in offensive security, delivering scalable and continuous security testing. Trusted by global enterprises, BreachLock provides human-led and AI-powered Attack Surface Management, Penetration Testing as a Service (PTaaS), Red Teaming, and Adversarial Exposure Validation (AEV) solutions that help security teams stay ahead of adversaries. 

    With a mission to make proactive security the new standard, BreachLock is shaping the future of cybersecurity through automation, data-driven intelligence, and expert-driven execution.

    Contact

    Senior Marketing Executive
    Megan Charrois
    BreachLock
    megan.c@breachlock.com

    The post BreachLock Named a Leader in 2025 GigaOm Radar Report for Penetration Testing as a Service (PTaaS) for Third Consecutive Year appeared first on Cyber Security News.
    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A newly discovered Windows malware packer named TangleCrypt has emerged as a serious threat in ransomware attacks, specifically designed to evade endpoint detection and response (EDR) solutions.

    The packer was first observed during a September 2025 ransomware incident involving Qilin ransomware, where threat actors deployed it alongside the ABYSSWORKER driver to disable security tools before encrypting victim systems.

    TangleCrypt works by hiding malicious payloads through multiple layers of encoding, compression, and encryption. The original executable is stored within PE resources using base64 encoding, LZ78 compression, and XOR encryption.

    This multi-layer approach makes it difficult for traditional security tools to detect the actual malware hidden inside the packed executable.

    WithSecure Labs security researchers identified the malware during an incident response investigation, recovering artifacts including two executables packed with TangleCrypt and VMProtect, along with a kernel driver masquerading as a CrowdStrike Falcon Sensor driver.

    The payload embedded in these executables was identified as STONESTOP, an EDR-killer tool that uses the ABYSSWORKER driver to terminate security processes running on the system forcibly.

    The packer employs string encryption and dynamic import resolving to hinder both static and dynamic analysis.

    Although malware authors commonly use these techniques, the TangleCrypt implementation lacks advanced anti-analysis mechanisms, making manual unpacking relatively straightforward for experienced analysts.

    Payload Execution Mechanism

    TangleCrypt supports two distinct methods for launching its payload, determined by a configuration string appended to the embedded executable.

    The first method, identified by the string “exex64_amd64_block_”, decrypts and executes the payload within the same process memory.

    The second method, marked with “exex64_amd64__riin”, creates a suspended child process and writes the decrypted payload into it before resuming execution.

    ProcessMonitor log of ‘b1.exe’ starting child process of itself (Source – Withsecure Labs)

    When executed, the loader first decrypts a small resource entry containing a numeric key, such as “175438”. This key is then used to XOR-decrypt the larger payload stored in the PE resources.

    The decryption process follows a specific sequence where a base64-encoded string is decoded, then LZ78 decompressed, decoded again from base64, and finally XOR-decrypted to reveal the original executable.

    Upon successful unpacking, the STONESTOP payload checks for administrative privileges and registers the ABYSSWORKER driver if elevated rights are present.

    The driver then terminates processes matching a predefined list of security product names, effectively blinding the system’s defenses before ransomware deployment begins.

    Follow us on Google News, LinkedIn, and X to Get More Instant Updates, Set CSN as a Preferred Source in Google.

    The post TangleCrypt Windows Packer with Ransomware Payloads Evades EDR Using ABYSSWORKER Driver appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Microsoft has acknowledged a frustrating new issue affecting users of the “new Outlook” for Windows, where Excel attachments fail to open if their filenames contain non-ASCII characters.

    The technical glitch, tracked under the reference ID EX1189359, triggers a vague error message advising users to “Try opening the file again later,” leaving many confused about the cause of the blockage.​

    The problem targets the modern “new Outlook” client explicitly and does not appear to impact the classic version of the software. According to Microsoft’s service health dashboard, the root cause lies in an encoding error within the request used to open the files.

    When an Excel file attached to an email includes non-standard characters such as accented letters, symbols, or non-English scripts, the application fails to process the filename correctly, resulting in an immediate error.​

    This issue has been ongoing since late November 2025, with initial reports surfacing around November 23. While the scope is limited to specific file naming conventions, the impact is significant for international users or organizations that frequently use non-ASCII characters in document titles.​

    Microsoft’s Response and Fix Status

    As of the latest update on December 1, 2025, Microsoft engineers have successfully developed a fix to address the missing encoding in file-handling requests.

    However, the solution is not yet available to all users. The company is currently in the validation phase, testing the deployment to ensure it resolves the error without introducing secondary issues.​

    Microsoft is also investigating why this encoding error occurred in the first place to prevent similar regressions in future updates. A further status update is expected by the evening of December 1, UTC time.​

    Until the patch is fully rolled out, Microsoft has provided two official workarounds for users who need immediate access to their spreadsheets:

    • Use Outlook on the Web (OWA): The web-based version of Outlook correctly processes these attachments, bypassing the client-side encoding failure.​
    • Download the File Locally: Users can save the attachment to their computer first. Once the file is saved to a local drive, it can be opened directly in Excel without triggering the Outlook previewer error.​

    This incident joins a growing list of pains for the new Outlook client, which has faced scrutiny from power users for feature-parity gaps compared to the classic COM-based application. Admin administrators can track the progress of the fix in the Microsoft 365 admin center under EX1189359.​

    Follow us on Google News, LinkedIn, and X for daily cybersecurity updates. Contact us to feature your stories.

    The post Microsoft Confirms New Outlook Bug Blocking Excel Attachments appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • India’s telecommunications ministry has reportedly asked major mobile device manufacturers to preload a government-backed cybersecurity app named Sanchar Saathi on all new phones within 90 days. According to a report from Reuters, the app cannot be deleted or disabled from users’ devices. Sanchar Saathi, available on the web and via mobile apps for Android and iOS, allows users to report

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A sophisticated Advanced Persistent Threat group known as Bloody Wolf has intensified its cyber espionage operations across Central Asia, targeting government and private sectors.

    Since late June 2025, the group has orchestrated spear-phishing campaigns primarily focusing on organizations within Kyrgyzstan and Uzbekistan.

    By meticulously impersonating state entities such as the Ministry of Justice, the attackers successfully deceive victims into compromising their systems.

    The primary vector involves weaponized PDF documents sent via email, mimicking official correspondence. These documents often bear titles suggesting urgent legal matters or case materials, compelling recipients to interact with embedded links.

    Once clicked, these links initiate a multi-stage infection process designed to bypass traditional security defenses and establish long-term access to the victim’s network.

    Group-IB security analysts identified this surge, noting the group shifted from commercial malware like STRRAT to deploying the legitimate, yet weaponized, NetSupport Remote Administration Tool.

    This strategic pivot allows attackers to blend in with normal administrative traffic, making detection significantly more challenging for corporate security teams.

    The campaigns demonstrate a high level of regional adaptation, including the use of local languages and geo-fencing techniques to restrict payload delivery to targets within specific countries.

    The impact is profound, granting attackers full remote control over infected endpoints. This access facilitates data exfiltration, system inventory surveillance, and lateral movement within critical infrastructure networks.

    Infection Chain

    Bloody Wolf’s technical strategy relies on malicious Java Archive files to execute the payload. Victims interacting with the lure are prompted to update Java, a pretext masking the malicious loader’s execution.

    The JAR files, compiled with Java 8, are unobfuscated but highly effective. In the Uzbekistan campaign, the infrastructure employed geo-fencing, where only requests originating from within the country triggered the download of the malicious JAR, while others were redirected to legitimate government portals.

    Persistence functions code (Source - Group-IB)
    Persistence functions code (Source – Group-IB)

    Once executed, the JAR loader ensures persistence through redundant methods. The malware drops a batch file into the Windows Startup folder and modifies registry keys, executing commands like cmd.exe to ensure the RAT launches upon reboot.

    Fake error message pop-ups (Source - Group-IB)
    Fake error message pop-ups (Source – Group-IB)

    Additionally, it creates a scheduled task using schtasks to guarantee execution. This redundancy ensures that the NetSupport RAT remains active on the system, allowing the attackers to maintain a persistent foothold while displaying fake error messages, to distract the user from the background malicious activity.

    Follow us on Google News, LinkedIn, and X to Get More Instant Updates, Set CSN as a Preferred Source in Google.

    The post Bloody Wolf Hackers Mimic as Government Agencies to Deploy NetSupport RAT via Weaponized PDF’s appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶