

-
Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword. “Compared with the variants we usually observe, P7 reduces its on-device footprint, adds on-device keychain and crypto-wallet theft, and adds two way C2 communication with the attacker’s infrastructure,” iVerify said in a new report published Thursday. The name
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
Four more U.S. states sued router maker TP-Link Systems on October 6, bringing the total to five, with Texas filing a suit in February. Florida, Iowa, Montana and Nebraska allege the California company misled buyers about how secure its routers are and how separate it is from China. TP-Link denies the claims and says it will fight them in court. TP-Link Systems is based in
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
Security researchers have published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that gives attackers root access before anyone approves the connection. AnyDesk patched the flaw in version 8.0.3 in June, but its changelog described the fix only as “fixed a bug that could lead to a crash,” with no CVE assigned and no security
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
 Sausalito, Calif. – Oct. 9, 2026
– Hosted by Everfox. REGISTER NOW
Join senior government, defense, and industry leaders for a day exploring how trusted mission data and operational AI are transforming national security. REGISTER NOW for Advantage 26 on Oct. 21 in Reston, Virginia.
Through keynote presentations, executive discussions, panels, and fireside chats, attendees will gain insights into AI adoption, coalition data sharing, mission infrastructure, insider risk, and the future of the defense industrial base, while connecting with peers through networking sessions, an executive lunch, the Mission Innovation Showcase, and an evening reception.
Hear perspectives from leaders representing Anthropic, Palantir, OpenAI, Anduril, AWS and more, alongside senior government and industry voices.
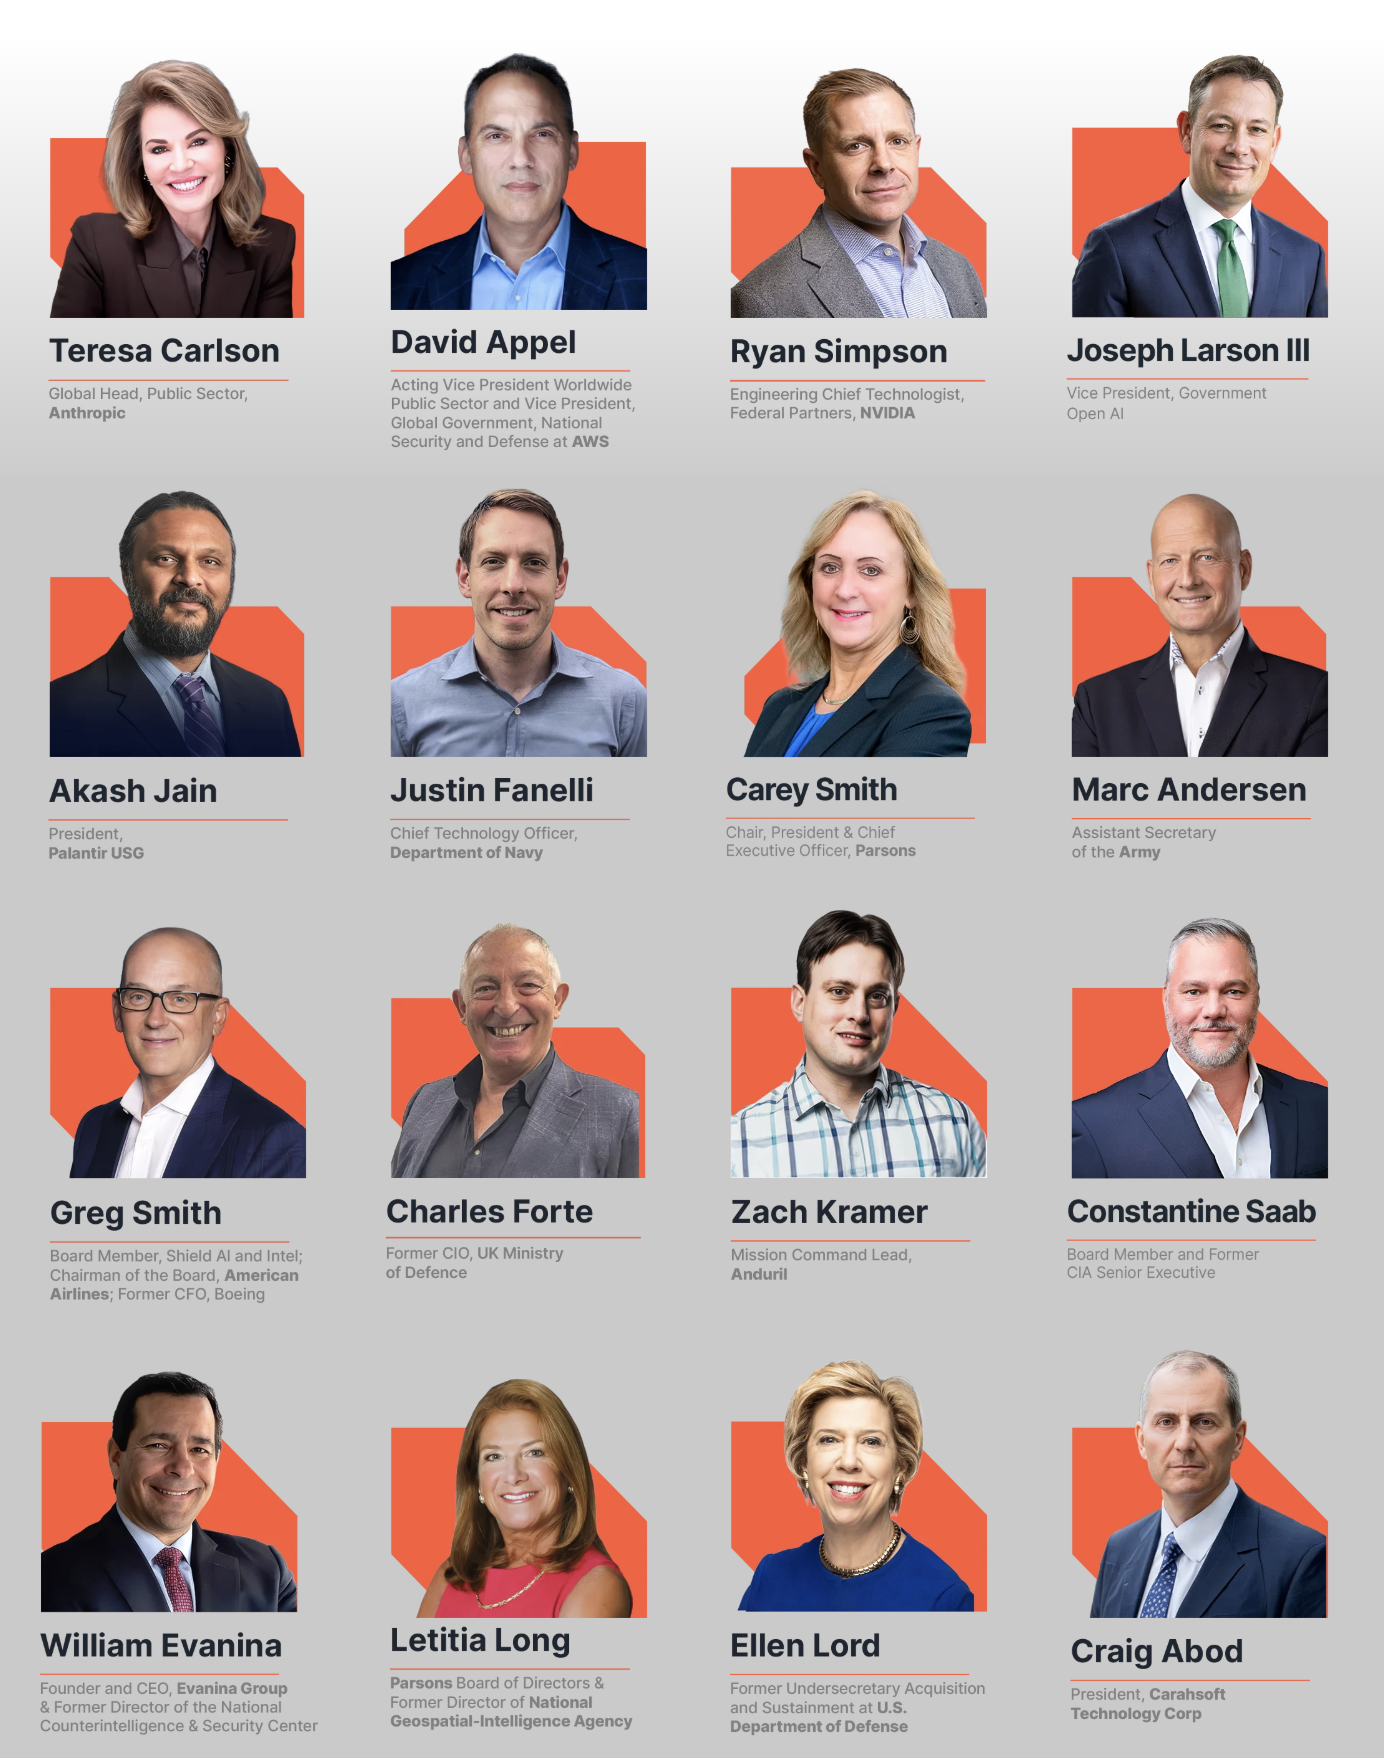
ADVANTAGE 26 CONVERSATIONS:
- Trusted Mission Data. How trusted data becomes the foundation for mission speed, AI adoption and decision advantage.
- Operational AI. Moving AI from experimentation to operational capability across national security environments.
- The Modern Defense Industrial Base. How government, established industry and emerging defense technology companies are reshaping the defense
industrial base. - Secure Data Sharing & Coalition Operations. Enabling trusted information to move securely across organizations, classifications and coalition partners.
- Securing the Human & Data Environment. Addressing insider risk and protecting trusted information as missions, technologies and collaboration
become more connected.
REGISTER NOW for Advantage 26 on Oct. 21 in Reston, Virginia.
FULL AGENDA including speakers, topics, breakfast, executive networking lunch, and the Mission Innovation Showcase.
CONTACT US with questions via email at advantage26@everfox.com.
Everfox delivers trusted connectivity to protect the world’s most critical environments and safeguard the sensitive data powering decision advantage. Built for mission-critical operations, Everfox protects what matters most by securing how data moves, how users access it, and how threats are neutralized across every domain.
The post Advantage 26: The Trusted Mission Data Summit. Oct. 21, 2026. Reston, Virginia appeared first on Cybercrime Magazine.
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
Anthropic on Thursday unveiled OSS Scanner as an opt-in vulnerability scanner to help secure the open-source ecosystem using artificial intelligence (AI). “It’s an opt-in service informed by our experience using Claude to find vulnerabilities during Project Glasswing,” Anthropic said. “Projects that join will receive thorough, periodic security scans by our strongest models at no cost.”
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
Threat actors have been observed exploiting two recently disclosed flaws in the AhsayCBS backup utility to seize control of affected devices and deploy web shells and XMRig cryptocurrency miners. Details of the flaws are below – CVE-2026-105133 (CVSS v4 score: 5.5) – An improper authentication vulnerability in the checkSysPwd() function in the “com/ahsay/obs/api/ApiStructsAction.java”
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
Learn how businesses can use AI to reduce repetitive work, improve workflows, connect information, and support better everyday decisions.
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
A security vulnerability has been identified in React Server Components deployments using specific vulnerable releases of React 19. An attacker can exploit this flaw to create a denial-of-service condition through specially crafted HTTP POST requests, as detailed in CVE-2026-23870. React Server Components Vulnerability Tracked as CVE-2026-23870 and GHSA-rv78-f8rc-xrxh, this high-severity vulnerability affects React Server Components […]
The post React Server Components Vulnerability Lets Attackers Freeze Next.js Servers With a Single Request appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon. The vulnerabilities in question are listed below – CVE-2015-3306 (CVSS score: 10.0) – An improper access control vulnerability in ProFTPD that could allow
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
CastleStealer, a C# information stealer first publicly identified in April 2026, has expanded its capabilities beyond credential theft. New samples analyzed by Flashpoint bypass Chromium app-bound encryption, support remote command execution, and transmit stolen data through small, encrypted TCP exchanges instead of uploading a single archive. Flashpoint has not observed widespread adoption among threat actors. […]
The post CastleStealer Malware Bypasses Chromium ABE and Adds Remote Command Execution Capabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
