

-
Attackers are exploiting a critical flaw in Cisco Secure Email Gateway that lets a sender with no login write files to the appliance’s operating system, Cisco said in an advisory on Wednesday. The attacker sends an email with a crafted attachment through the gateway and, if it succeeds, could then run commands as root. The appliance filters an organization’s email for spam, malware,
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
Defense Secretary Pete Hegseth’s vision for the planned Autonomous Warfare Command over the next two years “is that we're still iterating, we're still adapting, we're still learning, and we're moving faster and faster because we're doing it. We understand how to do it better with each iteration.”
Hegseth sat down to discuss the Defense Department’s efforts to advance its autonomous capabilities with the service secretaries and the Pentagon’s top civilian for special operations during a panel Wednesday at AUSA’s annual meeting in Washington, D.C., but the discussion offered few details on what the forthcoming AUTOWARCOM, scheduled to activate by Oct. 1, 2027, will look like and how it will accomplish its mission.
The secretary, who has ordered cuts to and flag officer positions across the military services, was asked why a four-star combatant command is the correct vehicle to speed up acquisition and fielding of autonomous systems. He said that sometimes a general is the best person to get the job done.
“Let's put rank where we need it to ensure we can drive change quickly,” Hegseth said. “We're going to use rank to drive change with the right people in those positions, but not just legacy formations and commands which have gathered over time and haven't led to battlefield efforts.”
He did not say whether a search is on for commander candidates and what kind of experience he’s looking for.
The Army on Tuesday announced it would rename its Futures and Concepts Command, headed by Lt. Gen. Mac McCurry, to Futures and Autonomy Command, which will be the service’s component command nested under AUTOWARCOM.
The other services haven’t made any announcements about their own forthcoming autonomy commands. The Navy did not immediately respond to a query from Defense One on its plans. The Air Force referred questions to Hegseth’s office.
Much of the discussion focused on the services’ current use of unmanned platforms, as distinct from autonomous systems, which generally function without a human operator.
Hegseth said that AUTOWARCOM would deal not just with procurement, but also with training and doctrine around unmanned systems.
Two of the speakers mentioned an Army effort to open up its test ranges to private companies that make “drone, counter-drone, and long-ranges fires solutions.” Announced in August, the Army Permissive Test Range Expansion effort includes a website that promises a response within four weeks to companies that apply to use the ranges.
“Before, we kept these test ranges to ourselves for our own purposes. We were prioritizing and micromanaging the use of these ranges,” Acting Army Secretary Adam Telle said Wednesday. “To the degree that our bureaucracy is living in the way of our most innovative people from iterating quickly, it's a shame.”
The Army is also working to open “theater innovation labs” outside the United States, said Derrick Anderson, assistant defense secretary for Special Operations and Low-Intensity Conflict. Anderson said the labs, which are being launched in conjunction with U.S. Special Operations Command, meant that “operators sitting here stateside iterating on these autonomous systems” would have a “place to go and iterate” when they go abroad as well.
Anderson added that the Defense Autonomous Warfare Group run by the Defense Innovation Unit will be folded into SOCOM’s new Task Force Autonomous Warfare.
One day before Hegseth took the AUSA spotlight, Army officials had offered some insight into their plans for autonomous warfare on Tuesday, including “appropriate levels of human judgment,” Army Chief Technology Officer Alex Miller said during a panel.
“Things like counter-battery fire, things like air and missile defense, things that happen at a superhuman speed and scale—want to have humans on the loop for decisions, but then we cannot be limited by you know the 20 watts that have up here,” Miller said, pointing to his head. “If we are taking thousands of drones or hundreds of rounds, we can't put that on a human. We want to enable them to be a crew chief for superintelligence and autonomy.”
On Wednesday’s panel, Air Force Secretary Troy Meink said his service is experimenting with autonomous fighter aircraft at Creech Air Force Base in Nevada.
Last year, the Pentagon came under fire for its intentions around autonomous capabilities when AI company Anthropic, then a vendor to the Defense Department, protested the potential use of its models in support of lethal autonomous weapons and mass domestic surveillance.
Currently, artificial intelligence is used in collecting intelligence, identifying battlefield and data management. AUTOWARCOM would ostensibly be an entire combatant command built around autonomous platforms, but none of the senior officials on stage Wednesday identified any of the advancements the department hopes to make in their use.
“It will be a leader in the way we fight going forward, and I think we'll look back and say that was a no-brainer,” Hegseth said. “We should have done it 10 years earlier, but at least we did it.”
Lauren Williams contributed to this report.
]]>¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
The Trump administration’s retreat from programs that track foreign influence operations has weakened various cross-sector relationships used to identify and confront those campaigns as midterm elections fast approach — even as artificial intelligence makes those operations easier to deploy — multiple sources told Nextgov/FCW.
State officials say they are receiving fewer election-specific federal briefings than in previous cycles, while others who track foreign influence have observed routine exchanges with government and technology companies fall away. Some also note that federal workforce departures have weakened cooperation with outside partners, including social media platforms, to track false information online.
While the federal government continues to gather intelligence on foreign threats to U.S. elections, some of those who lean on those findings say federal agencies are less reliably sharing information with non-federal researchers and state officials responsible for countering those campaigns. That cooperation began to weaken before President Donald Trump returned to office, and his administration has since dismantled several programs dedicated to countering the problem.
This story is based on interviews with current and former federal officials, state election officials and specialists in cybersecurity and influence operations. Several people spoke on the condition of anonymity to be candid about their views and for fear of retribution. Their concerns come as fast-evolving AI tools now allow foreign influence operators to do more than just generate fake images or audio, instead helping them produce plausible-sounding messages, find audiences to target and autonomously adjust campaigns at a scale not seen before.
The Cybersecurity and Infrastructure Security Agency referred questions about foreign malign influence to the Justice Department, saying that influence operations fall outside CISA’s mission. DOJ did not immediately respond to a request for comment.
“Election security is national security, and protecting our critical infrastructure remains a top priority for the Trump Administration, DHS, and CISA,” a CISA spokesperson said. “CISA works closely with intelligence and law enforcement partners to monitor threats to U.S. critical infrastructure, including election infrastructure.”
The spokesperson added that the agency is committed to supporting state and local election officials “to protect election infrastructure and safeguard our democracy.”
The Office of the Director of National Intelligence did not respond to a request for comment.
Foreign influence operations aim to shape what people believe and how they act, often without revealing who is behind the message. Around elections, that can mean spreading false voting information, stoking political divisions or casting doubt on results. Such messages can be harder to question when they appear to come from or be amplified by fellow Americans and reinforce views people already hold.
One election nonprofit official told Nextgov/FCW that, during the November 2024 election, they received an early-morning text from a colleague in Georgia asking about bomb threats at voting sites, which U.S. officials later deemed may have been tied to Russia. The official was sitting in CISA’s election operations room. Finding out whether other jurisdictions were facing similar threats meant simply walking across the room and asking federal personnel.
“Any time you have federal support to help connect the dots, it’s a game-changer,” the official said, noting that they have not been alerted to or invited to a CISA elections operations room for the coming midterms.
The CISA spokesperson said that, before and during Election Day, the agency will “activate an Incident Coordination Group to establish a unified operational picture, rapidly share critical information, coordinate essential services for stakeholders in the field and strengthen incident response within its mission and authorities.”
Bret Schafer, senior director of policy and research for information operations at the Institute for Strategic Dialogue, said efforts to bring government, technology companies and researchers together grew during Trump’s first term, after Russia’s interference attempts in the 2016 election exposed gaps in their understanding of foreign campaigns.
Each could see activity the others could not. Sharing those findings helped them recognize operations that might otherwise go unnoticed, Schafer said last week on a panel at a national-security law conference hosted by the American Bar Association.
Those routine exchanges with the government have become harder to sustain. Now, “civil society is out on both sides,” he said, adding that he had gone at least two years without an information-sharing conversation with a relevant technology company, and a couple of years without one involving the government.
Much of that cooling began in the Biden administration, when GOP litigation over federal interactions with social media companies made participants more cautious. The Trump administration has gone further. It shuttered CISA work focused on election disinformation, disbanded the FBI’s Foreign Influence Task Force and closed the State Department’s office for countering foreign information threats, all largely on censorship grounds. The ODNI Foreign Malign Influence Center also faced a similar fate last August under then-director Tulsi Gabbard.
An office can retain its responsibilities while losing the relationships that helped it do the work, according to a person familiar with U.S. efforts to address influence operations. But someone who once knew exactly whom to call may find that their counterpart has departed, or that the people still there are unsure whether leadership supports exchanging information.
One current U.S. official described an environment that puts less public emphasis on election security at CISA and across the Department of Homeland Security than in previous cycles, with greater attention to other critical infrastructure matters, including water systems.
The official speculated that employees could hesitate to highlight their election security work after seeing others who worked on elections lose their jobs, though they noted they had not heard staff express that fear directly. The official also acknowledged that midterms generally receive less attention than presidential elections.
The administration has maintained that federal support continues. ODNI has assigned officials to coordinate election threat intelligence, while CISA outlined election support plans last month. Defense Secretary Pete Hegseth also directed Cyber Command and military intelligence agencies to prioritize foreign election threats and coordinate with the Department of Homeland Security last month.
A current Defense Department analyst argued that closing offices focused on tracking influence operations does not necessarily erase expertise, because personnel can continue the work elsewhere in government or as contractors. But it’s unclear how much of that work has continued, or whether those who left government still have access to relevant information and federal contacts they once relied on.
The analyst recalled a strong working relationship with Meta, which operates Facebook and Instagram, when they worked on those issues around two years ago. The analyst could not say whether those exchanges continue today.
Similarly, one former U.S. official recalled preparations for the 2020 election beginning roughly a year before Americans went to vote, with coordination growing more frequent as Election Day approached. Some calls included 80 to 100 participants, including private companies, discussing topics that included ballot security and broadcasting accurate voting information.
“Our nation’s security is best protected when private individuals, private sector, industry and government work together toward a common goal to protect our freedom and way of life, and that includes reporting suspicious and illegal activity and leveraging legal access and authorities to protect the American people and interests,” Erin Joe, special counsel at Wiley Rein LLP and a former senior FBI executive, told Nextgov/FCW in an interview.
At the ABA conference, former DHS Secretary Michael Chertoff argued that the government still has a role in helping people recognize deception. Officials can explain where a message came from or show that a supposed recording was generated by AI, without telling people which political views to accept.
“It is fighting bad speech with good speech,” Chertoff said.
A TikTok spokesperson referred Nextgov/FCW to a webpage outlining steps the company is taking to prepare for midterms and disrupt covert influence operations on its platform. Several other social media companies and AI firms — including Meta, X, Anthropic and OpenAI — did not respond to requests for comment.
Two state election officials described how their offices are responding to misleading information while receiving fewer election-specific federal briefings than in previous cycles.
One said identifying who is behind false messages can be difficult. Their office often focuses on information that could confuse people about when, where and how to vote, as well as threats to election workers.
When a misleading claim surfaces, communications staff and leadership decide whether responding would help voters or draw more attention to something that might otherwise fade away. Threats to election officials are referred to law enforcement, the official said.
The same official said they had not received an election-specific federal briefing “in quite some time,” although they attend regularly held CISA calls about software vulnerabilities and known flaws being exploited by hackers. Those discussions offer little information that is specific to elections, the official said. Monthly meetings through the state’s fusion center still bring together state, local and federal law enforcement to discuss threats to election officials.
The second official said their office sends a representative to federal election-threat briefings whenever they are available, but those briefings have occurred less frequently than in 2024.
That official nevertheless described their election offices as better prepared than in past years, with multiple backup plans, in case disruptions occur.
“We hope that we don’t have to use them. But if we do, they’re there,” the official said.
Those preparations come as AI has lowered the cost and effort required to conduct influence campaigns. AI has played a key role in helping to run these operations, from writing posts and distributing them to studying how people respond, said Snehal Antani, CEO and co-founder of cybersecurity company Horizon3.ai. Operators can test different messages and use the results to adjust their approach, and AI agents can automate much of that work, reducing the time and expertise it once required, he said.
“AI has dramatically reduced the skills required and dramatically accelerated the speed at which this cycle can be executed,” Antani said.
Another former U.S. official added that increasingly capable, downloadable open-source models allow smaller actors to undertake work that once required substantial investment and specialized engineering.
“The barrier to entry is much lower,” the former official said, adding that AI-generated text can blend into everyday online conversations and make it harder to spot than a manipulated image or video with visible flaws.
Russia is more likely to pursue more obvious inflammatory messaging this cycle, while China’s efforts may be more covert to serve longer-term objectives, said another current official, adding that both are expected to make greater use of AI. Pro-Iran outfits have especially leveraged AI more overtly in recent months amid the war that began in late February.
But the official cautioned that more powerful AI tools and more convincing content do not necessarily mean a foreign operation is changing how people vote. An image or video getting lots of views does not mean people believe it or will vote differently because of it, they added.
In some cases, an influence campaign may not even target eligible voters. For instance, content aimed at younger Americans could sway their political stances, but they may not be of legal age to cast a ballot.
And in other settings, a foreign influence operation may not be needed for an American to vote a certain way.
“If I see gas is $7 a gallon, I don’t necessarily need a lot more to go vote blue,” the official said, referring to California voters who have faced record-high fuel prices in some parts of the state.
These foreign threats come as political campaigns at home have increasingly used AI in their advertisements.
The growing use of AI-generated political videos could also make it harder to distinguish real footage from fabricated material, according to research released Wednesday by cybersecurity firm Check Point.
“Video is one of the easier ways to make a claim feel real, since people tend to trust what they can see and hear for themselves,” the company’s findings say. As AI-generated political content becomes more common, it becomes harder for voters to “trust that a video of a candidate is real” and easier for anyone “to dismiss a real video as fake.”
The scale and sophistication of false information today “makes our sensitivity to it a little bit more dull than perhaps in years past,” said Kimberly Kearney, a former CIA case officer.
“We as individuals have to have the desire to know whether what we’re consuming is true or false, or if it feeds into a narrative that is convenient or more comfortable for us,” she said in an interview. “So it starts with that cognitive honesty and awareness to want to know whether what you’re consuming is accurate or if it could have a bias to it.”
]]>¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
Attackers exploited a flaw in an optional Nextcloud app, Collabora Online – Built-in CODE Server, to plant web shells on Nextcloud servers. Three administrators reported the issue on GitHub, with the first logged attack on September 10. A web shell is a small file that executes any command an attacker sends via a web request, with the rights of the web server account. The flaw
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
Microsoft and Health-ISAC, along with the Japan Cybercrime Control Center (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption of three phishing kits, CoGUI (aka NX or FA), Haozi (aka Phoenix), and Iron Man System. “Since January 2026, the threat actors behind these kits have been responsible for
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
The U.S. Department of Justice (DoJ) on Tuesday charged 14 people and seized about 187 computers as part of its ongoing efforts to disrupt North Korea’s fraudulent remote IT worker (ITW) scheme. The indictment charges a mix of U.S. citizens and Chinese nationals for their roles in an IT worker conspiracy affecting more than 70 U.S. companies, charging them with wire fraud conspiracy, money
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
The United Kingdom has issued economic sanctions against Cryptomus, a chameleonic cryptocurrency platform that experts say serves as a major conduit for payments related to ransomware, narcotics, darknet markets, fraud and cybercrime services that are helping Russia circumvent existing financial restrictions.

Heleket’s support agent on Telegram claims, despite all evidence to the contrary, that it is not affiliated with Cryptomus. Image: Richard Sanders.
On October 8, the U.K. issued sanctions (PDF) against Cryptomus — previously known as Certa Payments and Xeltox Enterprises — for processing payments that benefit the Russian government and its financial institutions. The sanctions freeze any Cryptomus assets at U.K. banks, and bar British companies from offering it any business, virtual or otherwise. Also targeted in these sanctions were the virtual payment platforms VexPay, TokenSpot, and the Tsunami Payments service.
As explained in our December 2024 investigation, “How Cryptocurrency Turns to Cash in Russian Banks,” Cryptomus has been a key payment processor for dozens of Russian cryptocurrency exchanges and websites hawking cybercrime services. The company has changed its name several times since emerging in 2022, most recently to “Heleket” last year after Canada levied a record CAD $176 million fine against the platform for anti-money laundering violations.
The blockchain data-crunching firm Chainalysis said the U.K. sanctions target the broader infrastructure supporting Russia’s wartime economy.
“Cryptomus and Heleket have emerged as major payment hubs for illicit activity,” Chainalysis wrote in an October 8 blog post. “Together, these services received more illicit funds across tracked categories than the mixers in our dataset and the number of illicit counterparties surged to more than 900 in a single month in late 2025.”

The Cryptomus support bot on Telegram, responding on Oct. 8 to an inquiry by saying the platform was suddenly unable to process transactions.
In April 2026, the blockchain analysis firm TRM Labs found Cryptomus had processed more than $7 billion in transactions since its inception in 2022, including transactions associated with child sexual abuse material vendors, terrorist financing networks, and human trafficking operations.
TRM noted that Cryptomus’s transaction volume cratered after the platform instituted new “know your customer” or KYC rules, and that the cryptocurrency platform responded to the Canadian fines by launching Heleket as a parallel service that continued to offer no-KYC payment processing.
Richard Sanders is a blockchain analyst and investigator who spent months mapping out Cryptomus’s payment infrastructure and transacting with its customers. Sanders said the U.K. sanctions on Cryptomus are important because Canada’s sanctions against the platform were ultimately unenforceable and uncollectible.
“A fine doesn’t stop a cryptocurrency payment processor from processing payments,” Sanders wrote on LinkedIn. “Sanctions kill the operation. The distinction matters.”
As our 2024 investigation noted, Cryptomus shared a Vancouver address with dozens of other foreign currency dealers and money transfer businesses — none of which appeared to be physically located there. Following the CAD $176 million fine for alleged money laundering violations, Cryptomus appealed the penalty, launched Heleket as a parallel service, and kept on processing large volumes of sketchy transactions, Sanders said.
Sanders said the sanctions also are notable because they are the first known instance of a “Five Eyes” country (referring to the Australia, Canada, New Zealand, the U.K. and the U.S.) sanctioning a cryptocurrency operation incorporated in another Five Eyes jurisdiction.
Where do entities like Cryptomus and Heleket derive their authority to offer international financial services? The answer appears to involve fake financial institutions overseen by a phony regulatory body positioned in a country that is not widely recognized as a sovereign nation.
Our 2024 investigation found the sole shareholder of Cryptomus’s parent company Certa Payments was a 25-year-old Ukrainian woman who also headed several other firms, including the WS Management and Advisory Corporation, which bills itself as the regulatory body that exclusively oversees licenses for cryptocurrency, foreign exchange and online gaming businesses incorporated in the disputed region in northwest Africa known as the Western Sahara.
That entity’s website — crasadr.com — says it assists applicants with bank setup and formation, online gaming licenses, and the creation and licensing of foreign exchange brokers. One of Certa Payments’ former sites — certa[.]website — also shared a server with 12 other domains, including rasd-state[.]ws, a website for the Central Reserve Authority of the Western Sahara.
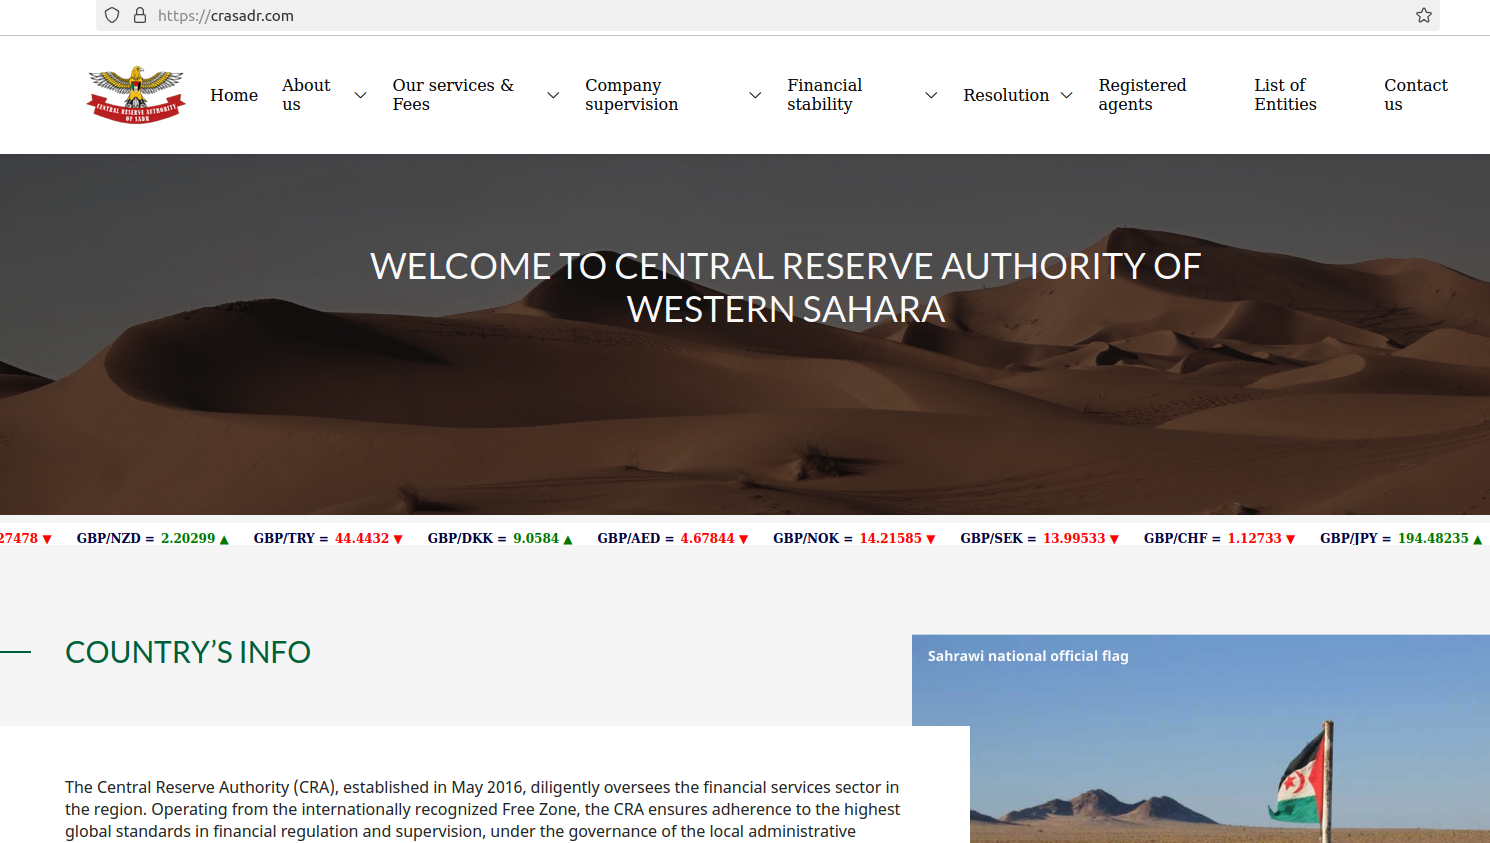
The website crasadr dot com, the official website of the Central Reserve Authority of Western Sahara, which lists the entities awarded licenses for cryptocurrencies, gaming and foreign exchange services.
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
Ransomware operators are extending their extortion tactics beyond corporate networks by threatening employees’ families and using artificial intelligence to enhance their attacks, according to the Semperis 2026 Ransomware Risk Report. Among the surveyed victims, 37% reported threats against their family members or friends, while 84% experienced attacks that involved AI in some form. The findings […]
The post Ransomware Gangs Threaten Employees’ Families as AI-Powered Attacks Escalate appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
·
 Sausalito, Calif. – Oct. 14, 2026
– Hosted by Everfox. REGISTER NOW
Join senior government, defense, and industry leaders for a day exploring how trusted mission data and operational AI are transforming national security. REGISTER NOW for Advantage 26 on Oct. 21 in Reston, Virginia.
Through keynote presentations, executive discussions, panels, and fireside chats, attendees will gain insights into AI adoption, coalition data sharing, mission infrastructure, insider risk, and the future of the defense industrial base, while connecting with peers through networking sessions, an executive lunch, the Mission Innovation Showcase, and an evening reception.
Hear perspectives from leaders representing Anthropic, Palantir, OpenAI, Anduril, AWS and more, alongside senior government and industry voices.
ADVANTAGE 26 CONVERSATIONS:
- Trusted Mission Data. How trusted data becomes the foundation for mission speed, AI adoption and decision advantage.
- Operational AI. Moving AI from experimentation to operational capability across national security environments.
- The Modern Defense Industrial Base. How government, established industry and emerging defense technology companies are reshaping the defense
industrial base. - Secure Data Sharing & Coalition Operations. Enabling trusted information to move securely across organizations, classifications and coalition partners.
- Securing the Human & Data Environment. Addressing insider risk and protecting trusted information as missions, technologies and collaboration
become more connected.
REGISTER NOW for Advantage 26 on Oct. 21 in Reston, Virginia.
FULL AGENDA including speakers, topics, breakfast, executive networking lunch, and the Mission Innovation Showcase.
CONTACT US with questions via email at advantage26@everfox.com.
Everfox delivers trusted connectivity to protect the world’s most critical environments and safeguard the sensitive data powering decision advantage. Built for mission-critical operations, Everfox protects what matters most by securing how data moves, how users access it, and how threats are neutralized across every domain.
The post Advantage 26: Join Cybersecurity Leaders From Anthropic, Palantir, OpenAI, Anduril, AWS. Oct. 21, 2026. Reston, Virginia appeared first on Cybercrime Magazine.
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
-
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday urged organizations to take steps to immediately update their Ivanti Connect Secure (ICS) appliances and deployments to the latest version following the disclosure of an actively exploited vulnerability. The security flaw, tracked as CVE-2026-104935 (CVSS score: 8.6), is a case of authentication bypass impacting ICS
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
¶¶¶¶¶
