• The consumer data broker Radaris.com has long had a reputation for ignoring requests to remove personal information from its vast empire of people-search services online. That reputation caught up with the company recently in a lawsuit alleging Radaris violated a New Jersey privacy law that provides for hefty fines against data brokers that publish personal information on state law enforcement officials. In the face of repeated stonewalling and prevarication by attorneys for Radaris, the judge in the case ordered that radaris.com and more than a dozen other data broker domains be transferred to the plaintiffs.
    The radaris.com website, prior to the domain transfer to Atlas.

    In February 2024, Radaris was sued by Atlas Data Privacy Corp, a company that has been pursuing data brokers alleged to be violating a New Jersey statute called Daniel’s Law. The statute allows state law enforcement officials, government personnel, judges and their families to have their information completely removed from commercial data brokers and people-search services, and provides for fines of $1,000 per violation against companies that ignore removal requests.

    Less than a month after Atlas sued Radaris, KrebsOnSecurity published a deep dive into the Radaris co-founders — Igor and Dmitry Lubarsky (also spelled Lybarsky) — Russian-born brothers living in Massachusetts who operate a dizzying array of people-search companies as well as a number of Russian language dating services and affiliate programs.

    Attorneys for the Lubarsky brothers threatened to sue for defamation if the story wasn’t removed and an apology issued. Their attorney asserted that our reporting was wildly inaccurate, and that the true owners of the company were Ukrainians living in Ukraine.
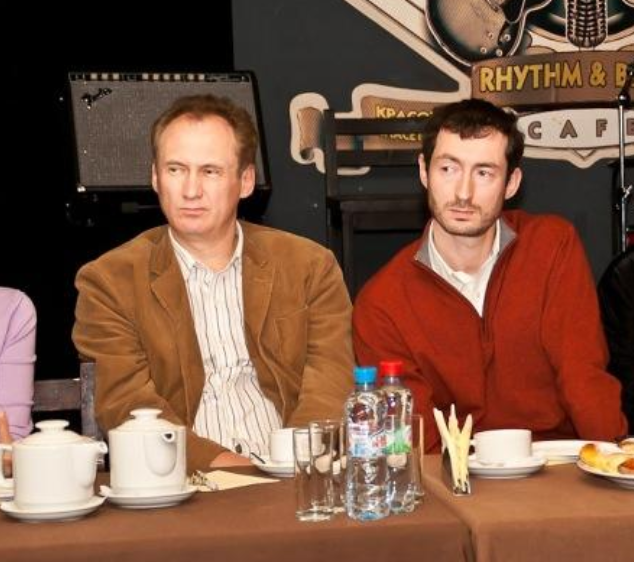
    The Lubarsky brothers Dmitry or “Dan” (left) and Gary/Igor.

    KrebsOnSecurity doubled down and showed how the Lubarsky brothers built and operated Radaris and other data broker companies using a fictitious CEO’s name. Our follow-up story noted that Radaris’s attorney — a lawyer with the Boston Law Group named Val Gurvits — admitted his clients had invented the CEO pseudonym “Gary Norden,” and that Radaris also had issued multiple press releases over the years that quoted the fake CEO while seeking money from potential investors.

    Attorneys for Radaris waited until the last minute to appear in court and contest what was all but certain to be a default judgment in favor of the plaintiffs, and then told the court that Atlas had failed to serve the real owners and operators of Radaris and several of its sister data broker companies.

    Atlas re-filed the lawsuit in June 2025, this time dramatically expanding the number of Radaris family data brokers accused of violating Daniel’s Law. Matt Adkisson, president and CEO of Atlas, said Radaris turned to a tried-and-true playbook: Delaying in court until the last possible minute, and playing shell games with Radaris’s true country of origin and the individuals listed as owners and operators of these sites.

    “We refer to this period as their island-hopping phase. Privacy policies changed constantly, and new entities kept appearing from places like the Marshall Islands, the British Virgin Islands, and Seychelles,” Adkisson told KrebsOnSecurity. “Behind the scenes, it felt like a shell game. Defense lawyers told the court that certain entities merely operated the domains and were the proper parties to sue. But by the time a judgment neared, those entities would be discarded and new entities would appear. Meanwhile, the lawyers claimed the other entities that actually owned the domains should not be held responsible.”

    Adkisson said when the defendants updated their terms of service to state that Radaris was suddenly managed by a company in the Marshall Islands, Atlas hired an investigator in that country and soon learned the brand new entity that Radaris claimed was managing the company didn’t even exist yet.

    Mr. Gurvits stepped forward as Radaris’s attorney in a class action lawsuit the company temporarily lost in 2017 because it never contested the claim in court. When the plaintiffs told the judge they couldn’t collect on the $7.5 million default judgment, the court ordered the domain registry Verisign to transfer the radaris.com domain name to the plaintiffs.

    Mr. Gurvits appealed that verdict, arguing the lawsuit hadn’t named the actual owners of the Radaris domain name — a Cyprus company called Bitseller Expert Limited — and thus taking the domain away would be a violation of their due process rights.

    The judge in the 2017 case ruled in Radaris’ favor — halting the domain transfer — and told the plaintiffs they could refile their complaint. Soon after, the operator of Radaris changed from Bitseller to Andtop Company, an entity formed (PDF) in the Marshall Islands in Oct. 2020. The plaintiffs never re-filed their lawsuit.
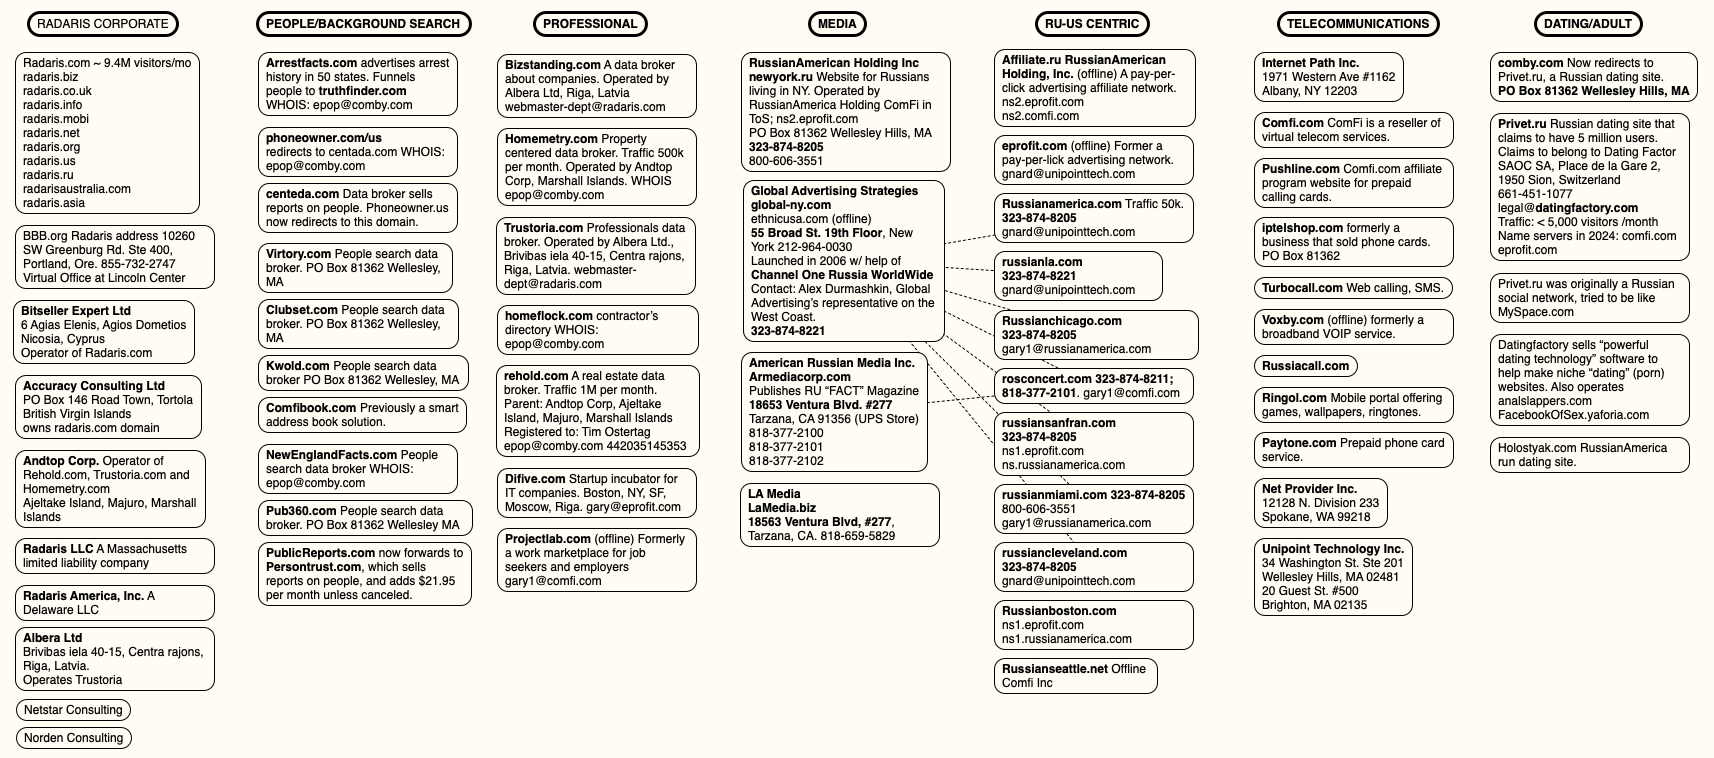
    A mind map of various entities tied to Radaris and the company’s co-founders. Click to enlarge.

    “That seemed to be their modus operandi,” said Raj Parikh, a partner at PEM Law in New Jersey who handles most of the Daniel’s Law litigation for Atlas. “In the past, they won by attrition. Plaintiffs’ attorneys tired of the procedural games and just gave up. That strategy worked for a decade, and it probably would have worked in this case too, since any financial recovery from foreign actors will be difficult. But we were acutely aware of the threat this website posed to law enforcement officers and other public officials in New Jersey, and decided early on to commit whatever time and resources were necessary to remove that threat.”

    On August 26, the judge in the New Jersey case found the defendants were given multiple chances to appear and defend the claims against them but had failed to do so. Mr. Gurvits declined to comment on the case, saying it had been assigned to another attorney, a Mr. Victor Worms. In response to questions, Mr. Worms asserted the New Jersey court transferred Radaris.com to Atlas as part of a default judgment against Radaris.com, which is not a legal entity.

    “We have made a motion to vacate that default judgment on the grounds that it is void since a non-entity has no legal capacity to sue or be sued,” Worms replied. “We also intend to pursue all appropriate appeals because we believe the transfer of Radaris.com amounts to a forfeiture in violation of various constitutional principles.”

    While radaris.com still comes up prominently in results when searching online for U.S. residents by name, the domain no longer sells detailed personal dossiers on millions of Americans. Its homepage now displays a notice from Atlas, as well as links to our previous reporting on Radaris.

    EMAIL CONFIRMATIONS

    Atlas told KrebsOnSecurity that it has obtained more than 10,000 emails and documents in the course of litigation, and that those messages confirm our previous reporting on the owners and operators of Radaris and its myriad companies.

    Atlas said the emails clearly establish that the nominal legal vehicles — Radaris America, Inc.; Bitseller Expert Limited; Digital Orbit Corp; Core Solutions Group Inc; Lucky Solutions Inc; Virtura Corp; Veripages Inc.; Nuform Solutions Inc.; Growth Data Advisors Inc.; Property Experts, Inc — are all administered by the same three or four people from the same mailboxes, share one bank or payment card set, and are all managed from one virtual office address.

    “The corpus establishes, with documentary evidence generated independently by banks, payment processors, hosting providers, registrars, software-as-a-service vendors and the operators’ own systems, that radaris.com and at least twenty-five other people-search websites are one operation run by a small Boston-area group whose administrative, financial and technical functions sit on the difive.com mail domain and its successors (centerex.com, scienteco.com, eprofit.com, realmo.com, pub360.com),” reads a summary shared by Atlas.

    Atlas said the emails show Radaris.com earns approximately $42,000 a month, while Veripages.com earns around $45,000 monthly via its partnership with the Lifetime Value Company, a marketing and advertising firm whose brands include PeopleLooker, PeopleSmart, NumberGuru, and Bumper, a car history site.

    According to Atlas, the emails also showed the Radaris family of websites earns as much as $25,000 each month from their partnership with Onerep, a company that claims to help people remove their information from people-search sites. In March 2024, KrebsOnSecurity revealed how the Belarusian founder of Onerep had launched and operated dozens of people-search sites over the years and was continuing to operate one of them (Nuwber), effectively spreading the disease and selling the cure.

    The domain radaris.com now redirects to this notice from Atlas about the court-ordered domain transfer.

    The domain radaris.com now redirects to this notice from Atlas about the court-ordered domain transfer.

    All told, the New Jersey court has so far transferred 14 domain names from the Radaris family of companies to Atlas. Radaris.com now redirects to a notice of the court-ordered domain transfer.

    THE ROAD AHEAD

    The Radaris family of companies is still potentially facing fines of $1,000 per alleged violation of Daniel’s Law. For the time being, however, Daniel’s Law is facing a constitutional challenge from virtually all of the 150 other consumer data broker firms being sued by Atlas.

    The data broker industry responded by having at least 70 of the Atlas lawsuits moved to federal court, challenging the New Jersey statute as overly broad and a violation of the First Amendment. The U.S. Court of Appeals for the Third Circuit has not yet issued a decision on the constitutional challenge, but either way the case is widely expected to be appealed all the way to the U.S. Supreme Court.

    Meanwhile, at least 14 other states have now passed laws modeled after the New Jersey statute, with more states considering similar measures. However, West Virginia’s Daniel’s Law was ruled facially unconstitutional under the First Amendment by a federal district court in August 2025.

    Justin Sherman is a privacy expert and author of the forthcoming book “The Middlemen,” which examines how the data broker industry powers modern surveillance. Sherman said federal lawmakers have long faced intense lobbying by the technology industry against more restrictive U.S. data privacy laws, but that many powerful industries are now working against passing comprehensive data privacy legislation.

    “These days at the federal level, add in the intense amount of lobbying against these laws from social media companies, big tech, cryptocurrency firms, and now AI proponents in the mix who claim that limiting their data scraping is somehow going to collapse the whole U.S. economy under Chinese rule,” he said.

    Sherman said people-search companies will continue to thrive unless and until Congress enacts meaningful consumer privacy and data protection laws that are relevant to life in the 21st century. That’s because virtually all state privacy laws exempt records that might be considered “public” or “government” documents, including voting registries, property filings, marriage certificates, motor vehicle records, criminal records, court documents, death records, professional licenses, bankruptcy filings, and more.

    At least 25 states have passed or implemented laws requiring age verification for residents seeking to access adult content online, but there is no federal law that limits how the companies that are scanning everyone’s drivers license can use, share or keep the data provided. Had such restrictions been enshrined in law, we may have avoided the recent breach at IDScan.net, which exposed the drivers license information on more than 153 million Americans when the records were briefly turned into a point-and-click identity theft service on the dark web.

    “The average person can look at Daniel’s Law and have a perfectly normal reaction, which is that everyone should be covered, not just police and judges,” Sherman said. “But we don’t need more wake-up calls. We’ve had eight million wake-up calls already on the need for better privacy laws. The lack of comprehensive federal privacy law is not for a lack of knowledge, and anyone claiming otherwise is either not reading the news or kidding themselves.”

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • NATIONAL HARBOR, Md.— The U.S. military’s top uniformed leader says U.S. forces must be ready for war near or possibly even on the moon, a rhetorical leap that comes as service leaders are still wrestling with the legal frameworks surrounding its newly revealed orbital weapons.

    “Our task, my friends, is to adapt right now, so the Joint Force is prepared to fight, endure, and win, in global contested environments, from the seabed to cislunar space,” Joint Chiefs Chairman Gen. Dan Caine told airmen, guardians, and industry figures during his keynote address at the Air, Space, and Cyber Conference.

    Caine later repeated the thought—“today’s modern battlefield operates from the seabed to cislunar space”—but he did not clarify whether he meant on the moon’s surface. U.S. law is ambiguous, defining cislunar space as “the region of space from the Earth out to and including the region around the surface of the moon.” At least one Harvard Law Journal article interprets the clause to mean on the moon itself, and the White House’s National Cislunar Science and Technology Action Plan explicitly said in late 2024 that it includes the lunar surface. But the Air Force Research Laboratory’s 2021 “Primer on Cislunar Space” appears to treat space and the moon’s surface as two different domains.

    Caine pointed to recent comments made about orbital weapons by the Air Force secretary and the Space Force’s chief of space operations. Top space force officials have been hesitant to provide more details on how they would operate in that domain and how they’d responsibly use space weapons in future conflicts.

    While top Space Force officials have provided few details about how U.S. forces would fight between the Earth and its moon, they have been vocal about adding sensors and capabilities to watch adversary movements there. Aaron Brynildson, a space law professor at the University of Mississippi said it’s understandable why the military would want to increase awareness within that region. 

    “There’s a fear that recent Chinese activity on the moon and in cislunar space might outpace the United States,” Brynildson said. “China has a relay satellite in cislunar space and is performing robotic missions on the far side of the moon.”

    The Outer Space Treaty of 1967, which the U.S. signed, outlaws certain military behaviors on the Moon and states that it shall be used “exclusively for peaceful purposes.” 

    “The establishment of military bases, installations and fortifications, the testing of any type of weapons and the conduct of military manoeuvres on celestial bodies shall be forbidden. The use of military personnel for scientific research or for any other peaceful purposes shall not be prohibited.”

    Space Force Lt. Gen. Gregory Gagnon, the head of Combat Forces Command, told reporters during a media roundtable that the 18th and 19th Space Defense Squadrons are now both sharing the cislunar mission among each other. 

    “Our adversaries, our potential adversaries, such as the PRC, are actively pursuing activities in the cislunar parts of space. So that's sort of the expansion, if you will, of I would say the end zone, if you will, in the football game,” he said.

    When asked if the Outer Space Treaty limits the military’s cislunar ambitions, Gagnon said it did not limit orbital operations.

    “The United States Space Force will continue to execute safe and responsible space operations in all regions of space and in all orbits,” he said.

    Brynildsonn said that while the treaty forbids the creation of military bases on the moon, “The U.S. needs better capabilities in cislunar space to ensure China complies with that obligation and doesn’t militarize the moon. There’s a real coverage gap by the U.S. that needs closing.”

    This week’s revelation by Air Force Secretary Troy Meink and Chief of Space Operations Gen. Douglas Schiess that the U.S. has on-orbit space-control weapons has raised legal questions about their responsible use. Experts have speculated that the weapons are likely non-kinetic, such as jammers and electronic warfare capabilities.

    When asked whether U.S. policy limits the use of a kinetic space weapon, meaning a destructive capability that would cause debris, Gagnon deferred to policy offices. 

    “So we have capabilities in the military because we are preparing to defend the nation. The reason we have capabilities is to help create deterrence,” he said. “When you go to war, you break things.”

    Brynildson said it’s not clear how current laws limit the use of space weapons.

    “It’s unclear what the legal restraints on the use of kinetic or non-kinetic weapons in space might be. The Outer Space Treaty doesn’t give us great answers to what factors a military action must consider,” he said. “The DoD Law of War Manual is also non-committal on the unique aspects of the space domain. At a minimum, general principles from the law of armed conflict would apply, such as only striking military-related satellites, avoiding collateral damage to civilians, etc.”

    U.S. lawmakers are also concerned by the lack of space-focused military legal knowledge. A provision inserted by the Senate Armed Service Committee in the 2027 National Defense Authorization Act tasks the Defense Department with assessing its “space law requirements” to face rising threats and examine “options for establishing a dedicated legal organization within the Air Force, Space Force, or Space Command.” The amendment adds that senators are “concerned that current legal, policy, and institutional structures within the Department of Defense may not have kept pace with the complexity of space operations.”

    Those clarified legal norms may not emerge until it’s too late.

    “Ultimately, I think the first space conflict might be the time when most of these rules get written,” Brynildson said.

    ]]>

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A critical security flaw in Issabel Framework, a web-based framework for the open-source unified communications PBX software, has come under active exploitation. The vulnerability in question is CVE-2026-89026 (CVSS v3.1 score: 9.8/CVSS v4.0 score: 9.3), which can allow an unauthenticated remote attacker to execute arbitrary operating system (OS) commands by taking advantage of a hard-coded

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Enterprises in Russia have emerged as the target of three threat activity clusters tracked as NightEagle, Hacking Cat, and Toy Ghouls, according to multiple reports from Kaspersky. The cybersecurity vendor said it has identified attacks mounted by NightEagle (aka APT-Q-95), a threat actor known to be active since at least 2023, that involve new techniques for persistence and lateral movement.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Security researchers at Forever Security have shown that one ordinary browser extension could take control of the AI assistants built into five Chromium-based products: Gemini Live in Chrome, Perplexity Comet, Microsoft Edge, Opera Neon and the Claude in Chrome extension. Once the extension was installed, it could access each product’s built-in AI with a single click. On Comet, Edge,

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A newly identified device-code phishing kit dubbed GhostCode exploits Microsoft Entra device enrollment to maintain access after stolen tokens are revoked. GhostCode begins with business-email social engineering rather than a conventional credential-harvesting page. Operators impersonated procurement staff from legitimate organizations, including BJ’s Wholesale Club, and submitted benign inquiries through Salesforce contact forms. Once a sales […]

    The post GhostCode Abuses Microsoft Entra Device Enrollment to Maintain Access After Token Revocation appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Mandiant says an attacker hijacked an active AI coding-assistant session at an unnamed software-as-a-service provider and later spread Shai-Hulud across about 100 internal code repositories. Before the repository spread, the assistant recommended software that the attacker had poisoned, and the recommendation was accepted. The worm stole repository secrets and source code for the

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • This week in cybersecurity from the editors at Cybercrime Magazine

    Sausalito, Calif. – Sep. 16, 2026

    – Listen to the Podcast

    Silk Road 2.0 was a dark web marketplace launched in Nov. 2013, approximately five weeks after the FBI shut down the original Silk Road and arrested its founder, Ross Ulbricht.

    Blake Benthall is the former operator of the infamous dark web marketplace. Operating under the pseudonym “Defcon,” Benthall spent a year building and expanding Silk Road 2.0 until his arrest by the FBI in Nov. 2014. After time in solitary confinement and eight months in a federal detention center, he spent many years cooperating with the FBI’s Cyber Division on high-profile cases.

    Benthall, now CEO and founder at Fathom(x), a blockchain analysis and risk mitigation company based in Houston, Texas, joins host Cybercrime Magazine Podcast host Scott Schober to discuss his experience, arrest, and journey to where he is today.

    Listen to the Podcast Episode


    Cybercrime Magazine is Page ONE for Cybersecurity. Go to any of our sections to read the latest:

    • SCAM. The latest schemes, frauds, and social engineering attacks being launched on consumers globally.
    • NEWS. Breaking coverage on cyberattacks and data breaches, and the most recent privacy and security stories.
    • HACK. Another organization gets hacked every day. We tell you who, what, where, when, and why.
    • VC. Cybersecurity venture capital deal flow with the latest investment activity from various sources around the world.
    • M&A. Cybersecurity mergers and acquisitions including big tech, pure cyber, product vendors and professional services.
    • BLOG. What’s happening at Cybercrime Magazine. Plus the stories that don’t make headlines (but maybe they should).
    • PRESS. Cybersecurity industry news and press releases in real time from the editors at Business Wire.
    • PODCAST. New episodes daily on the Cybercrime Magazine Podcast feature victims, law enforcement, vendors, and cybersecurity experts.
    • RADIO. Tune into WCYB Digital Radio at Cybercrime.Radio, the first and only round-the-clock internet radio station devoted to cybersecurity.

    Contact us to send story tips, feedback and suggestions, and for sponsorship opportunities and custom media productions.

    The post Blake Benthall aka “Defcon”, Former Operator of Silk Road 2.0, Tells His Story appeared first on Cybercrime Magazine.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Parallels Desktop for Mac has a flaw that lets an ordinary local account run code as root, the highest level of access on a Mac, software company JFrog said this week. The attack needs code already running on the machine as a normal user, so it does not work over the network. JFrog says the fix is in Parallels Desktop 27, a version that Intel Macs cannot install. Yuval Moravchick, who leads

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • VectraRAT, a previously undocumented Malware-as-a-Service platform that combines remote-access trojan capabilities with automated credential theft and a silent Windows privilege-escalation chain. Unlike the large number of commodity RATs that recycle leaked AsyncRAT, XWorm, or QuasarRAT code, VectraRAT appears to be a purpose-built, full-stack product maintained by a single developer. The platform is rented rather than […]

    The post VectraRAT Malware-as-a-Service Lets Hackers Bypass UAC and Hijack Windows Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶