• Ransomware operators have shifted from opportunistic malware distribution to highly targeted campaigns that exploit legitimate software for stealth and persistence.

    Emerging in early 2025, several ransomware families began abusing popular remote access tools—such as AnyDesk and Splashtop—to establish footholds within enterprise networks.

    By hijacking or silently installing these utilities, adversaries bypass security controls that traditionally trust signed installers, enabling initial access without tripping conventional detection mechanisms.

    Organizations rapidly discovered anomalous remote sessions connecting from unexpected geolocations.

    Seqrite analysts identified that attackers leveraged credential stuffing and phishing to obtain privileged accounts, then deployed remote access tools to move laterally.

    Rather than relying solely on custom malware binaries, threat actors used existing administration frameworks to blend malicious activity into everyday IT operations, rendering their actions practically invisible to legacy endpoint protections.

    The impact of these campaigns has been profound. Victims report encrypted file shares, disabled backups, and altered Remote Access Tool credentials to lock out administrators.

    In high-profile intrusions attributed to LockBit and Black Basta variants, attackers combined RAT abuse with file-shredding commands to eradicate forensic traces, extend dwell time, and maximize ransom demands.

    Organizations suffered costly downtime and data loss, underscoring the urgency of reevaluating trust in routine IT utilities.

    Persistence Tactics of Remote Access Tool Abuse

    A critical enabler of these ransomware operations is the attackers’ ability to maintain persistent control through run-of-the-mill remote administration software.

    Two primary methods emerged: hijacking preinstalled tools to avoid file creation and deploying lightweight installers via command-line flags.

    In the hijacking scenario, adversaries enumerate installed applications through Windows Management Instrumentation or PowerShell, then inject malicious credentials or modify JSON configuration files to grant unattended access under the attacker’s account.

    This approach leaves no new executables on disk and evades antivirus scanning by abusing trusted executables already whitelisted in enterprise policies.

    When opportunistic targets lack preexisting remote access utilities, attackers fall back on silent installation.

    Using known installer parameters, they deploy signed binaries with minimal noise:-

    Start-Process -FilePath '.\AnyDesk.exe' -ArgumentList 'INSTALL=C','STARTWITHWINDOWS=1','SILENT=1' -NoNewWindow

    This command installs AnyDesk as a service that launches at boot, granting the adversary persistent entry points for follow-on operations.

    Similar flags—such as VERYSILENT and NORESTART—are documented in vendor manuals yet rarely monitored by defenders.

    Once embedded, the remote tool runs with elevated privileges if attackers escalate via utilities like TrustedInstaller or PowerRun.

    Combined with registry run-key manipulation and hidden scheduled tasks, this chain ensures that even if an incident responder removes one backdoor, a secondary access path remains.

    This layered persistence model frustrates remediation efforts and demands a shift toward behavior-based monitoring that flags anomalous tool usage rather than file signatures.

    By abusing trusted remote administration software, ransomware gangs have turned IT convenience into their most potent weapon.

    Defenders must implement strict application whitelisting, enforce multi-factor authentication, and monitor command-line arguments associated with common remote access tools to detect and disrupt these stealthy persistence tactics before encryption can occur.

    Follow us on Google News, LinkedIn, and X to Get More Instant Updates, Set CSN as a Preferred Source in Google.

    The post Ransomware Gangs Leverage Remote Access Tools to Gain Persistence and Evade Defenses appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A novel and alarming cybersecurity threat has emerged, turning an ordinary computer peripheral into a sophisticated eavesdropping device.

    Researchers have detailed a new technique, dubbed the “Mic-E-Mouse” attack, which allows threat actors to exfiltrate sensitive data by exploiting the high-performance optical sensors found in many modern computer mice.

    This method can covertly capture and reconstruct user speech, opening a new frontier for auditory surveillance. The vulnerability stems from the ever-increasing sensitivity and polling rates of optical sensors in consumer-grade mice.

    These advanced sensors, often found in gaming or high-performance models, can detect minute surface variations thousands of times per second.

    The Mic-E-Mouse attack capitalizes on this by using the sensor to pick up microscopic vibrations that travel through a desk or work surface when a person speaks.

    In effect, the mouse becomes a makeshift microphone, capturing the acoustic environment around it.

    The Attack Pipeline

    While a mouse sensor can detect these vibrations, the raw signal it produces is of extremely poor quality. A high noise floor, non-uniform sampling, a non-linear frequency response, and extreme quantization heavily distort it.

    To overcome these significant challenges, the researchers developed a sophisticated pipeline of signal processing and machine learning techniques.

    Mic-E-Mouse Attack Pipeline
    Mic-E-Mouse Attack Pipeline

    The Mic-E-Mouse pipeline works in several stages. First, malicious software on the victim’s computer collects the high-frequency mouse movement data (Δx, Δy, and Δt).

    This data collection process is designed to be invisible to the average user. Once collected, the data can be exfiltrated and processed offline by the attacker.

    The pipeline then applies advanced algorithms to filter the noise, correct the distortions, and ultimately reconstruct an intelligible audio waveform from the compromised mouse data.

    The effectiveness of this method is striking. When tested against the VCTK and AudioMNIST speech datasets, the pipeline achieved a Signal-to-Interference-plus-Noise Ratio (SI-SNR) increase of +19dB, demonstrating a significant improvement in audio clarity.

    Furthermore, automated tests demonstrated an 80% accuracy in speaker recognition, and a human study yielded a Word Error Rate (WER) of 16.79%, indicating that the reconstructed speech is highly comprehensible.

    Threat Model and Delivery

    The researchers outlined a practical threat model for deploying this attack. The ideal delivery vehicle is open-source software, particularly applications where the collection of high-frequency mouse data is not inherently suspicious.

    This makes video games, creative software, and other high-performance, low-latency applications prime targets for injecting the malicious data-gathering code.

    Threat Model and Delivery
    Threat Model and Delivery

    An attacker could compromise such an application, and once it’s running on a victim’s computer, it would begin collecting the mouse sensor data.

    Many video games already contain networking code that the exploit can repurpose to exfiltrate the collected data without raising suspicion from security software.

    After the initial collection, all subsequent processing and analysis can be performed on the adversary’s own systems at any time.

    The growing accessibility and affordability of vulnerable hardware magnifies the threat. High-fidelity mice are already available for under $50, and as technology improves, their prices are expected to drop further.

    This trend will lead to the increased use of vulnerable mice by consumers, corporations, and government entities, dramatically expanding the attack surface for this type of surveillance.

    Researchers note that most human speech falls within the 200Hz to 2000Hz frequency range, which their pipeline can successfully detect and reconstruct.

    This new research demonstrates that auditory surveillance through high-performance optical sensors is not just a theoretical possibility, but an effective and efficient threat.

    Cyber Awareness Month Offer: Upskill With 100+ Premium Cybersecurity Courses From EHA's Diamond Membership: Join Today

    The post New Mic-E-Mouse Attack Let Hackers Exfiltrate Sensitive Data by Exploiting Mouse Sensors appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • In recent months, security researchers have turned their attention to Asgard Protector, a sophisticated crypter employed by cybercriminals to obfuscate and deploy malicious payloads.

    First advertised on underground forums in late 2023, Asgard Protector has gained traction among threat actors for its seamless integration with popular C2 platforms such as LummaC2.

    By wrapping infostealers and remote access trojans within seemingly benign installers, Asgard Protector undermines traditional antivirus defenses and complicates incident response efforts.

    The toolkit typically arrives as a Nullsoft self-extracting archive that, upon execution, unpacks several hidden components into the temporary directory.

    SpyCloud analysts noted that this installer disguises its batch script with mismatched file extensions—for example, renaming a .bat file to Belgium.pst—and employs obfuscation techniques to hide its true purpose.

    Once extracted, the installer assembles an AutoIt interpreter binary in memory, leveraging pieces from embedded CAB archives to reconstruct the executable before launching the next stage.

    SpyCloud analysts identified additional layers of evasion within the embedded AutoIt scripts. Encrypted payloads are stored inside the script and only decrypted in memory using an RC4 routine.

    The script then decompresses the binary using the LZNT1 algorithm before performing a process injection into explorer.exe, effectively hiding the malicious process under a trusted system host.

    Asgard Protector ad, which appeared on XSS (Source – SpyCloud)

    A unique sandbox-detection mechanism further complicates analysis: the script issues a ping to a randomly generated domain and exits if any response is received, indicating a monitored or emulated network environment.

    After this unpacking and validation, the malicious payload gains persistence by modifying autorun registry keys or deploying scheduled tasks, depending on the operator’s configuration.

    The combination of in-memory decryption, compression, and sandbox checks enables Asgard Protector to slip past endpoint defenses and execute without dropping a traditional executable on disk.

    Infection Mechanism

    Delving deeper into the infection mechanism reveals how Asgard Protector engineers its defense evasion.

    The Nullsoft installer script leverages a simple yet effective obfuscation:-

    findstr /b /r /c:"MZ" *.dat > offset.txt
    for /f "tokens=1" %%A in (offset.txt) do set /A start=%%A
    certutil -decode input.cab temp.exe
    fsutil file createnew stub.bin %start%
    more +%start% input.cab >> stub.bin
    The obfuscated .bat file used by Asgard Protector for installation (Source – SpyCloud)

    In this snippet, the script locates the “MZ” header within a CAB archive to determine where the PE header begins.

    It then concatenates the extracted data past that offset to reconstruct the AutoIt binary. Once assembled, the script executes a companion AutoIt script that handles RC4 decryption and LZNT1 decompression before injecting the resulting payload into memory.

    This piecemeal assembly and execution model allows the malware to evade signature-based antivirus engines and thwart disk-based inspection tools.

    Follow us on Google News, LinkedIn, and X to Get More Instant Updates, Set CSN as a Preferred Source in Google.

    The post Researchers Reversed Asgard Malware Protector to Uncover it’s Antivirus Bypass Techniques appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A widespread campaign observed exploiting a novel zero-day vulnerability in Oracle E-Business Suite (EBS) applications, now tracked as CVE-2025-61882. 

    First observed on August 9, 2025, this unauthenticated remote code execution (RCE) flaw is being weaponized to bypass authentication, deploy web shells, and exfiltrate sensitive data from internet-exposed EBS instances. 

    CrowdStrike assesses with moderate confidence that the threat actor GRACEFUL SPIDER is behind the mass exploitation, although evidence suggests additional actors may be involved.

    Mass Exploitation Campaign 

    On September 29, 2025, GRACEFUL SPIDER allegedly sent Clop-branded emails to multiple organizations claiming successful data theft from Oracle EBS applications. 

    Shortly after the October 3, 2025 proof-of-concept (POC) disclosure and Oracle’s patch release, a Telegram channel post hinted at collaboration between SCATTERED SPIDER, SLIPPY SPIDER, and the ShinyHunters group. 

    The post included a purported EBS exploit with SHA256 hash 76b6d36e04e367a2334c445b51e1ecce97e4c614e88dfb4f72b104ca0f31235d and criticized GRACEFUL SPIDER’s tactics. 

    Oracle’s advisory incorporated this PoC as an indicator of compromise (IOC), implying vendor concerns over in-the-wild exploitation.

    CrowdStrike connects activity leveraging Java Servlets for initial compromise, indicating the POC aligns closely with observed intrusions. 

    Despite ongoing investigation into the exploit’s provenance and distribution, the timing of public POC release and patch deployment is likely to spur further weaponization by adversaries familiar with Oracle EBS.

    The exploit begins with an HTTP POST request to /OA_HTML/SyncServlet, triggering the authentication bypass. Confirmed incidents show adversaries leveraging administrative account privileges within EBS. 

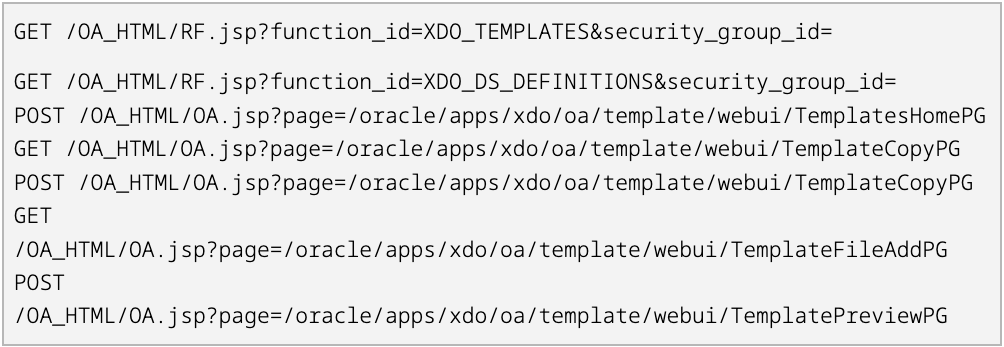
    Following bypass, attackers target the XML Publisher Template Manager via GET /OA_HTML/RF.jsp and POST /OA_HTML/OA.jsp to upload a malicious XSLT template. 

    Commands embedded in the template execute upon preview, which captures sample GET and POST requests used to upload and preview the payload. 

    Template names retrieved from the xdo_templates_vl view correspond to TemplateCode URL references.

    Successful template execution establishes an outbound Java process connection over port 443 to the attacker-controlled infrastructure. 

    Analysis indicates this channel is used to load web shells, often via a two-step process: loading FileUtils.java to download a secondary backdoor Log4jConfigQpgsubFilter.java. 

    The backdoor engages through a doFilter chain at the public endpoint /OA_HTML/help/state/content/destination./navId.1/navvSetId.iHelp/, enabling command execution and persistence.

    CrowdStrike Intelligence emphasizes that CVE-2025-61882 presents a significant remote code execution (RCE) risk to Oracle EBS environments.

    Organizations are urged to apply the October 4, 2025, patch immediately, audit outbound connections for suspicious activity, review xdo_templates_vl for unauthorized templates, investigate icx_sessions for UserID 0 and UserID 6 anomalies, and deploy web application firewalls to protect exposed EBS services. 

    Monitoring for Java process behaviors consistent with published Falcon LogScale and SIEM detection rules can further mitigate ongoing exploitation risks.

    Cyber Awareness Month Offer: Upskill With 100+ Premium Cybersecurity Courses From EHA's Diamond Membership: Join Today

    The post CrowdStrike Warns of New Mass Exploitation Campaign Leveraging Oracle E-Business Suite 0-Day appeared first on Cyber Security News.
    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • References to a 2019 law that guarantees back pay to all federal workers after a shutdown were quietly removed from guidance by the Office of Management and Budget on Friday.

    Until Oct. 3, OMB’s "Frequently Asked Questions During a Lapse in Appropriations" document highlighted the Government Employees Fair Treatment Act, the 2019 law enacted as part of the deal to end the 35-day partial government shutdown during President Trump’s first term. Signed into law by Trump, the law requires back pay for furloughed and excepted federal workers after government funding is restored after “any lapse in appropriations that begins on or after December 22, 2018.” Until the law’s passage, Congress had to OK back pay for furloughed workers after each lapse. 

    “All excepted employees are entitled to receive payment for their performance of excepted work during the period of the appropriations lapse when appropriations for such payments are enacted,” stated the document, which was updated Sept. 30 before this year's shutdown began. “The Government Employee Fair Treatment Act of 2019 (Public Law 116-1) provides that upon enactment of appropriations to end a lapse, both furloughed and excepted employees will be paid retroactively as soon as possible after the lapse ends, regardless of scheduled pay dates.”

    But the latest version of the document omits the latter sentence and references to OPM guidance on the topic. That removal is the only change between the two document versions, aside from the date.

    OPM’s shutdown guidance, last updated Sept. 28, still says that furloughed workers will receive back pay after the shutdown.

    “After the lapse in appropriations has ended, employees who were furloughed as the result of the lapse will receive retroactive pay for those furlough periods,” OPM wrote. “Retroactive pay will be provided on the earliest date possible after the lapse ends, regardless of scheduled pay dates.”

    After Government Executive asked the White House about the change on Monday evening, Axios on Tuesday reported that senior administration officials were developing guidance that furloughed federal workers are not entitled to back pay. The White House officials said it would take a novel interpretation of the back pay law and argue it applied only to the 2019 shutdown.  

    More than 620,000 employees are currently furloughed, a number that will continue to climb as the shutdown drags on.  

    Sen. Chris Van Hollen, D-Md., who helped write the 2019 back pay measure and shepherd it into law with then-Sen. Ben Cardin, D-Md., said the language of the statute left no room for interpretation. 

    “The law is the law," Van Hollen said. "After the uncertainty federal employees faced in the 2019 Trump Shameful Shutdown, Sen. Cardin and I worked to ensure federal employees would receive guaranteed back pay for any future shutdowns. That legislation was signed into law—and there is nothing this administration can do to change that.”

    Sen. Tim Kaine, D-Va., threatened legal action if the Trump administration follows through on its newly minted legal interpretation.

    "I was proud to work across the aisle in 2019 to pass legislation that President Trump himself signed to guarantee backpay to federal workers in the event of a shutdown," Kaine said. "If OMB chooses thuggish intimidation tactics over following the law, it better prepare to face the American people in court." 

    Matt Biggs, national president of the International Federation of Professional and Technical Engineers, described OMB’s decision to remove reference to the law “highly suspicious.”

    “The Federal Employee Fair Treatment Act is bipartisan law that has been in effect since 2019, and one that passed the House overwhelmingly with only seven no votes, passed the Senate on a voice vote without a single senator raising a concern, and was signed by President Trump,” he said. “Despite the OMB director’s clear disdain for our federal workforce, he can’t unilaterally ignore a law that overwhelmingly passed both chambers of Congress and was signed by President Trump himself. The OMB needs to stop playing games with the livelihoods of federal workers and their families.”

    ]]>

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent alert regarding a critical zero-day vulnerability in Oracle E-Business Suite that cybercriminals are actively exploiting to deploy ransomware attacks against organizations worldwide. The vulnerability, tracked as CVE-2025-61882, poses an immediate threat to enterprises running Oracle’s widely-used business management software. Critical Vulnerability Enables Complete System […]

    The post CISA Alerts on Oracle E-Business Suite 0-Day Actively Exploited for Ransomware Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The WARMCOOKIE backdoor first surfaced in mid-2024, delivered primarily via recruiting-themed phishing campaigns that coaxed victims into executing malicious documents.

    Initially designed as a lightweight implant for remote command execution, its modular codebase enabled rapid adaptation to new objectives.

    Over the past year, targets have included enterprise networks across multiple regions, with operators exploiting malvertising and spam campaigns to seed infections.

    These intrusions have allowed threat actors to maintain persistent footholds, steal credentials, and deploy secondary payloads.

    Elastic Security Labs analysts identified ongoing updates to WARMCOOKIE’s infrastructure and code family shortly after the initial disclosure.

    By mid-2025, the backdoor was implicated in Europol’s Operation Endgame, yet infections persisted through revamped delivery mechanisms.

    While earlier variants relied on hardcoded folder paths and static mutex names, recent builds leverage dynamic string banks and dual GUID-style mutexes for improved stealth.

    Beyond simple command handlers, the malware now incorporates new capabilities to launch executables, DLLs, and PowerShell scripts on demand.

    Each command type is routed through a unified function that writes the payload into a temporary directory before execution, either by invoking rundll32.exe for DLLs or PowerShell.exe for scripts.

    This expansion broadens WARMCOOKIE’s utility as a flexible loader, accommodating custom modules without altering the core binary.

    Infection Mechanism

    WARMCOOKIE’s infection mechanism has evolved to evade static detection and complicate incident response.

    Upon execution, the backdoor parses a configuration blob embedded within its resource section, decrypting fields such as the Remote Command and Control (C2) URL, RC4 key, and a campaign identifier.

    The decryption routine resembles the following pseudocode:-

    DWORD seed = GetTickCount();
    srand(seed);
    int index = rand() % STRING_BANK_SIZE;
    char *path = string_bank[index];
    desStringDecrypt(dword14001B620, buffer, bufferSize);

    This snippet illustrates how WARMCOOKIE seeds its random number generator with the system uptime, selects a legitimate-looking folder name from a dynamic list, and decrypts campaign parameters at runtime.

    The campaign ID field, introduced in later versions, enables operators to tag infections with distribution context—such as “traffic2”—facilitating granular tracking of victim sets.

    After decryption, the malware establishes persistence by creating a scheduled task whose name and executable path mirror recognized software vendors drawn from the same string bank.

    This shows a sample scheduled task entry where the task name and folder path reference a legitimate IT services company name.

    Scheduled task using string bank (Source – Elastic)

    By randomizing folder names and task identifiers, WARMCOOKIE avoids repeating known artifacts across samples, complicating signature-based detection.

    In parallel, dual GUID-style mutexes regulate initialization sequences, ensuring only a single instance runs and mitigating race conditions during startup.

    Collectively, these enhancements underscore the attackers’ emphasis on resilience and evasion, reinforcing WARMCOOKIE’s position as a persistent threat to enterprise environments.

    Follow us on Google News, LinkedIn, and X to Get More Instant Updates, Set CSN as a Preferred Source in Google.

    The post Threat Actors Behind WARMCOOKIE Malware Added New Features to It’s Arsenal appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A security issue in the Kibana CrowdStrike Connector allows attackers to access stored CrowdStrike credentials. The flaw affects multiple versions of Kibana and can expose credentials across spaces within the same deployment. Elastic has released updates to resolve this issue and urges users to upgrade immediately. Vulnerability Details The flaw, tracked as CVE-2025-37728, arises from […]

    The post Kibana CrowdStrike Connector Flaw Exposes Sensitive Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Cisco has released advisories for a zero-day exploit chain affecting its Secure Firewall Adaptive Security Appliance (ASA) and Secure Firewall Threat Defense (FTD) software, which is reportedly being used in highly targeted attacks by an unknown threat actor.

    According to Rapid7, the exploit chain combines two vulnerabilities, CVE-2025-20362 and CVE-2025-20333, to achieve unauthenticated remote code execution (RCE) on vulnerable devices.

    A third vulnerability, CVE-2025-20363, was also patched, but evidence suggests only the first two are actively used in the attack chain.

    The core of the issue lies within the clientless VPN (WebVPN) feature, allowing an attacker to bypass authentication and then trigger a memory corruption flaw.

    The Two-Stage Exploit Chain

    The attack begins with CVE-2025-20362, an authentication bypass vulnerability caused by a path traversal flaw. This vulnerability allows an unauthenticated, remote attacker to access restricted URL endpoints that should normally require authentication.

    The flaw is a variant of a previously discovered vulnerability, CVE-2018-0296. Attackers can exploit this by sending a specially crafted HTTP request, such as CSCOU...CSCOE, to the device’s web server.

    This bypasses security checks and grants access to authenticated endpoints, setting the stage for the second part of the attack. A successful bypass can be identified if the server responds with “CSRF token mismatch” or “Failed to upload file”.

    Once authentication is bypassed, the attacker leverages CVE-2025-20333, a buffer overflow vulnerability within the WebVPN feature’s file upload handling process.

    This flaw, classified as CWE-120 (Buffer Copy without Checking Size of Input), is located in a Lua script that processes file uploads. Specifically, the script fails to validate the size of the “boundary” value in an HTTP request.

    By sending a request with a boundary string larger than the allocated 8192-byte buffer, an attacker can overflow it by calling the HTTPCONTENTTOBUFFER function with a length greater than the buffer’s capacity.

    This memory corruption can be triggered via the CSCOEfilesfileaction.html endpoint, which becomes accessible due to the initial authentication bypass, according to Rapid7 analysis.

    Mitigations

    The successful chaining of these two vulnerabilities results in unauthenticated RCE, giving an attacker complete control over an affected Cisco firewall.

    The exploit is non-trivial but has been confirmed to be active in the wild, leading to system crashes and reboots on vulnerable devices. The vulnerability is due to improper validation of user-supplied input in HTTP(S) requests.

    Both Cisco ASA and FTD software are affected when the clientless VPN (WebVPN) portal is enabled. Cisco has released patched software versions, including ASAv version 9.16.4.85, to address these critical vulnerabilities.

    Administrators are strongly urged to update their systems immediately to prevent potential exploitation.

    Follow us on Google News, LinkedIn, and X for daily cybersecurity updates. Contact us to feature your stories.

      The post Cisco ASA/FTD 0-Day Vulnerability Exploited for Authentication Bypass – PoC Released appeared first on Cyber Security News.

      ¶¶¶¶¶

      ¶¶¶¶¶

      ¶¶¶¶¶

      ¶¶¶¶¶

      ¶¶¶¶¶

    1. An extortion group calling itself Crimson Collective claimed responsibility for a major breach at Red Hat Consulting. With only 22 followers on Telegram at the time, the group’s rapid rise to notoriety has stunned security experts. By the end of that day, Red Hat confirmed the breach and began notifying affected clients. Red Hat Consulting […]

      The post Red Hat Breach Impacts 5,000+ High-Value Enterprise Customers, Data at Risk appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

      ¶¶¶¶¶

      ¶¶¶¶¶

      ¶¶¶¶¶

      ¶¶¶¶¶

      ¶¶¶¶¶